The Hill Cipher: Why You Keep Getting Stuck on the Math and How to Fix It
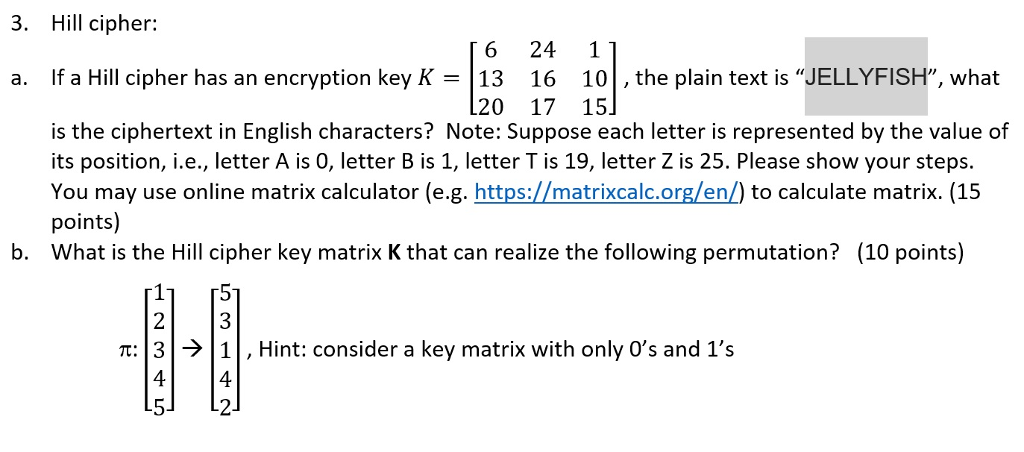
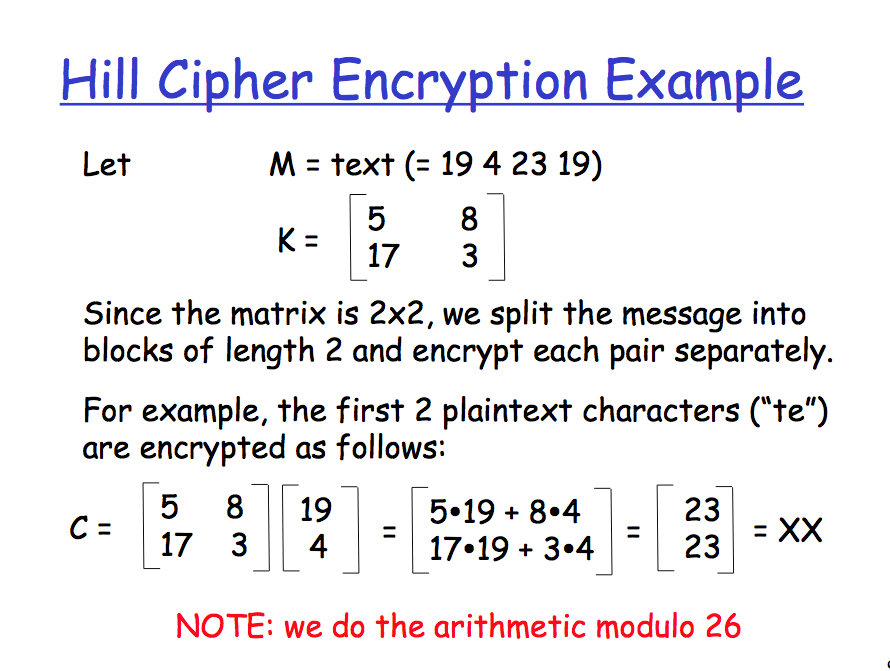
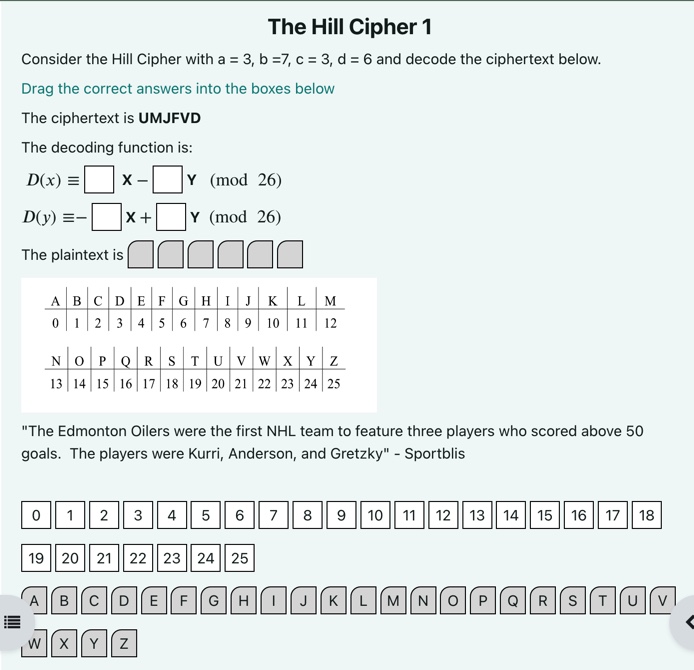
I've been digging through Hill Cipher questions and answers on forums for years, and almost everyone hits the same wall. They can spell out the theory, but the moment they try to actually compute a decryption or pick a valid key matrix, everything falls apart. Here's what's going wrong and how to get it right. The cipher works by taking your plaintext, converting each letter to a number (A = 0, B = 1, and so on), grouping those numbers into vectors the same size as your key matrix, and then multiplying. Encryption is just matrix-vector multiplication modulo 26. Decryption reverses it by multiplying with the inverse of the key matrix modulo 26. The part nobody gets right the first time is the modular inverse. You can't just flip the determinant and call it a day. The determinant needs to have a modular multiplicative inverse modulo 26, which means gcd(det, 26) must equal 1. If your determinant is even, or if it's a multiple of 13, your matrix has no valid inverse and you're dead in the water. I wasted an afternoon once debugging a Python script that kept throwing a "matrix has no modular inverse" error, only to realize my randomly generated 3x3 key matrix had a determinant of 52. 52 is divisible by both 2 and 13, so of course it failed. The workaround was simply writing a validation function that checked gcd(det, 26) == 1 before ever attempting encryption.
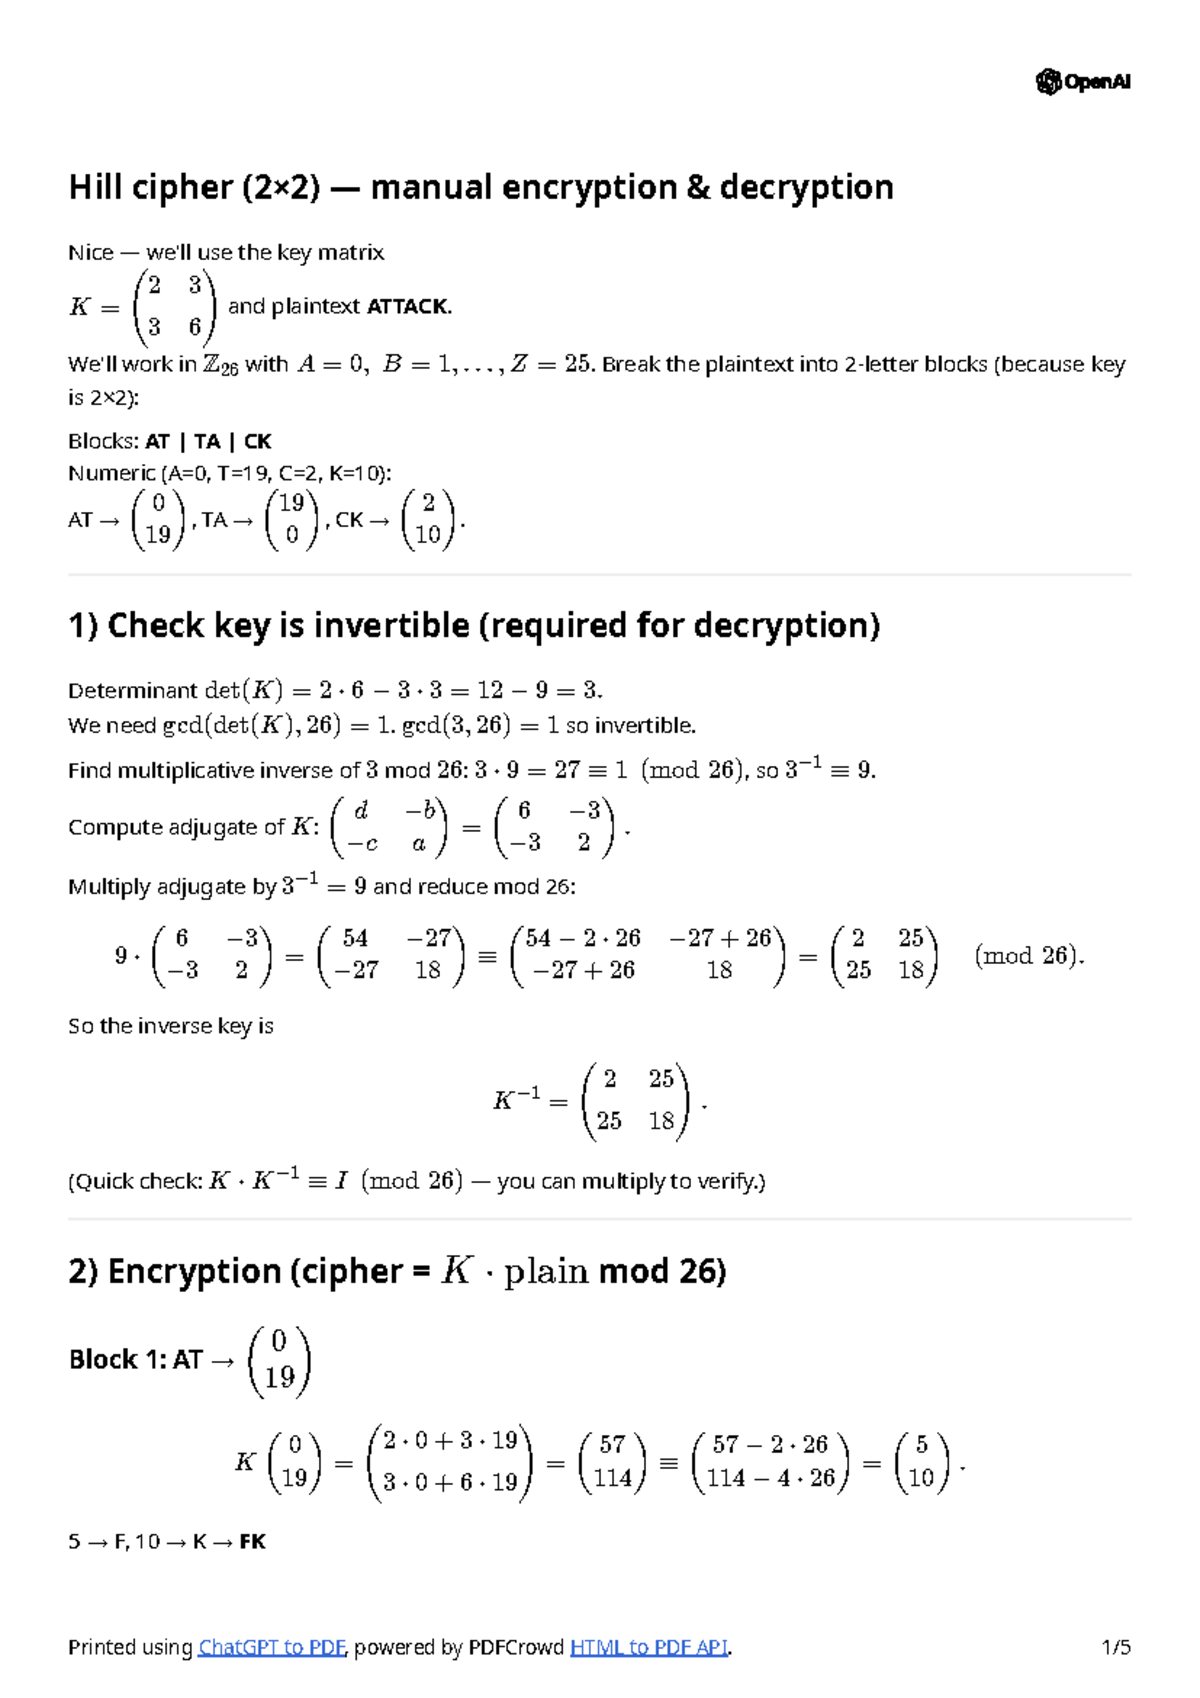
Here's a straightforward example with a 2x2 matrix. Let your key be: K = [[3, 3], [2, 5]] The determinant is (3 × 5) - (3 × 2) = 15 - 6 = 9. gcd(9, 26) = 1, so we're good. The modular inverse of 9 modulo 26 is 3, since 9 × 3 = 27 1 (mod 26). The adjugate matrix is [[5, -3], [-2, 3]], and reducing the negatives modulo 26 gives [[5, 23], [24, 3]]. Multiply everything by 3 and take mod 26 again, and your decryption key comes out to [[15, 18], [20, 9]]. Test it by multiplying K times K^(-1) mod 26 and you should get the identity matrix.
Plaintext "HELLO" becomes [7, 4, 11, 11, 14]. Pad it to an even length with a trailing Z (25), giving you two column vectors: [7, 4] and [11, 11] and [14, 25]. Multiply each by K mod 26 and convert back to letters. That's the full pipeline. A lot of people also miss that the Hill Cipher is vulnerable to known-plaintext attacks, and not in some obscure academic way. If an attacker knows even a short piece of plaintext and its corresponding ciphertext, they can set up a system of linear equations and solve for the key matrix directly. A 2x2 key only requires four known plaintext-ciphertext character pairs, and a 3x3 key needs nine. This is textbook material but it still surprises people who treat Hill Cipher as anything close to secure for real-world use. It isn't. It was never meant to be. It was designed to show that polygraphic substitution was feasible with linear algebra, not to build a production cipher. One thing beginners consistently overlook is padding. If your message length isn't divisible by the matrix dimension, you have to pad it. Common approaches use a null character like Z, or you can append a fixed padding scheme. The problem is that weak padding schemes can leak information. If you always pad with Zs, an analyst can sometimes infer message boundaries or shorten the effective search space. I've seen implementations that just silently drop characters that don't fit the block size instead of padding them, which corrupts the decrypted output in ways that are painful to debug because the error doesn't manifest until the very end of the text.
Get the Full Details
Another practical detail: modular arithmetic in programming languages handles negative numbers inconsistently. In Python, -3 % 26 gives 23, which is correct. In C or Java, -3 % 26 can give -3, which breaks your entire calculation chain if you're not careful. Always add the modulus before taking the remainder if you're working in a language where the modulo operator preserves sign. This tripped me up in a C implementation and took me longer than I want to admit to track down because every intermediate result looked fine when printed. If you're looking for something to work with, most university cryptography courses provide Hill cipher exercises with answer keys online. You can also find reference implementations in Python on GitHub or academic sites. The math itself is straightforward linear algebra with a modular twist. The pitfalls are all in the details — invalid key matrices, padding mishandling, negative modular results, and a fundamental overestimation of what this cipher can actually protect. Use it for learning. Don't use it for anything that matters.