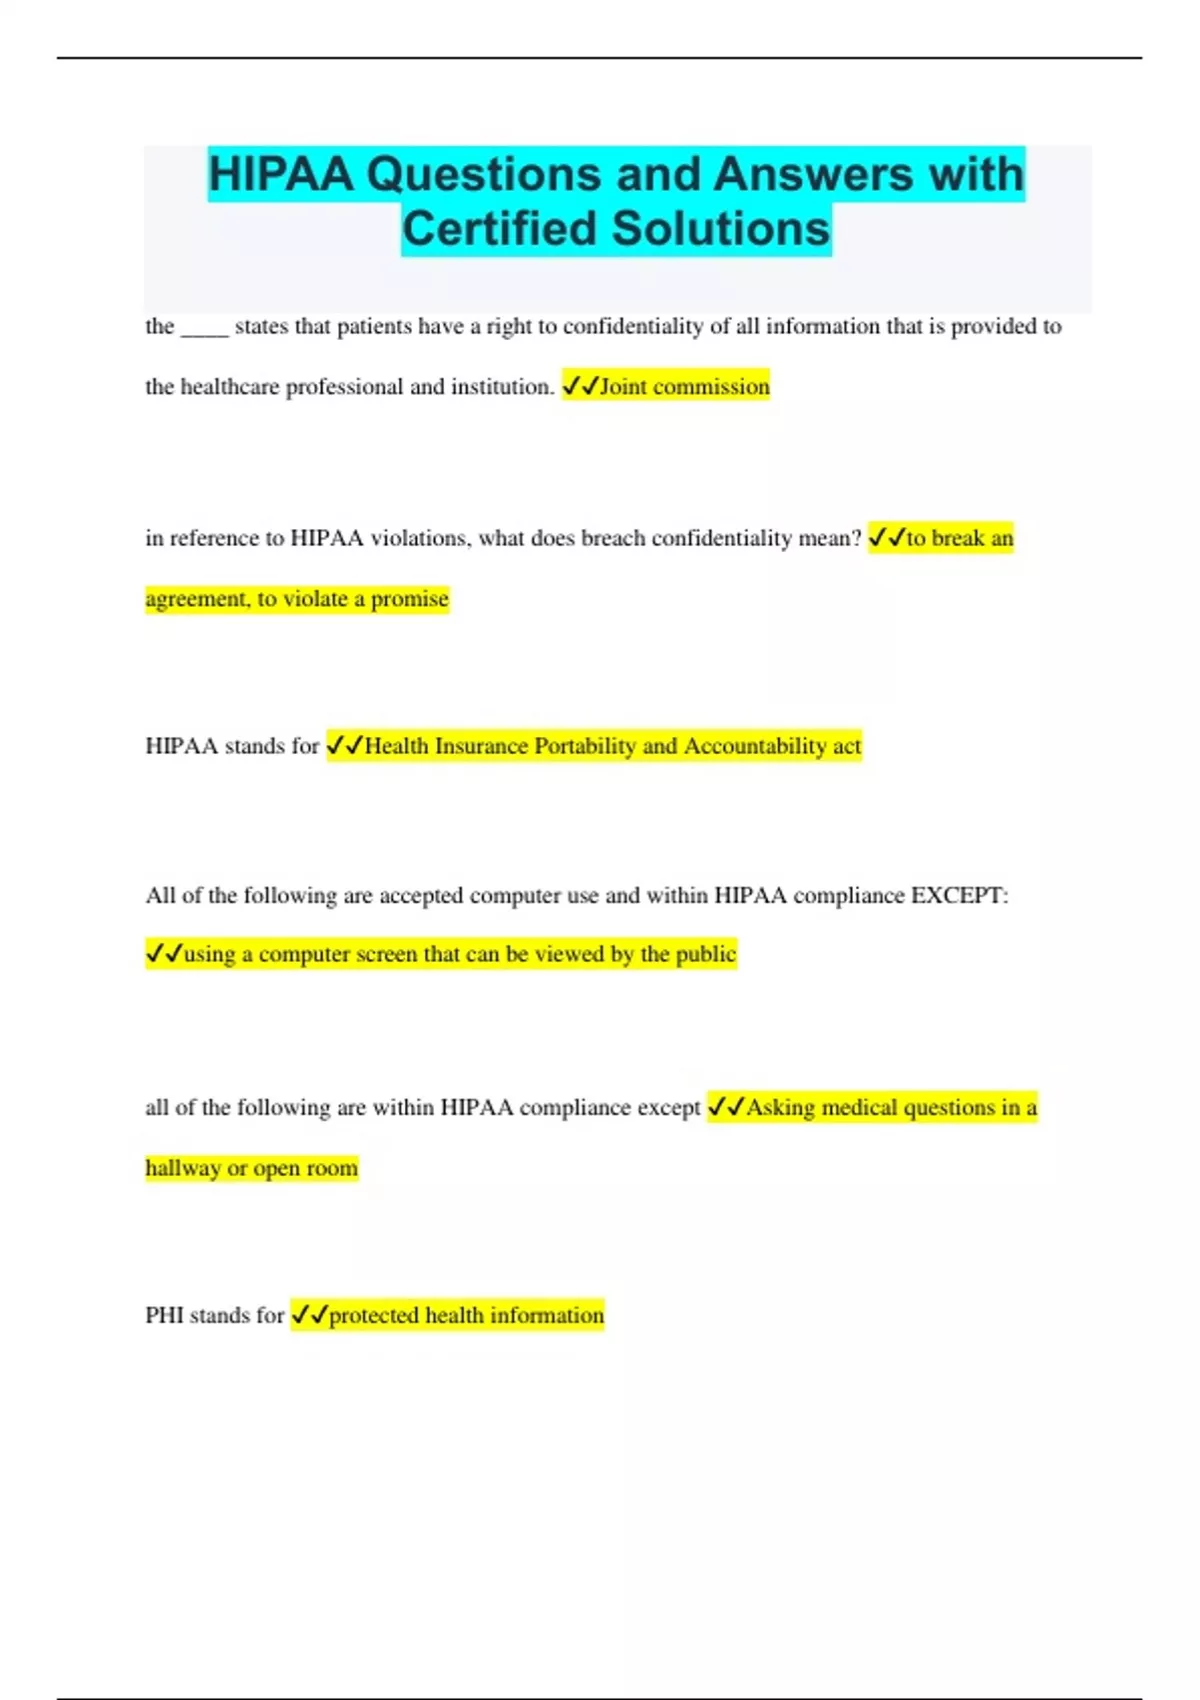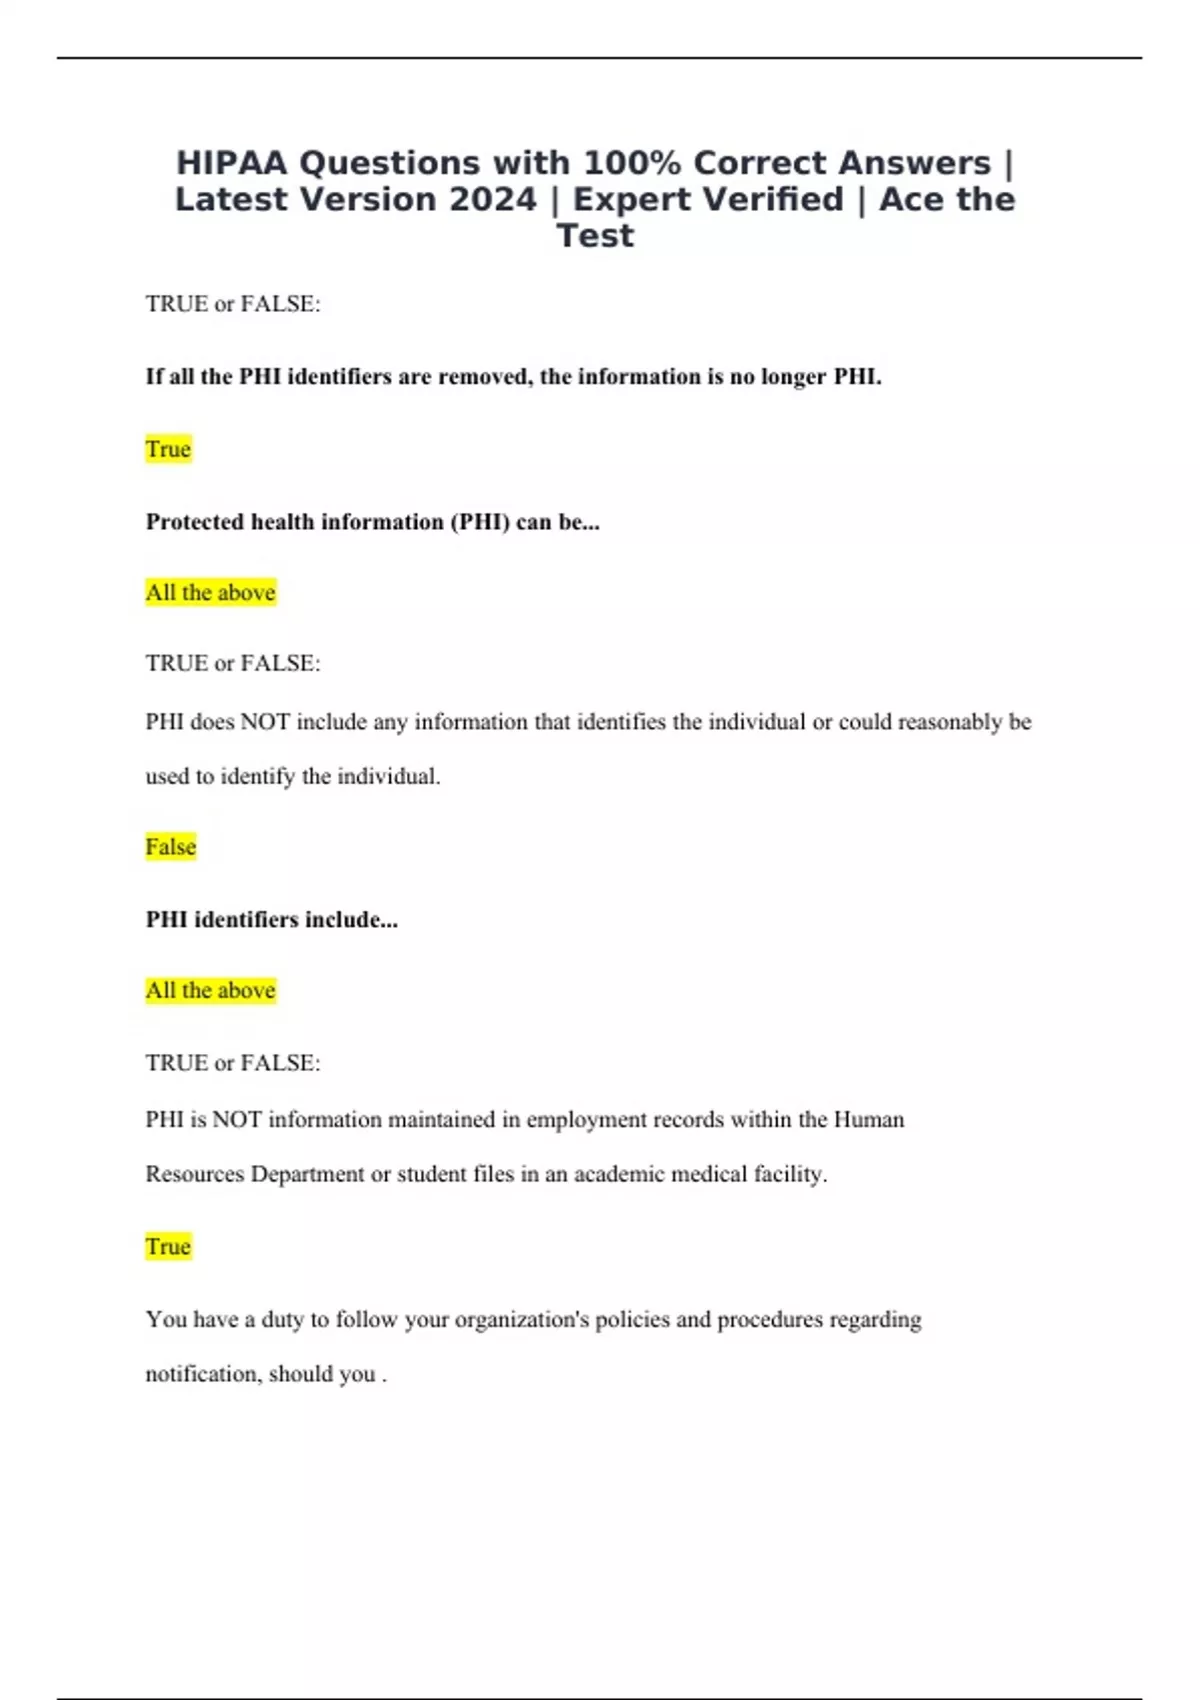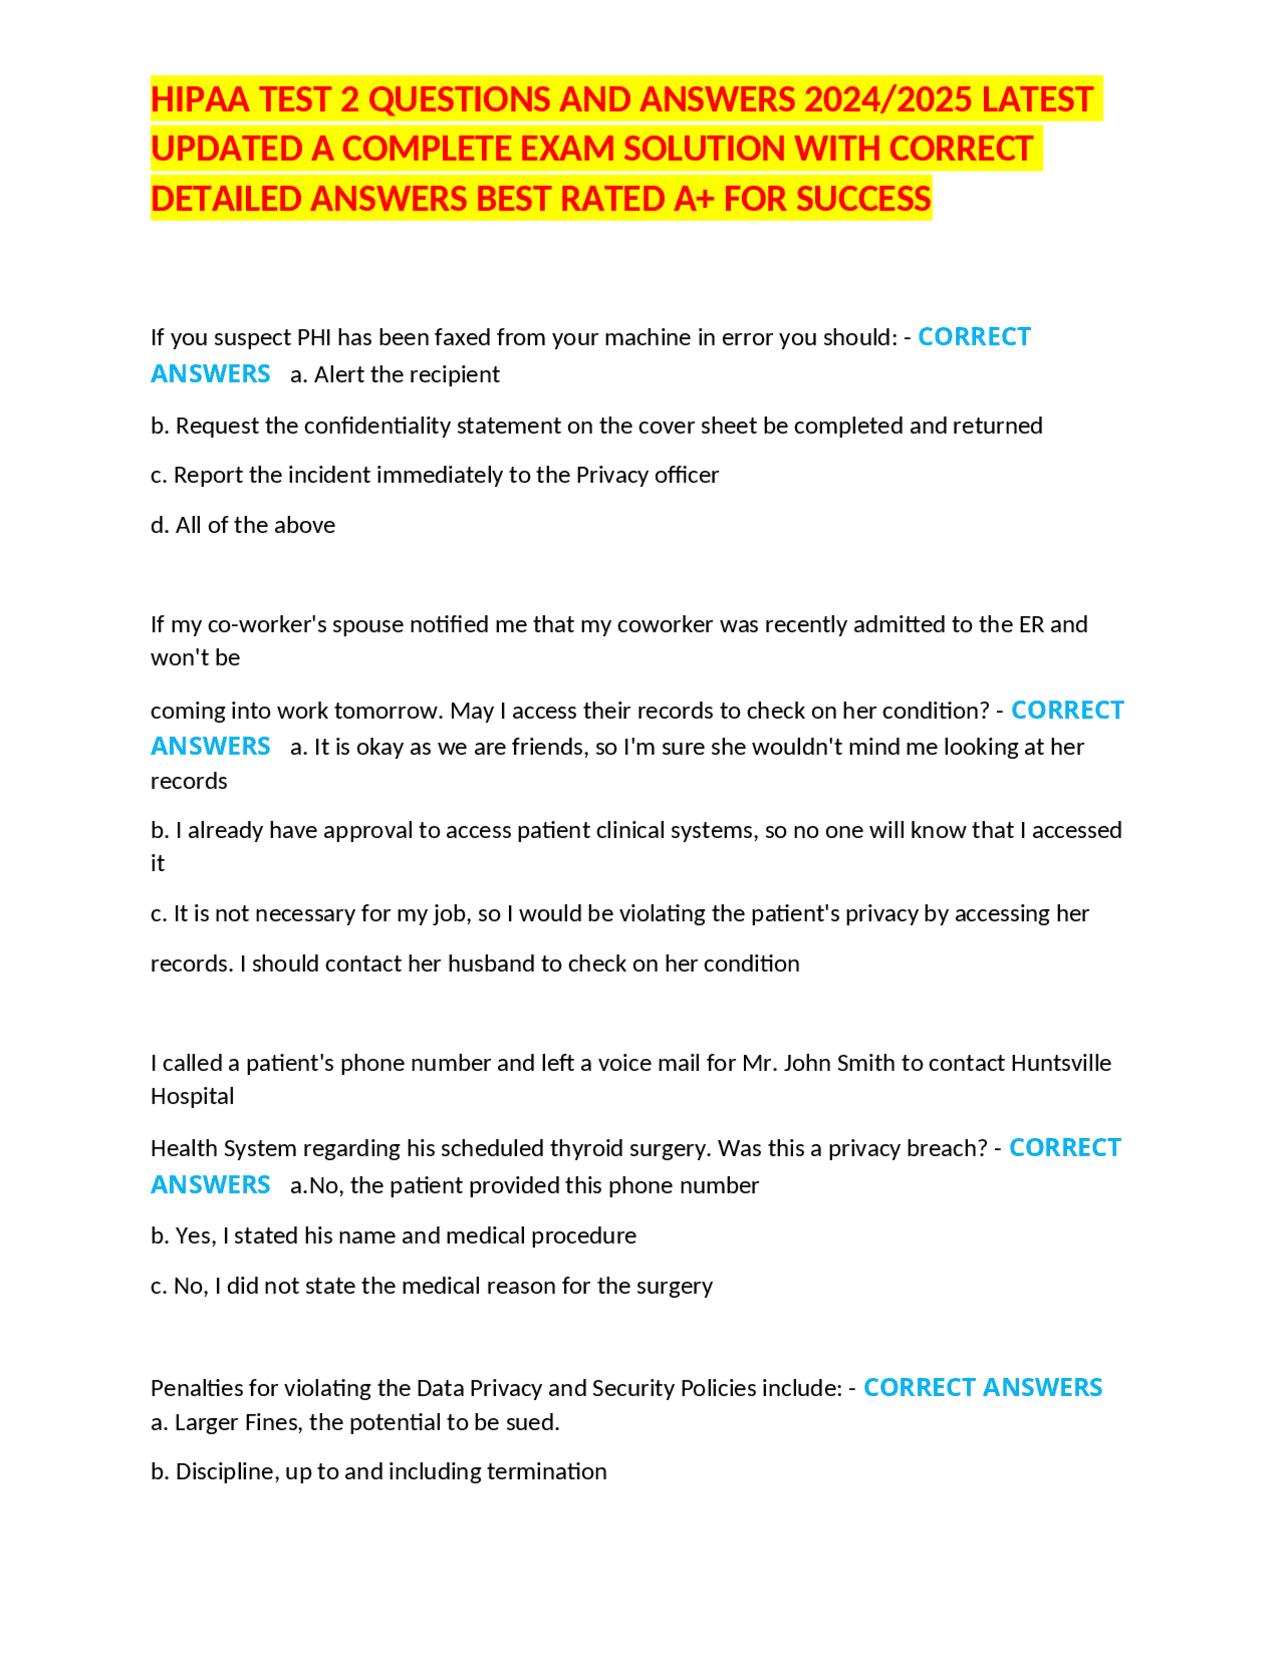
What HIPAA Training Assessments Actually Look Like
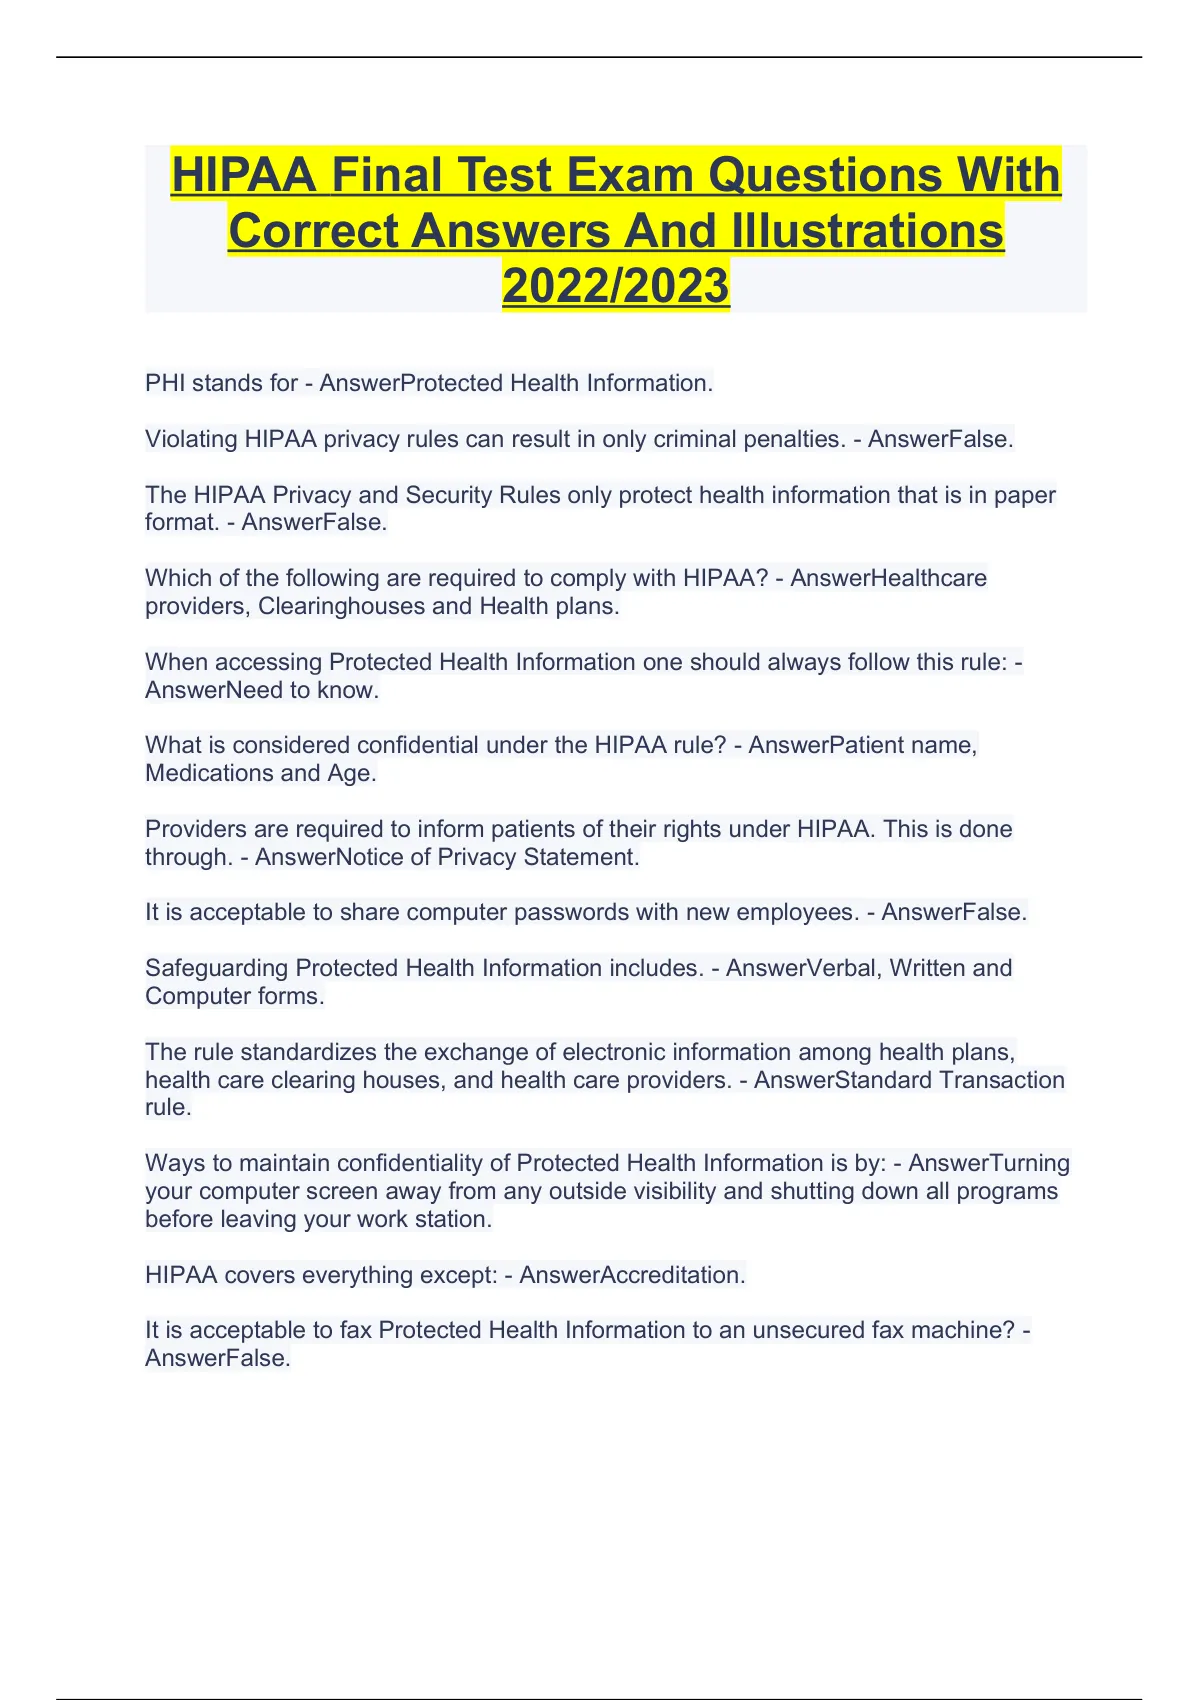
Most organizations build their own question banks rather than buying off-the-shelf ones. That is just how it works when you are dealing with regulators who care about outcomes, not procurement receipts. The core of a HIPAA test covers the Privacy Rule, the Security Rule, breach notification requirements, and sanctions for violations. Anything beyond that tends to be padding. Here is a realistic set that mirrors what most covered entities use internally. I compiled these from real audit prep sessions and organizational training programs over the years. Q1: What is the primary purpose of the HIPAA Privacy Rule?
A: To establish national standards for protecting individually identifiable health information while allowing the flow of information needed for quality healthcare and appropriate accountability. Q2: Which of the following is NOT a permitted use of PHI under the Privacy Rule without patient authorization? A: Marketing purposes. Treatment, payment, and healthcare operations are the standard permitted uses. Marketing requires explicit authorization unless it falls under the very narrow facilities directories exception.
Q3: What does the Security Rule specifically address that the Privacy Rule does not? A: Electronic PHI (ePHI). The Privacy Rule covers all forms of PHI. The Security Rule is limited to electronic protected health information and mandates administrative, physical, and technical safeguards. Q4: A nurse checks a celebrity's medical record out of curiosity. Which violation has occurred?
Get the Full Details
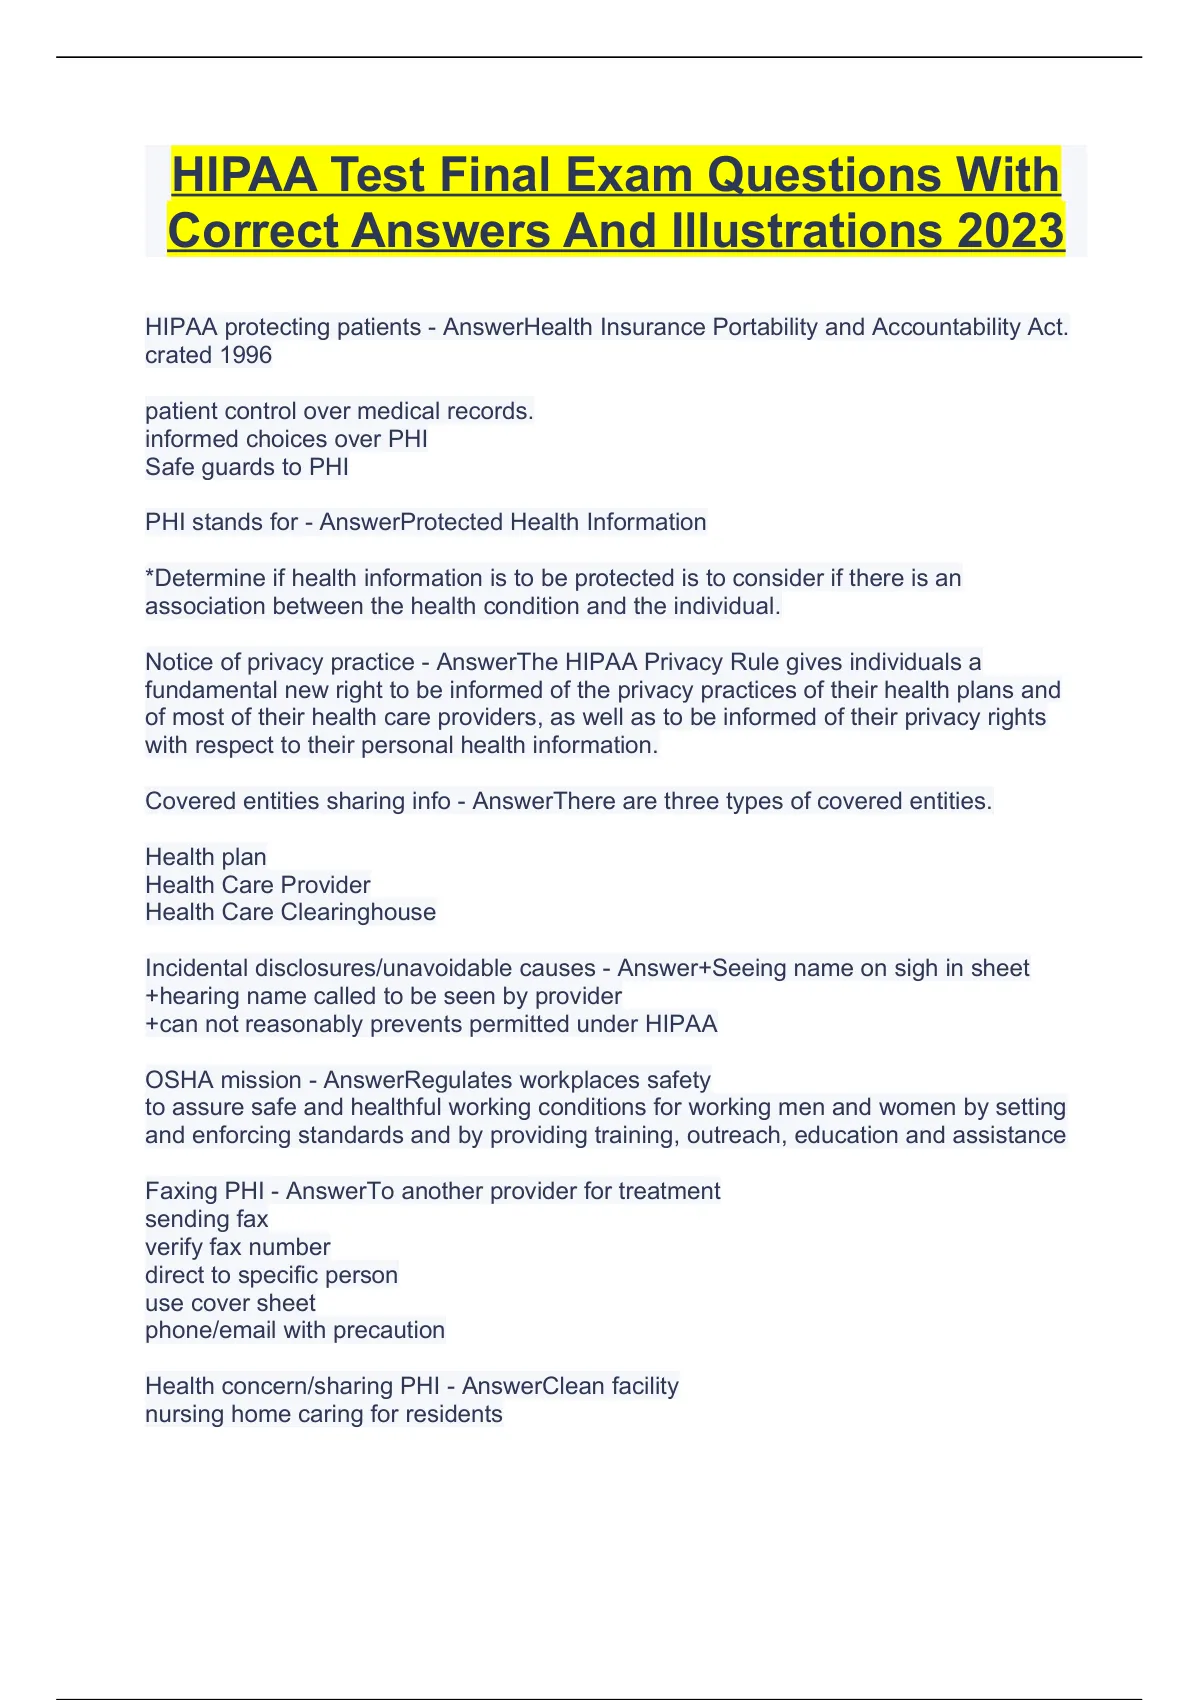
A: Unauthorized access to PHI. Lack of a treatment, payment, or operations justification makes this a clear Privacy Rule violation regardless of whether the information was shared further. Q5: How soon must a covered entity notify individuals after discovering a breach of unsecured PHI? A: Without unreasonable delay and in no case later than 60 days from discovery. This is a hard deadline in the Breach Notification Rule.
Q6: What constitutes a "minimum necessary" standard? A: Making reasonable efforts to limit PHI access and disclosure to the minimum information needed to accomplish the intended purpose. It applies to requests by other workforce members, business associates, and external parties, with exceptions for healthcare providers sharing PHI for treatment purposes. Q7: When does the 500-patient threshold trigger different breach notification requirements?
A: If a breach affects 500 or more individuals, the covered entity must notify the Secretary of HHS immediately and provide prominent notice to the media. Breaches affecting fewer than 500 individuals only require annual logging and notification within 60 days. Q8: What is the difference between a required and a permissible safeguard under the Security Rule? A: Required safeguards are mandatory and must be implemented. Addressable safeguards require the entity to evaluate whether they are reasonable and appropriate for their situation. If not reasonable, the entity must document why and implement an equivalent alternative measure. This distinction trips up a lot of people during audits.
How to Build Your Own Assessment
Don't rely on free online dumps. They are often outdated, inaccurate, or misaligned with your specific organizational policies. A proper assessment ties directly back to your written policies and procedures. Start by mapping each question to a specific section of your policy manual. If you cannot find a policy reference for a question, that question does not belong on your test. I once spent three weeks trying to figure out why an auditor flagged our entire training program. The issue was not the content. It was that our questions referenced a 2017 version of our acceptance of risk analysis policy while we had since updated it to reflect the 2021 OCR guidance. The answers were technically correct for the old policy but wrong for the current one. The fix was straightforward: version-stamp every question with the policy edition it references and run a quarterly cross-check. This takes about 45 minutes if you have your documents indexed properly.
Common Mistakes People Make
The biggest one is treating compliance testing as a checkbox exercise. Passing a quiz does not mean your workforce understands HIPAA. It means they can select the right bubble on a multiple-choice form. I have seen organizations where the average test score was 94 percent and a random audit still found PHI left on desks, shared via unencrypted email, and discussed in public elevator areas. The disconnect between test performance and actual behavior is real and well-documented. Another mistake is using the same test for everyone. A receptionist, a billing coder, and a network administrator should not get identical questions. Their access to PHI and their respective risks are completely different. Role-based testing cuts irrelevant questions in half and makes the assessment actually measure something meaningful. The third mistake is forgetting that the Security Rule requires an ongoing risk analysis, not a one-time event. Your test questions should evolve when your threat landscape changes. If you started using a new cloud EHR platform last year, your Security Rule questions should reflect that change. Static question banks become obsolete within 18 to 24 months.
Where to Find Legitimate Reference Material
The HHS OCR website publishes the full text of the Privacy Rule, Security Rule, and Breach Notification Rule. That is your source of truth. The HIPAA Journal and Medscape also maintain updated compliance guides. For question format guidance, HHS has published sample training materials, though they are intentionally generic and not sufficient as a standalone assessment tool. There are commercial platforms like ComplyRx, HIPAATracker, and SprintByte that offer curated question banks and automated tracking. They are useful if you lack internal compliance staff, but budget accordingly. These platforms typically run between $2,000 and $8,000 annually depending on organization size and feature requirements. If you want a practical starting point, take the HHS online training course at hs.gov and adapt its quiz questions to your specific policies. That approach gives you accuracy, alignment, and zero licensing cost. It also ensures that when an auditor asks how your test was developed, you have a defensible paper trail showing the derivation path from federal guidance to your customized assessment.
The bottom line is that HIPAA test quality matters more than test quantity. Thirty well-aligned questions beat one hundred generic ones every time. Focus on your actual risks, tie every question to a written policy, and update at least annually. That is what keeps auditors satisfied and, more importantly, keeps patient data from becoming a headline.