Setting Up an IAM System That Doesn't Break Everything
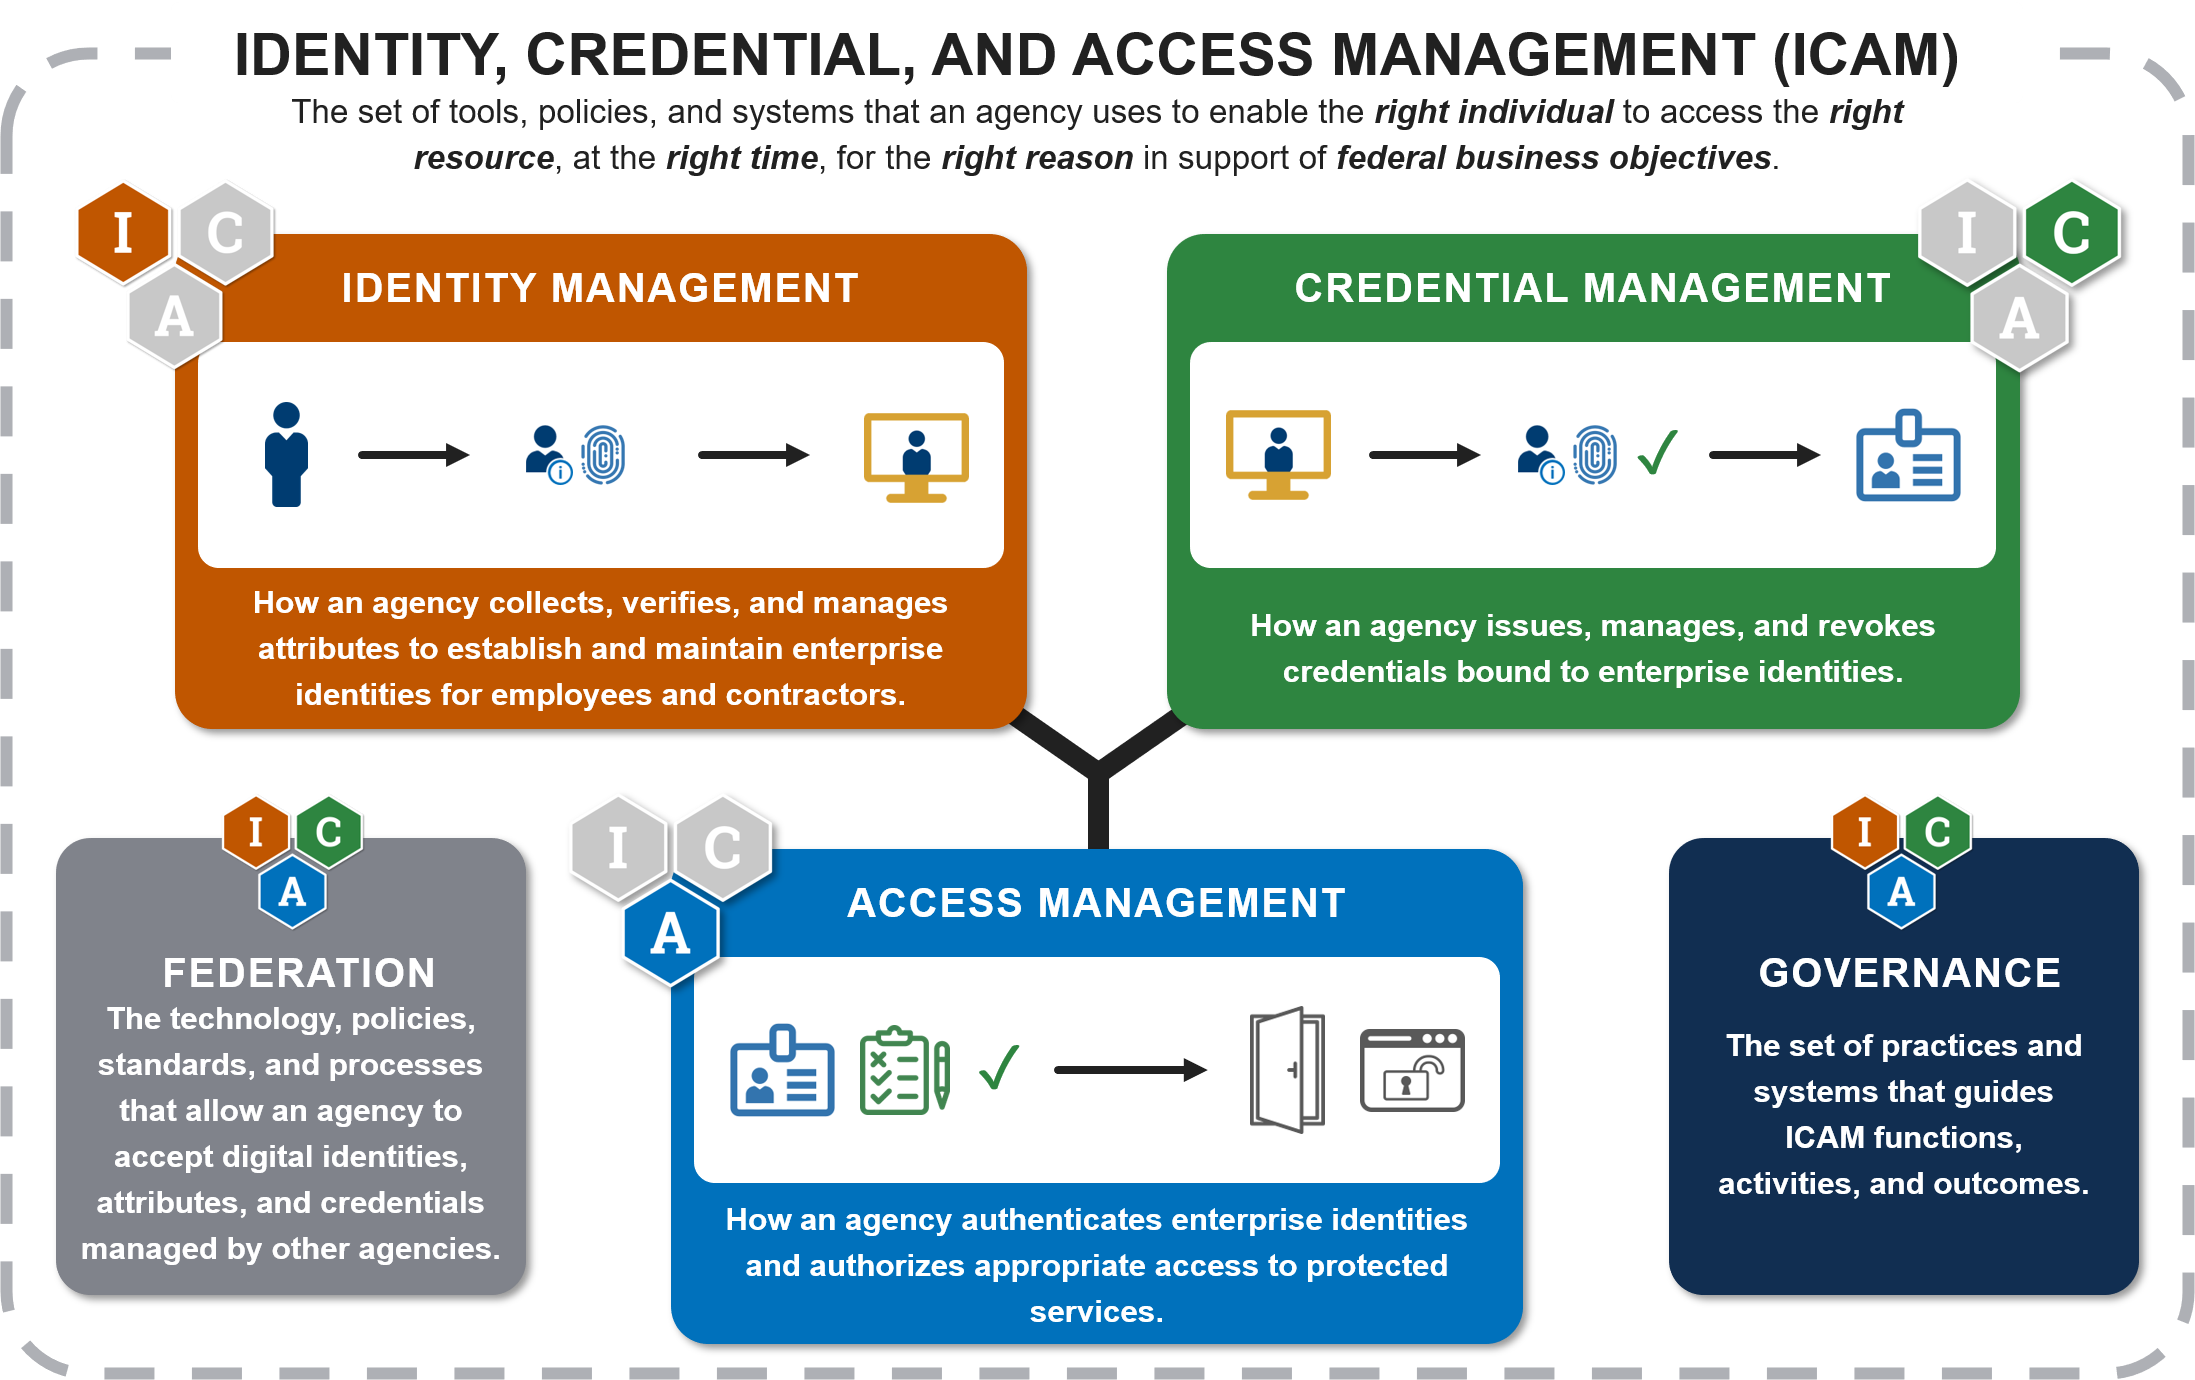
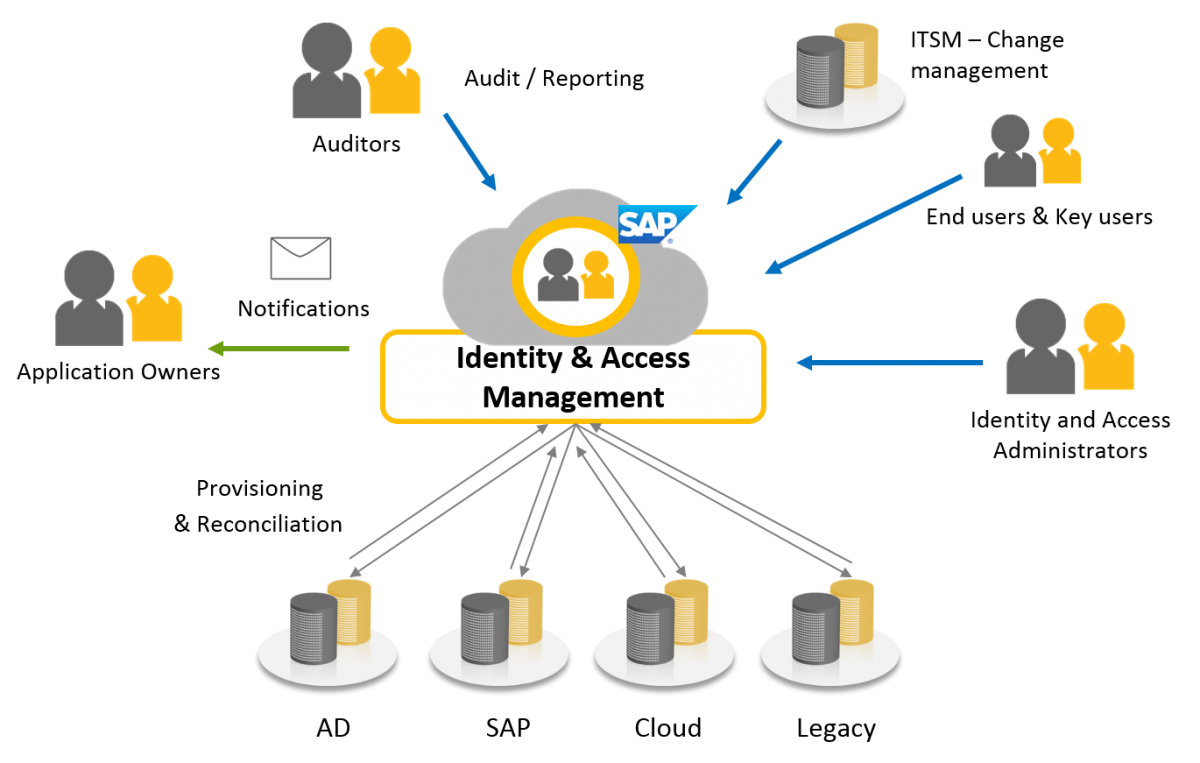
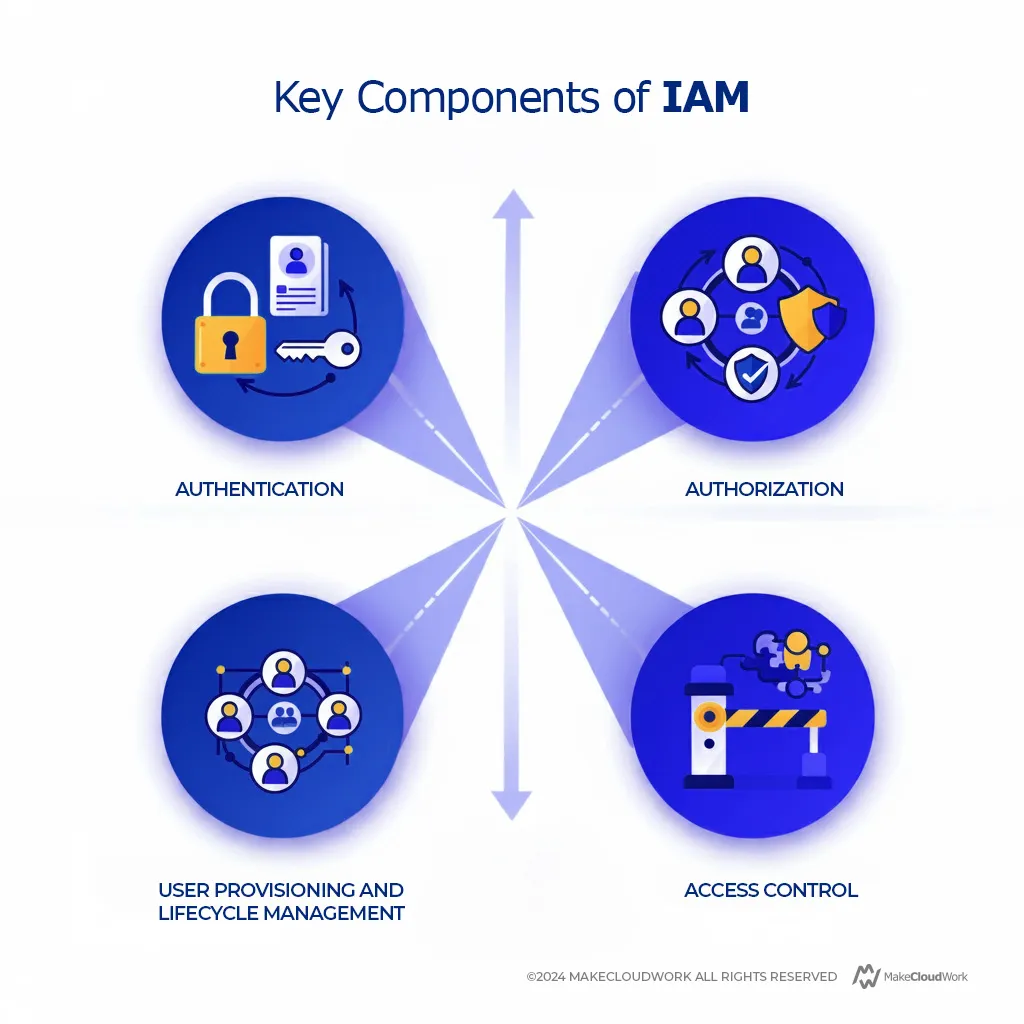
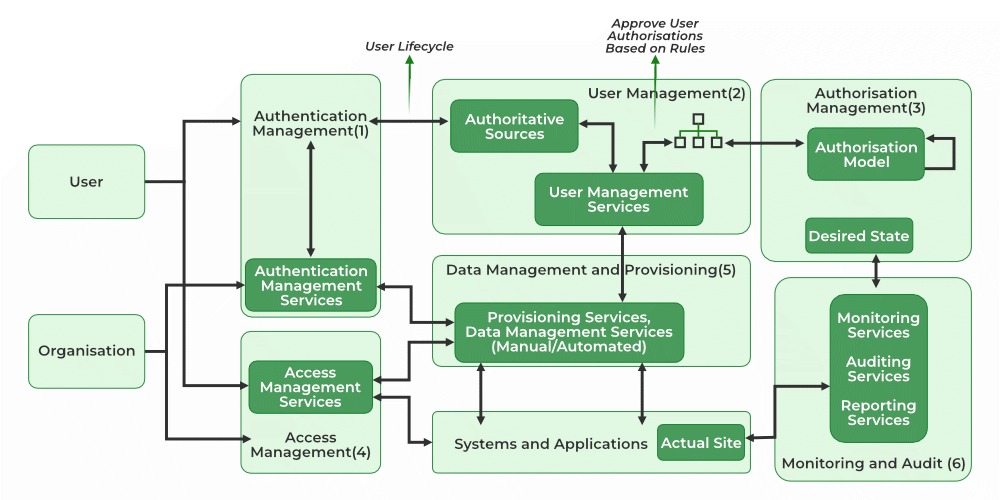
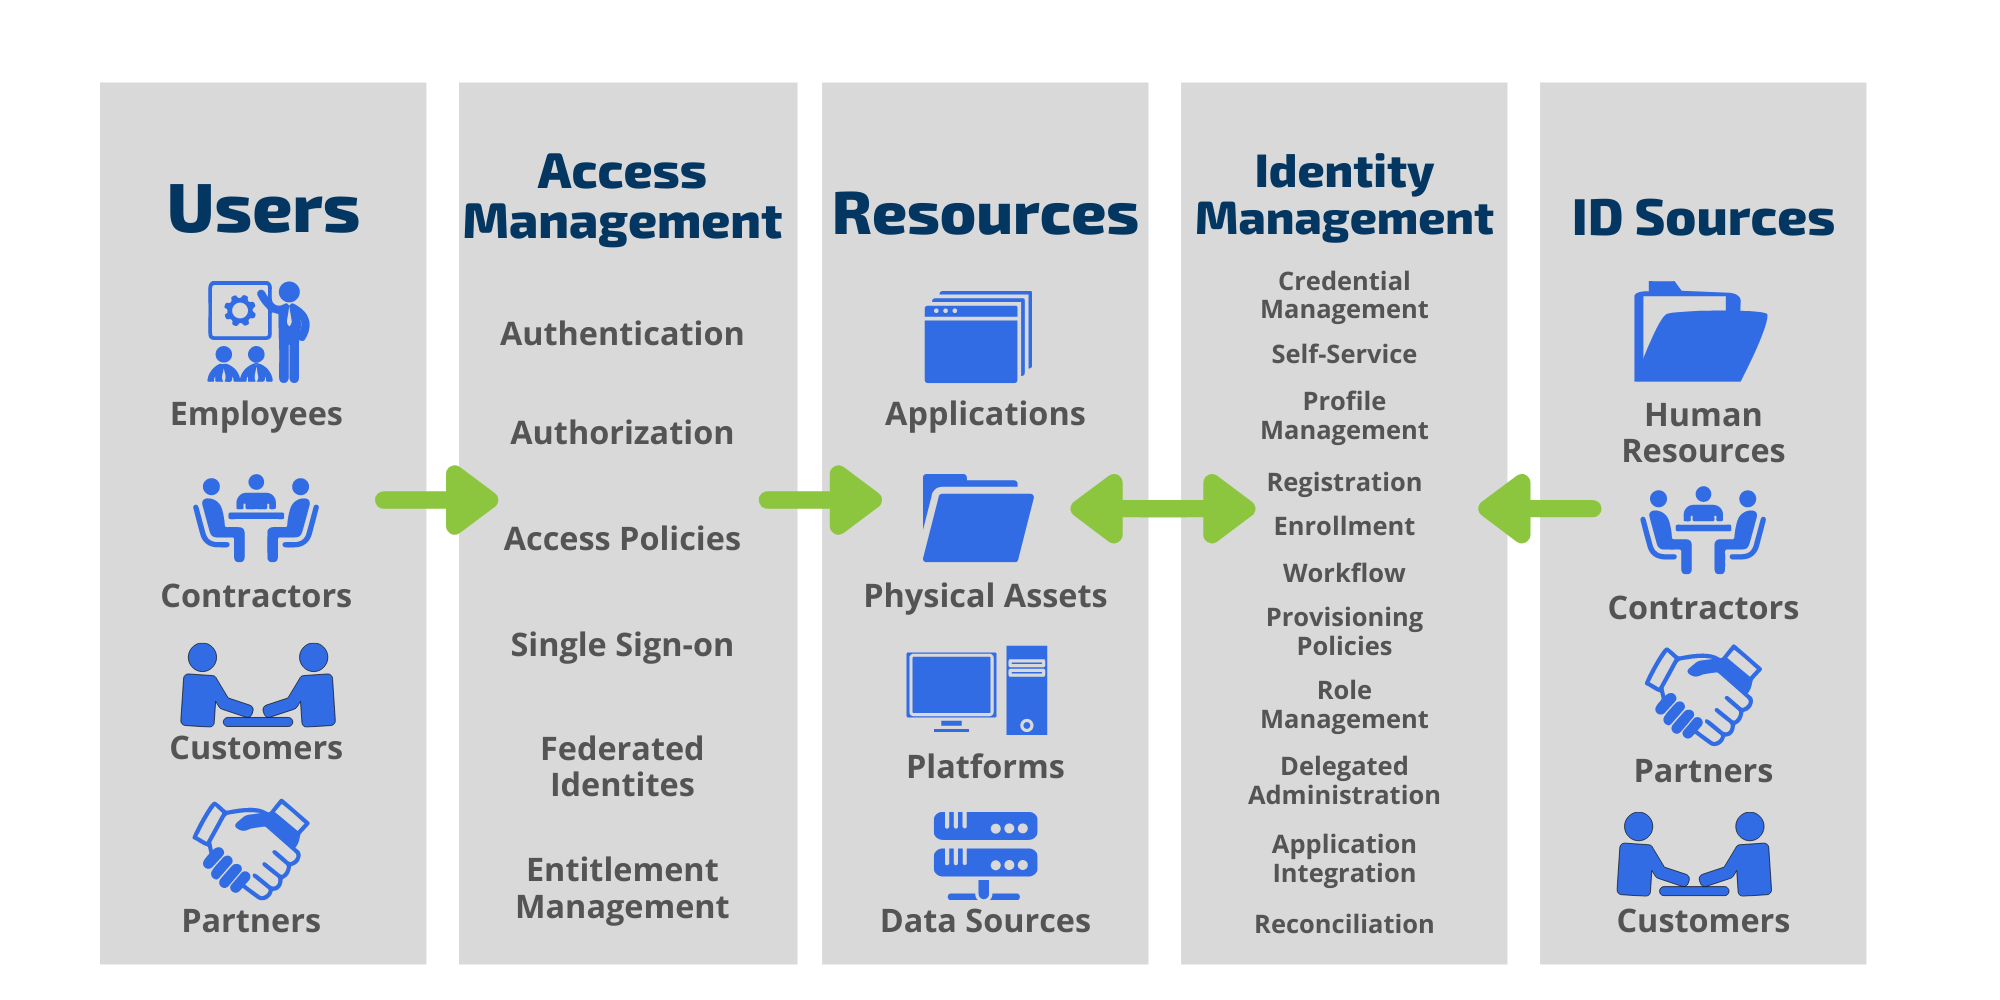
I spent three years building access management platforms for mid-size companies and another two cleaning up messes from poorly designed ones. What follows isn't a vendor whitepaper. It's what happens when you actually have to keep it running. An Identity Access Management System is a software layer that controls who gets access to what inside your organization. That's the textbook version. In practice, it sits between your identity sources like Active Directory or a human resources system, and the applications employees need to do their jobs. It decides whether Person A should see Database B on Tuesday morning. It handles provisioning new hires, changing permissions when someone transfers teams, and revoking access when someone leaves. The core components are identity stores, policy engines, authentication mechanisms, and audit logging. Each piece has to talk to the others reliably. If any single component fails, you either lock people out entirely or grant access to everyone by default. Neither outcome is acceptable for long.
I learned this the hard way during a migration from a legacy directory to Okta. We configured group-based provisioning through SCIM, set up SSO for fifteen applications, and declared success. Two weeks later, finance reported they couldn't access their expense system. The provisioning attribute mapping was silently dropping a middle initial that some of their employee IDs relied on as a unique key. The workaround was writing a custom attribute transformation script that normalized names before the SCIM sync ran. It took me about six hours. The fix itself was maybe forty lines of JavaScript, but debugging which attribute was causing the mismatch consumed most of that time.
How It Actually Works Under the Hood
Authentication and authorization are separate problems that people frequently conflate. Authentication answers "who are you?" Authorization answers "what are you allowed to do?" Your IAM system has to handle both, usually through protocols like SAML 2.0 for identity federation and OAuth 2.0 with OpenID Connect for modern application access. Here's how a typical login flow works end to end. An employee opens Salesforce. The app redirects to your identity provider with a SAML authn request. The IdP checks whether the user is already authenticated via session cookie or MFA token. If not, it presents a login page. After successful authentication, the IdP constructs a SAML assertion containing attributes like email, department, and role group membership. The application validates the signature, extracts the attributes, and grants or denies access based on its own authorization logic. All of this usually completes in under two seconds if your infrastructure is properly sized. The less visible part is just as important. Every assertion, every token refresh, every failed login attempt should be logged. Without detailed access logs, you're flying blind when something goes wrong. I've seen teams spend days tracing permission gaps because audit trails had been disabled to save on storage costs. It's not worth it.
Get the Full Details
Designing for Real Organizations
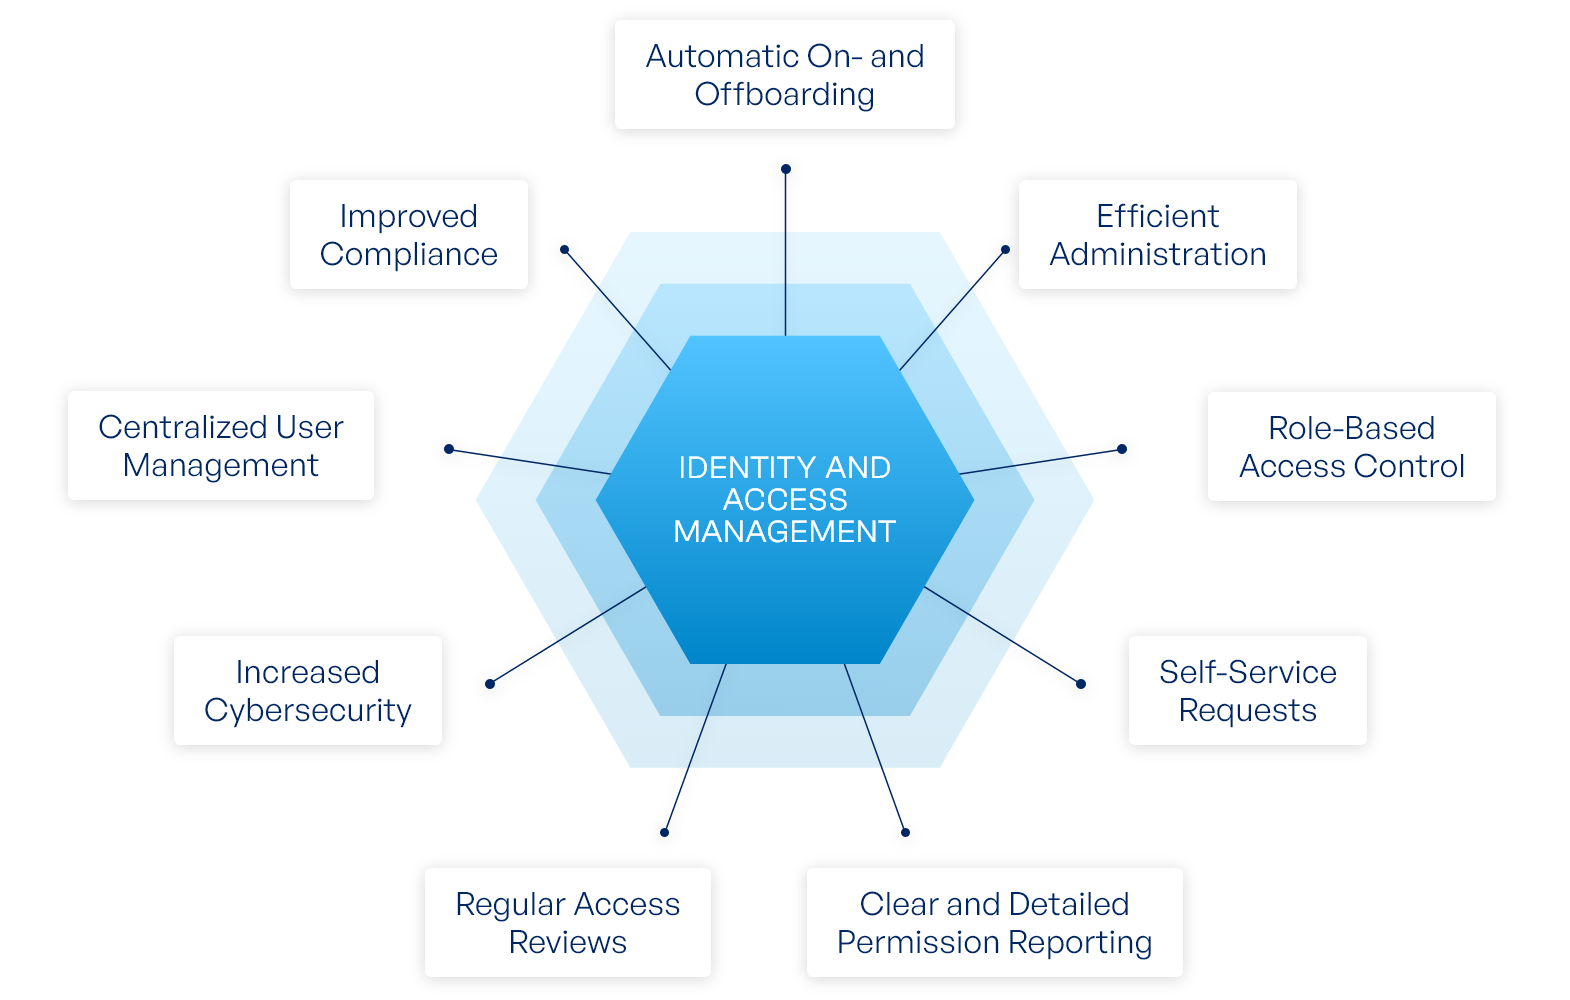
The biggest mistake I see is treating role-based access control as if it scales linearly. It doesn't. When you assign permissions by role, you're creating a mapping between job functions and access levels. That works fine with five or six roles. By the time you're managing thirty roles across twenty business units, the matrix becomes unmanageable. People get assigned conflicting roles. Permission creep happens because it's easier to add a role than to audit existing access. A better approach for complex environments is implementing attribute-based access control alongside RBAC. ABAC evaluates contextual factors like department, location, time of day, and device compliance in addition to role membership. This sounds more complicated upfront, but it actually reduces the total number of permission rules you need to maintain. You write one rule saying "engineering members can access code repositories from any corporate network" instead of creating individual rules for every engineering subteam across every office location. Another thing nobody warns you about is the joiner-mover-leaver lifecycle. Joiners are straightforward. You create accounts based on HR data. Movers are where things fall apart. When someone changes departments, their old access doesn't automatically disappear. Most IAM systems handle provisioning well and deprovisioning okay. Reconciliation between what the system thinks the user has and what they actually have is where the gaps appear. I recommend running a quarterly access certification campaign where managers review their team members' access. Even sixty days of stale permissions creates liability.
Common Pitfalls That Waste Time
First, over-relying on manual provisioning workflows. Every ticket a helpdesk agent fills out to create an account is a failure of automation. If your system can't pull new hire data from your HR platform and provision accounts without human intervention, you have a design problem. I've seen companies run IAM processes where seventy percent of account creation is still manual. It shouldn't be anywhere near that high. Second, treating MFA as a checkbox instead of a layered defense. Password plus an SMS code is better than password alone. It's also bypassed by SIM-swapping attacks that happen with frustrating regularity. Hardware security keys or biometric authenticators on managed devices are meaningfully more secure. The difference matters more than vendors admit when they tout MFA support as a complete solution. Third, ignoring API-level access. Everyone focuses on human users logging into dashboards. Service accounts, automated scripts, and third-party integrations often have broader permissions than the humans using those same systems. A compromised service account with admin privileges can do more damage than a compromised human account with standard access. These accounts tend to accumulate permissions over years without anyone reviewing them. I've audited environments where service accounts had domain admin rights that were granted during an initial setup five years earlier and never removed.
What This Approach Can't Do
No IAM system can enforce policies that aren't explicitly defined. If you don't write a rule saying contractor accounts expire after ninety days, they won't expire. The system only enforces what you configure. This means you need dedicated personnel, ideally one person whose primary responsibility is IAM governance, not a junior sysadmin who also handles printer issues. Another limitation is the integration surface area. Each application you connect to your IAM system becomes a potential failure point. Custom-built internal tools that don't support standard protocols like SAML or OIDC require custom connectors or proxy middleware. Building and maintaining those connectors is a recurring cost that often gets underestimated during initial deployment. A typical enterprise might integrate with forty to eighty applications over five years. Factor in the maintenance burden for each one. If your organization has highly regulated requirements around data sovereignty or air-gapped infrastructure, cloud-based IAM solutions may not be viable. In those cases, on-premises deployments like Keycloak or Microsoft Entra ID in hybrid mode are the alternatives, though they come with their own operational overhead.
Where to Start
If you're evaluating or implementing an Identity Access Management System from scratch, begin by inventorying your current access landscape. Map which applications exist, which directories hold the user data, and how access currently gets granted. You'll probably find gaps you didn't know existed. Then define your core roles and attribute model before touching any configuration. Rushing into tool selection without this foundation is how people end up with expensive systems they can't operate effectively. Popular platforms worth looking at include Okta, Microsoft Entra ID, Ping Identity, and Keycloak for those who want an open-source option with full self-hosting control. Each has different strengths depending on your existing Microsoft or non-Microsoft footprint, your budget, and whether you need cloud-native or hybrid deployment. The work doesn't stop at deployment. IAM is ongoing. Review access quarterly. Test your incident response procedures for credential compromise scenarios. Keep documentation current. The systems that run smoothly are the ones where someone pays attention to them regularly.