What You Actually Need When Setting Something Up
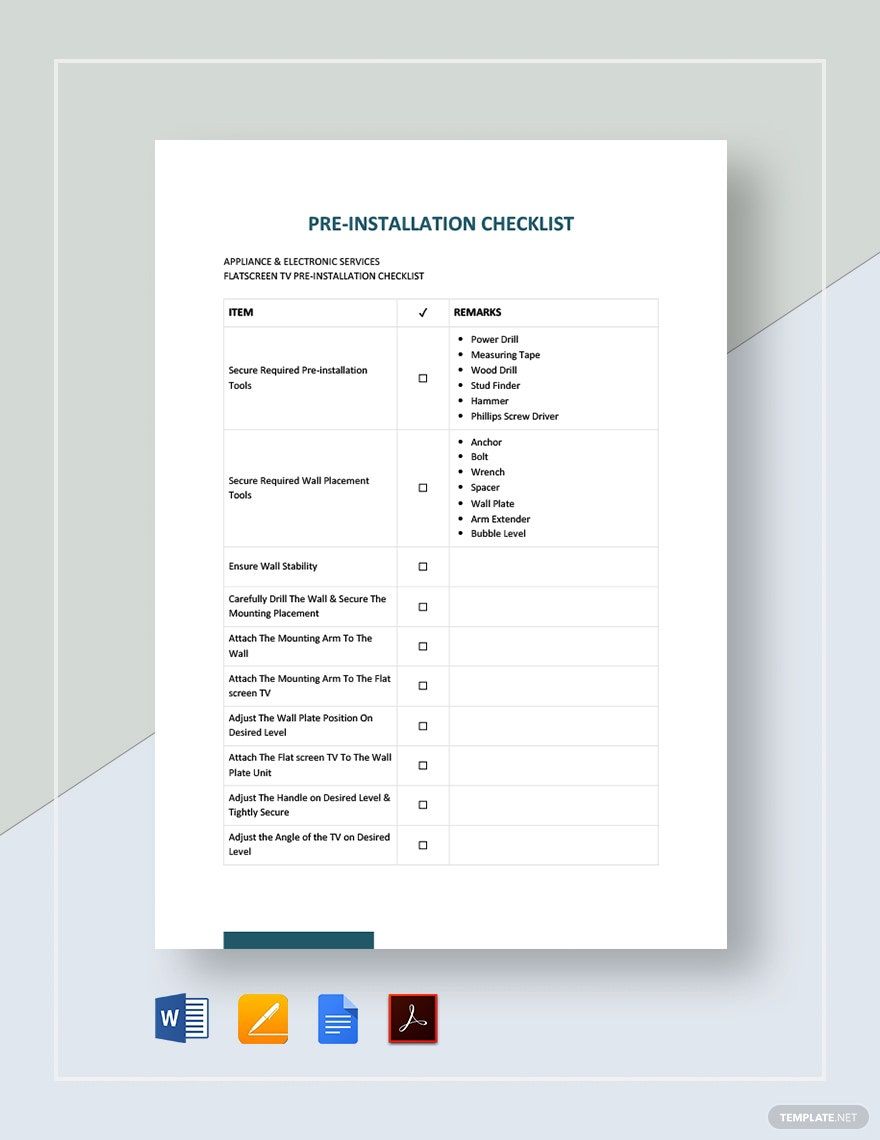
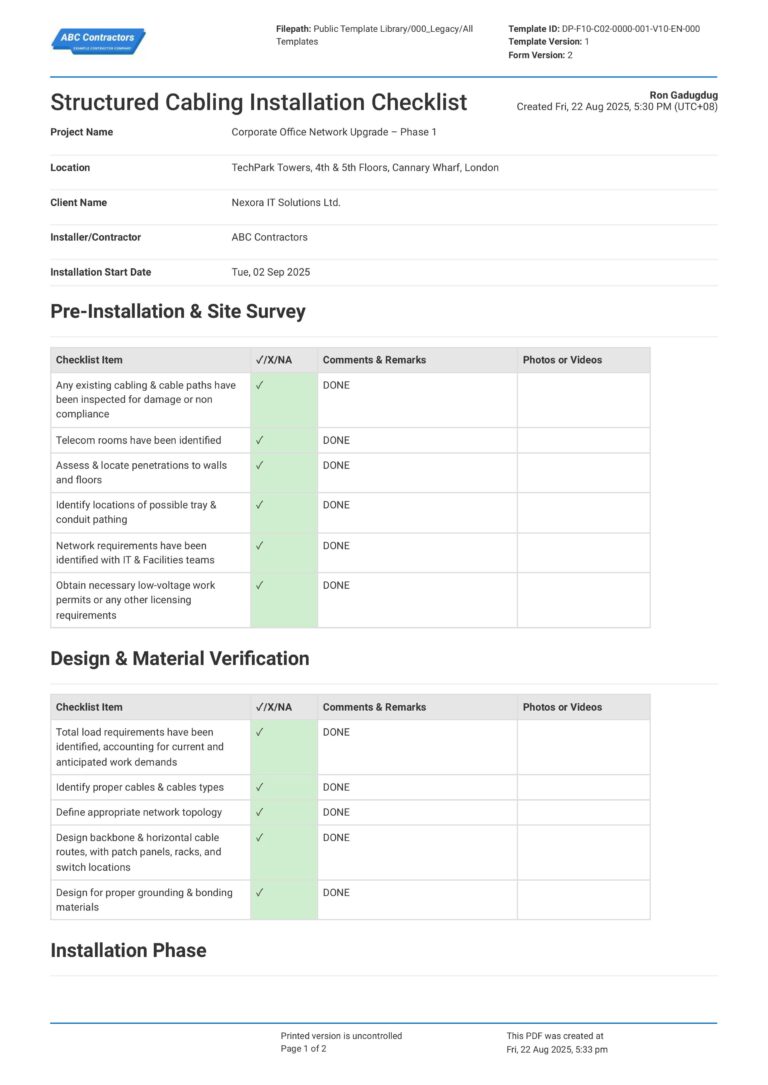
An Installation Guide Checklist is just a structured list of steps and verification points you follow before, during, and after installing a piece of software or hardware. It sounds simple, but the reason people use them is because things routinely fail in specific ways when you skip the less obvious steps. I've seen the same issue pop up on dozens of installations: someone deploys a service, it runs, they call it done, and then two days later the backup job fails because they never created the log directory the application expects to write to. Here is how I approach building and using one. The first thing to understand is that it is not the same as the installation guide itself. The guide tells you what to do. The checklist is your personal record of what you verified. I keep mine in a shared markdown file on our internal wiki. Each deployment gets its own section with timestamps. This is what actually saved us last year when a client claimed our software was causing disk leaks. We pulled the checklist from the install three months prior, saw that we had skipped the pre-flight disk space audit on the /var partition because it showed 90 percent free at the time, and tracked down the issue in twenty minutes instead of spending three days investigating. The structure I use has four sections. Pre-install, Dependencies, Installation, and Post-install Verification. Within each section I include both required steps and optional conditional steps based on the environment. For example, if the target machine runs Windows Server, I add a step for Group Policy conflict checks. If it is Linux, I add a step for SELinux or AppArmor profile verification. I do not write separate checklists for every OS variant. I use a single master list with annotated conditionals. This keeps maintenance down to one place when we update the software.
I have found that most people underweight the post-install verification section. They verify that the binary exists and the service starts. That is not enough. You need to verify the data path, the network binding, the log rotation, and the failure state. I once spent an afternoon debugging a connection timeout that turned out to be a firewall rule applied after installation. The checklist step I added afterward was explicit: confirm network connectivity using the same credentials and endpoints the application will use in production, not just a ping test. This detail is the kind of thing that does not show up in the vendor documentation because the vendor assumes the network is already correct. Another thing I do that beginners usually skip is a rollback confirmation step before the install begins. I run through the undo procedure to make sure it works, not just that it looks like it would work. Half the checklists I see online include rollback steps that reference files or services that do not exist in newer versions of the product. You write a rollback plan, then you verify it can actually execute. I lost a day once because I assumed the rollback script from the previous major version still worked. It did not. The database migration scripts had changed the table structure and the rollback failed mid-way, leaving the system in a half-applied state. Here is the honest part about checklists. They do not prevent human error. They prevent you from forgetting steps you already know you should check. The real value shows up when you go through a checklist that is six months old and you realize you skipped three items because you were rushing. That moment is the whole point. You catch yourself before the customer does.
There are cases where a checklist adds very little value. If you are installing the same package on identical machines in an automated pipeline with full observability, a lightweight status check is usually sufficient. But the moment you introduce variability, like custom paths, non-default ports, or external authentication, the checklist pays for itself immediately. I also recommend pairing the checklist with a short deployment log that captures exit codes and errors rather than relying on memory. I use a simple script that appends each command and its output to the checklist file during execution. This gives you a timestamped trail without extra effort. The download I linked below is the template I actually use. It is plain text with section markers and example entries so you can see how detailed the verification steps should be. I do not put passwords or secrets in it. I keep those in a separate vault file. The template covers pre-flight checks, dependency verification, installation commands with expected outputs, and post-install validation with specific pass/fail criteria for each step.
Get the Full Details