Working with the IPPF when you're actually trying to get a job done
The International Professional Practice Framework is technically defined as the collection of mandatory guidance for internal auditors, but that definition sounds like it was written by someone who's never had to explain to a CFO why their audit plan needs to align with IESAs. Let's skip the textbook intro and talk about what actually happens when you try to apply this framework in a real organization. The IPPF sits under the IIA's umbrella and contains Attribute Standards (1000 series), Performance Standards (2000 series), and Implementation Standards (specific to types of work). That structural map is what the books will show you. The reality is that most people only touch 1100, 1200, 2010, and 2020 on any given engagement because those are the ones that generate findings when they're violated. Here's a specific problem I ran into about eighteen months ago. My organization adopted a new ERP system, and I had to determine whether our existing audit universe aligned with the new IPTEA (Information and Related Technology) standards under the IPPF. The framework doesn't explicitly address cloud migration scenarios, and the IPTEA guidance was written before SaaS became the default infrastructure for enterprise companies. I spent three weeks trying to force a square peg into a round hole before realizing I needed to use the Principle-Based Standards approach — meaning I cited 2120 (Sufficiency and Competency of Information) and 2201 (Planning Considerations) rather than chasing specific technology guidance that didn't exist for the scenario. The workaround worked because the IPPF is structured to allow principle-based application when Implementation Standards fall short of emerging practice. It's not ideal documentation for a skeptic, but it's what happened when I had to tell the audit committee we were compliant despite the framework being silent on the exact situation.
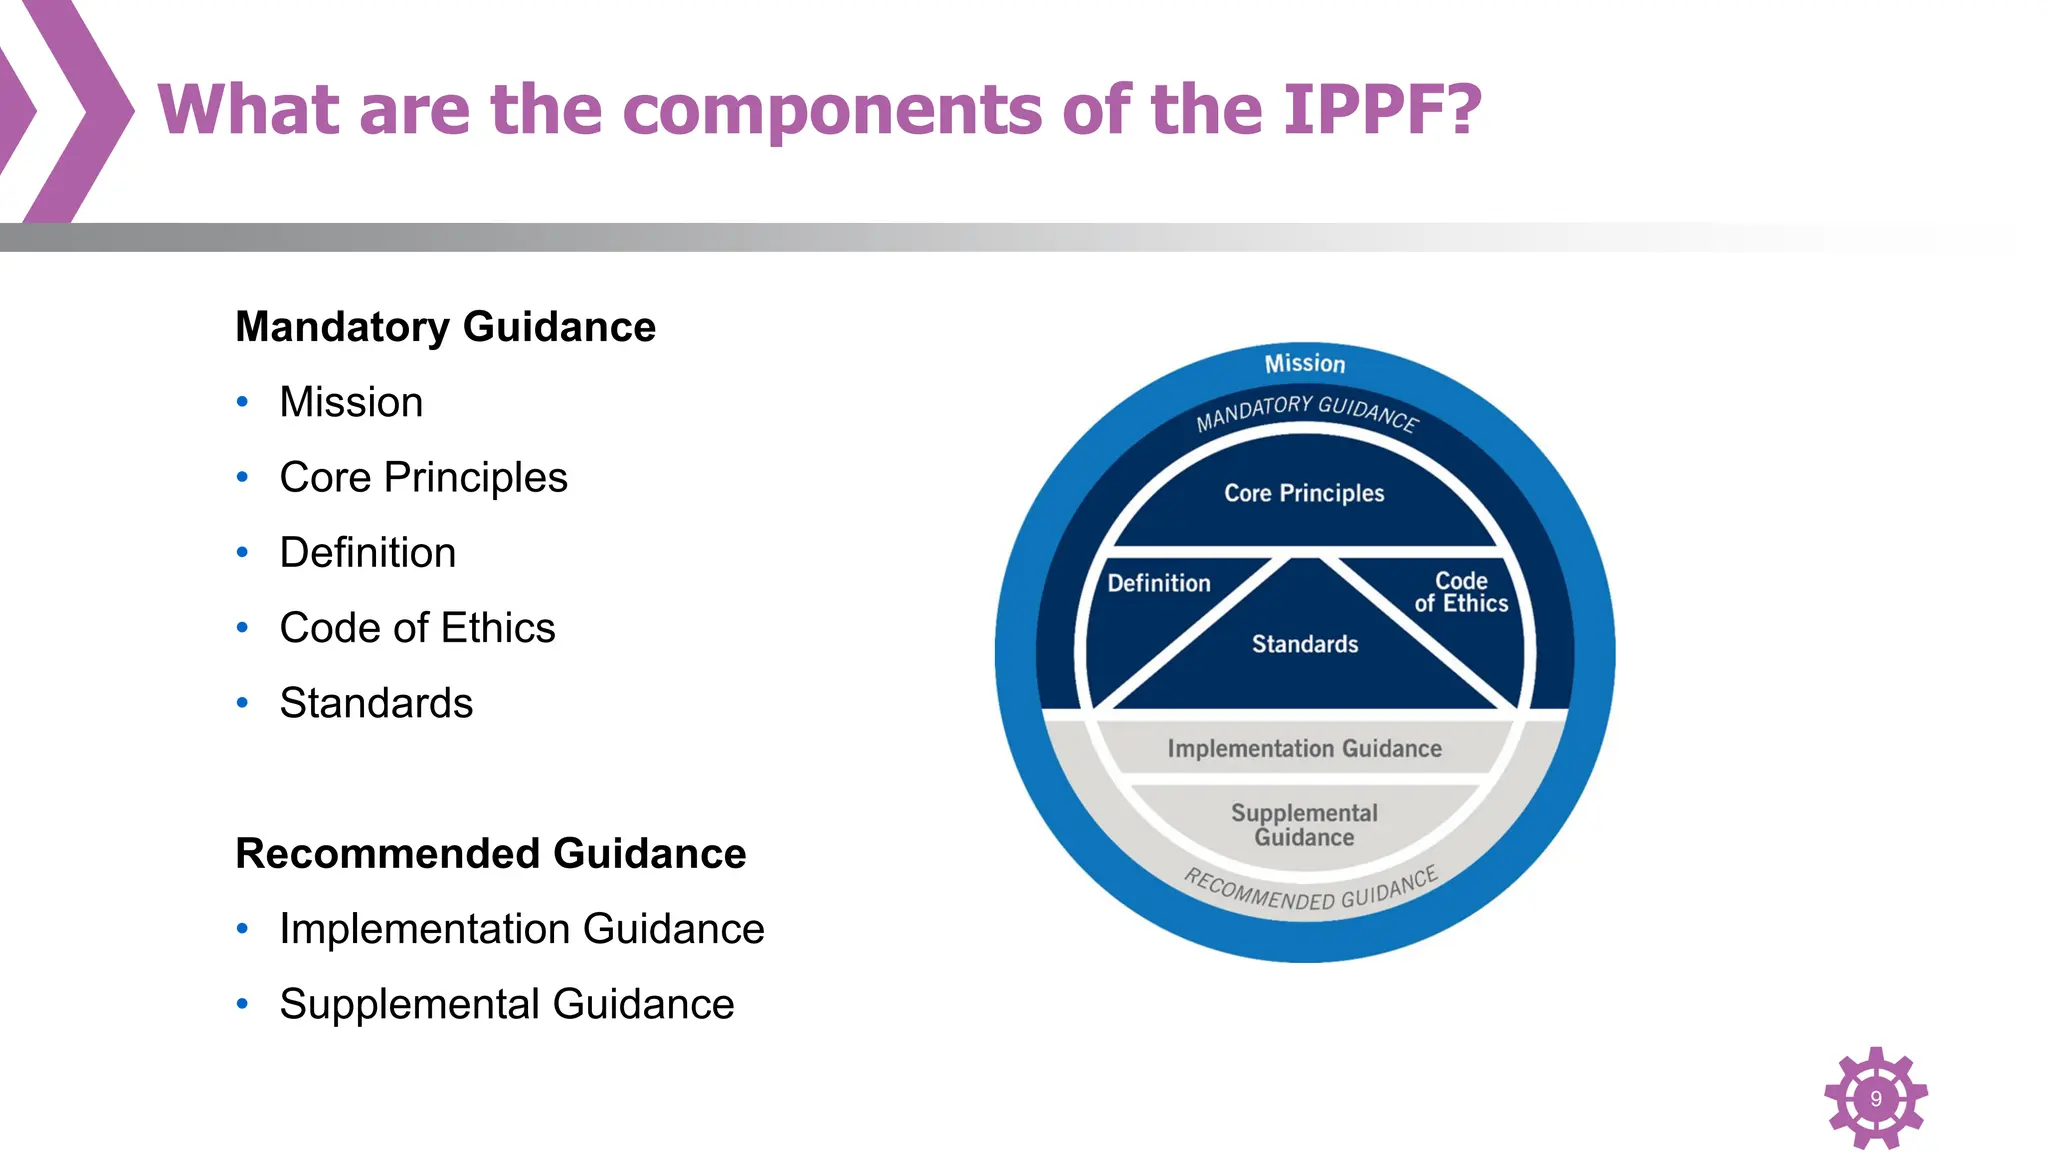
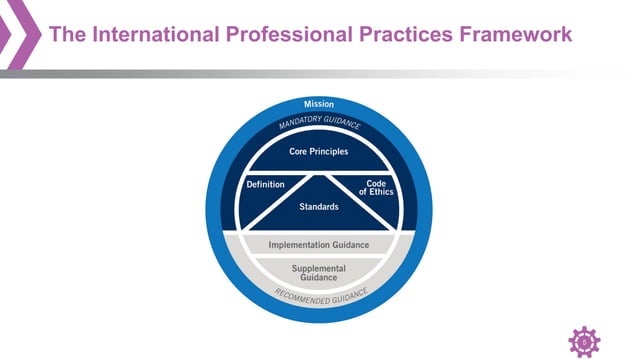
The counterintuitive thing about the IPPF that nobody tells beginners is that compliance with the framework doesn't actually improve audit quality. What improves audit quality is using the IPPF as a constraint system. You spend more time proving you followed the Standards than you spend analyzing risks. I've seen senior audit managers treat the IPPF as a checklist of evidence to collect rather than a structure for professional judgment, and the audits from those people read like compliance reports rather than assurance work. The Standards were designed to protect against negligence, not to guarantee competence. Another nuance people miss: the IPPF's mandatory guidance is layered, and the hierarchy matters more than most practitioners realize. The Core Principles come first and override everything else. When a Performance Standard conflicts with a Core Principle, the Core Principle wins. This isn't theoretical — I've watched audit reports get rejected by quality assurance reviewers specifically because they met the letter of Standard 2410 but violated the spirit of Core Principle 5 (Demonstrates Integrity). The framework anticipates this conflict and builds in the override mechanism, but it's buried in the front matter where nobody reads it.
How to actually use the IPPF without losing your mind
Start with your engagement objectives, not with the Standards. Too many auditors open the IPPF first and work backward to justify what they've already decided to do. That creates a confirmation bias problem where you're looking for Standards that support your preconceived conclusions rather than letting the work plan be shaped by the risk assessment. Open to the attribute Standards, understand what independence and objectivity require for your specific engagement, then build outward. The 2010 and 2020 Planning Standards are where most people get trippedosed up. 2010 requires an engagement objectives statement, and 2020 requires an engagement work program. The work program detail varies enormously depending on whether you're doing operational, compliance, or IT work. For financial process audits, a typical work program might run thirty to fifty pages. For a focused compliance review, you might see ten to fifteen pages. The variation isn't about effort — it's about the depth of testing required by the risk profile you've documented under 2010. When you're documenting conformance with the IPPF, focus on the 2400 series. That's where most external quality assessments look first. Standard 2420 requires communication of incomplete, incorrect, or insufficient information. This is the standard that gets people in trouble when they send preliminary findings to management without confirming the data with source documentation. I've had to restart entire engagements because a team member communicated a finding based on an unverified system output, and the 2420 violation forced a retraction that cost three days of work. The workaround is simple: no communication of findings occurs until the working papers have been reviewed and the underlying evidence has been cross-referenced. It adds approximately two hours per engagement for review cycles, but it prevents the much larger time sink of corrective action after the fact.
Get the Full Details
Where the IPPF breaks down
The framework assumes a mature internal audit function with sufficient resources, access to information, and organizational independence. In smaller organizations where the internal audit function is a single person or where the chief audit executive reports through a chain of command that includes the people being audited, the IPPF's requirements around independence and objectivity become difficult to satisfy without creating real organizational tension. The framework acknowledges this in 1100 but doesn't provide a practical path forward for situations where structural independence is impossible. For organizations in heavily regulated industries where local regulation conflicts with the IPPF — particularly around confidentiality requirements that restrict information sharing or access — the framework provides no resolution mechanism. You comply with the regulation and document the deviation from the IPPF with justification, but that creates a quality assurance gap that external assessors will flag during reviews. If your organization is small enough that the full IPPF compliance burden outweighs the assurance benefit, consider whether alternative frameworks like the COBIT framework for IT governance or a risk-based internal audit approach aligned with COSO might serve you better. The IPPF is the gold standard for professional internal audit practice, but it's also expensive to implement properly and delivers diminishing returns when applied mechanically in organizations that lack the maturity to support it.
Where to get the current IPPF documents
The complete International Professional Practice Framework Ippf is available directly from the Institute of Internal Auditors at theiiainstitute.org. You'll need membership or a subscription to access the full Standards and Guidance documents, but the Core Principles and an overview of the framework structure are publicly available. The documents are typically updated annually, so verify the version number against the date of your last quality assurance review before relying on them for conformance documentation.