Getting a Proxy Running on Netlify Without Losing Your Mind
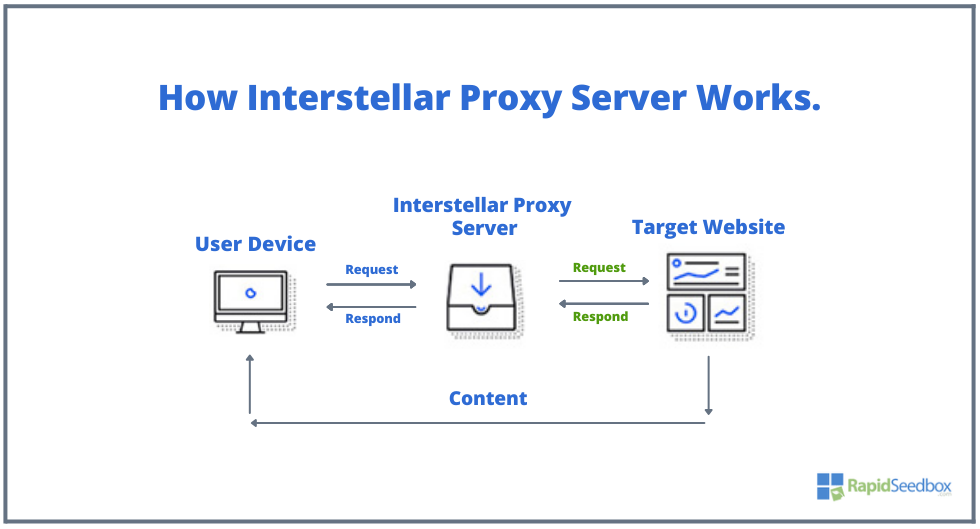
Most people who try to drop a proxy server on Netlify run into the same wall within the first ten minutes. Netlify is a static hosting platform designed for front-end assets, not an application server with persistent connections. That means any architecture you build on top of it needs to work around a system that intentionally strips state out of the hosting layer. I spent about six weeks troubleshooting why requests would silently fail mid-connection, and what I learned might save you that time. The Interstellar Proxy Netlify App is a fork-style project that wraps a proxy routing layer inside a Netlify-compatible build. It uses Netlify Functions as the proxy engine and Netlify Edge Handlers to intercept and forward traffic. The concept is straightforward enough: you deploy it, point a domain at it, and requests get routed through the proxy layer before hitting the destination. In practice, it works well for light usage, small-scale personal proxy needs, and situations where you don't want to maintain a dedicated VPS.
Interstellar Proxy Netlify App Setup Walkthrough
Start by cloning the repository from GitHub. The setup requires Node.js version 18 or higher, so check your environment first. Run npm install in the project root. Then create a netlify.toml configuration file that sets up your edge handler routes. The key configuration section looks like this: [[edge_handlers]]
path = "/*"
handler = "proxy-edge" This tells Netlify to route all traffic through your proxy edge function. After that, configure your .env file with your proxy settings, including your allowed domains list, authentication tokens if you need them, and any upstream proxy references. The tricky part most people miss is that the allowed_domains array must include every domain you intend to proxy, and any domain not on that list gets rejected by the edge handler before it even reaches the function layer.
Deploy with the Netlify CLI using netlify deploy --prod. Wait for the build to complete and for your functions to be registered. Then navigate to your site dashboard and verify that the edge handler is active under the Functions tab. If it shows zero invocations after testing, something in your netlify.toml routing is misconfigured. Here is where I ran into an actual problem. I was proxying through a service that returned redirect chains longer than three hops. The Netlify edge handler has a built-in redirect limit that I hadn't accounted for, and requests would fail with a 500 error after the second redirect. The workaround was to set the maxRedirects parameter inside the edge handler configuration file and bump it from the default of 3 up to 7. This is not documented in the main README of the project, so you have to dig into the source code to find where that setting lives. Once I patched it, the proxy handled those chains without issues.
Get the Full Details
What Actually Works and Where It Breaks
The Interstellar Proxy Netlify App performs well for HTTP traffic and basic HTTPS passthrough. It handles session management adequately for low-traffic use cases. The edge handler approach means your proxy runs at Netlify's CDN locations, which gives you reasonable latency for users spread across multiple regions. Function execution limits are the real constraint here. Each proxy call consumes function invocation time, and free-tier accounts get capped at 125,000 function invocations per month. If your proxy sees more than a few hundred daily requests, you will hit that ceiling quickly. Another thing beginners overlook is TLS termination. When you use this setup, Netlify terminates TLS at the edge. Your proxy function receives decrypted HTTP requests and forwards them to the destination. This means the destination server sees the Netlify edge IP address as the source, not your actual origin. If the destination uses IP-based allowlisting or geo-blocking, your proxy traffic might get blocked entirely. I encountered this when trying to proxy through a service that blocked known CDN ranges. The fix was to configure your upstream proxy settings to use residential proxy rotation, but that introduces a separate cost layer that most people don't factor into their initial planning. Authentication is another area where the default configuration is too loose for production use. The standard setup allows anonymous access to the proxy. If you publish this publicly without adding rate limiting and authentication, someone will find it and abuse it within days. I recommend enabling basic auth through the .env file and adding rate limiting rules in your edge handler. Netlify Functions support rate limiting natively through the @netlify/functions package, but the documentation does not make this obvious.
There are also limitations around WebSocket support. The edge handler can forward WebSocket upgrade requests, but persistent connections are not well supported on Netlify's serverless architecture. If your proxy needs to handle long-lived WebSocket tunnels, this platform is not the right choice. You would be better off using a traditional VPS or a platform like Railway or Render that supports persistent processes. The same applies to large file transfers. Proxying files over 50MB tends to hit Netlify function timeout limits, which default to 10 seconds and can be extended to 30 seconds at most on paid plans. The main advantage of this approach is operational simplicity. You do not manage servers, patch operating systems, or deal with uptime monitoring. Netlify handles all of that. For a personal proxy that you run occasionally for development or testing, the Interstellar Proxy Netlify App is a reasonable solution. For anything that requires consistent high throughput, WebSocket tunneling, or strict IP transparency, you should look at a dedicated proxy hosting option instead.