What You Actually Need to Know About It Essentials Chapter 11 Exam Answers
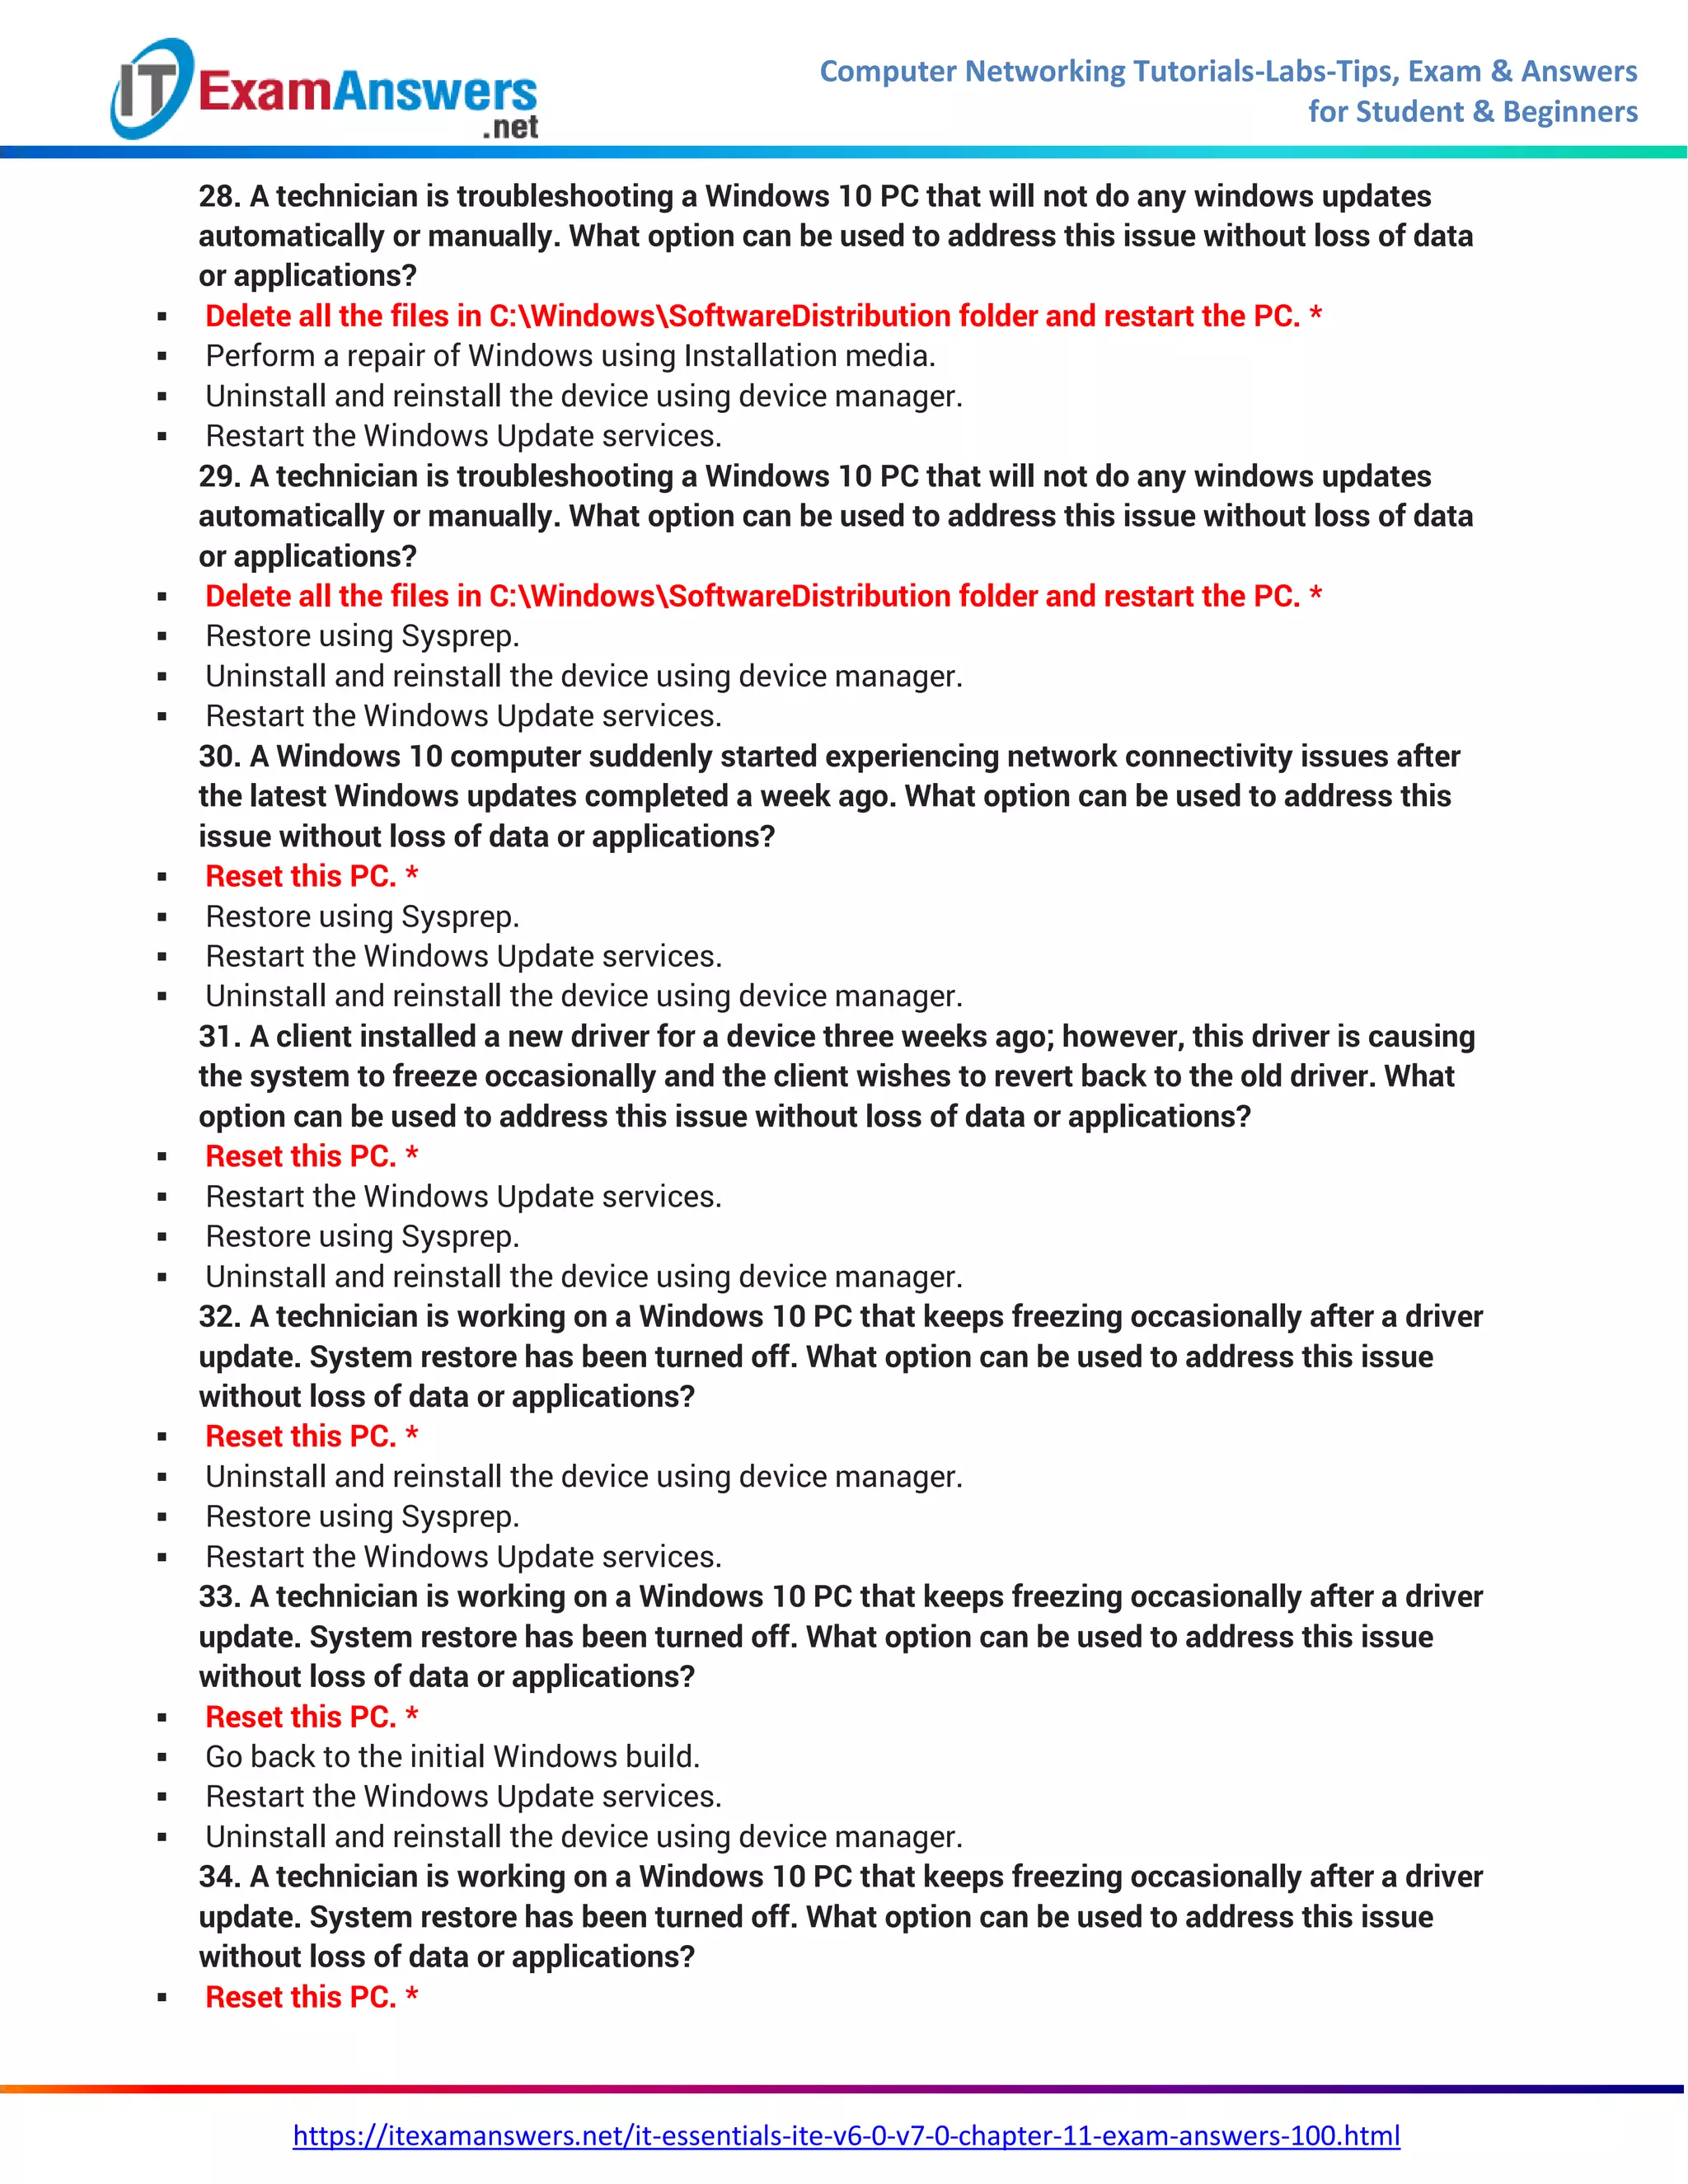
Chapter 11 in CompTIA IT Essentials covers security fundamentals. That means you are looking at topics like malware types, cryptography basics, authentication methods, and security policies. When people search for It Essentials Chapter 11 Exam Answers, they usually want to prepare for a test that checks whether they understand basic security concepts well enough to apply them in a real workplace. I have seen students struggle with this chapter more than any other. The security section tends to pile on acronyms without much context. You get hit with AES, RSA, SHA-256, and TLS all in one quiz. The exam wants you to know which one does what, but the course material often explains them in isolation rather than showing how they work together.
Where to Find Reliable It Essentials Chapter 11 Exam Answers
Official practice exams come from CompTIA directly, or you can use materials from the publisher if your school provided a textbook. Avoid sites that claim to have "dump" questions because those are usually outdated or incorrect. The real exam changes question wording regularly, so memorizing exact answers from random forums will not help you pass. The best approach is to work through practice questions and understand why each answer is right or wrong. If you pick the correct option but cannot explain the reasoning, you do not actually know the material. This matters because the exam includes scenario-based questions where two answers look correct at first glance. I ran into a specific problem last year when a student kept failing the security portion even after studying for weeks. The issue was that the practice tests he used were based on an older version of the curriculum. Chapter 11 had been updated to include more on zero trust architecture, but his materials still focused heavily on perimeter defense concepts. Switching to current practice questions from the official publisher fixed the gap entirely.
How the Chapter 11 Security Topics Actually Work
Malware classification is one of the trickier parts. People mix up ransomware with spyware because both involve unwanted software, but the behavior difference is huge. Ransomware encrypts files and demands payment. Spyware records keystrokes and sends data to a third party. The exam expects you to know which type matches which description. Cryptography questions focus on symmetric versus asymmetric encryption. Symmetric uses one key for both encryption and decryption. Asymmetric uses a public key and a private key pair. I have noticed that most students remember the definitions but forget when to use each type. Public key encryption is slower but solves the key distribution problem. Private key encryption is faster but requires a secure way to share the key beforehand. Authentication methods cover passwords, tokens, biometrics, and multi-factor authentication. The exam loves asking which scenario requires MFA. The answer is usually any situation involving sensitive data or remote access. A single password is no longer considered sufficient protection in most enterprise environments.
Get the Full Details
I encountered an edge case during a study group where someone insisted that hashing and encryption were the same thing. They are not. Hashing is a one-way function that produces a fixed-length digest. You cannot reverse it to get the original data. Encryption is reversible if you have the key. The exam will test this distinction, often by describing a password storage scenario where hashing is the correct method.
Common Mistakes That Cost Points
Students frequently confuse the port numbers for common protocols. HTTPS uses 443, not 80. SSH uses 22, not 23. FTP uses 21. Telnet uses 23. These numbers appear in multiple questions, so mixing them up guarantees lost points. Another pitfall is assuming that encryption alone provides confidentiality. It does, but encryption without authentication leaves you vulnerable to man-in-the-middle attacks. The exam sometimes presents a scenario where data is encrypted in transit but the certificate is not verified. That is still a security risk because an attacker could intercept the connection and present a fake certificate. I have also seen people overthink the difference between hashing algorithms. SHA-256 and SHA-512 are both secure choices. MD5 and SHA-1 are considered broken and should never be used. The exam may ask which algorithm is insecure, and the answer is always the older ones.
What This Method Cannot Do for You
Using practice questions without understanding the underlying concepts will only get you so far. The exam tests application, not rote memorization. You might guess the right answer three times in a row, but the next question will probably throw in a scenario you have not seen before. Some study guides claim to predict exact exam questions, but CompTIA explicitly prohibits this. Any site selling "leaked" questions is operating outside the testing policy and risks your certification if caught. The official route is through certified training partners or self-study using approved materials. If you are struggling with the security topics specifically, consider focusing on hands-on practice rather than just reading. Setting up a home lab where you configure firewalls, test encryption tools, and analyze malware samples in a safe environment builds practical knowledge that translates directly to the exam. This approach usually takes about two to three weeks of consistent practice and tends to improve retention significantly compared to passive studying.

Bottom Line for Chapter 11 Preparation
The security section is dense but manageable if you organize the material correctly. Group related topics together. Keep malware types separate from authentication methods. Understand how cryptography fits into both categories. Work through practice questions and track which areas you miss. Focus your review time on those weak spots rather than re-reading material you already know. When searching for It Essentials Chapter 11 Exam Answers, prioritize official or reputable sources over forums that promise quick passes. The exam is designed to validate real knowledge, and the only reliable way to pass is to actually learn the content. Spend about twenty to thirty minutes daily on practice questions, and you should feel comfortable with the material within a few weeks of focused study.