What a Management Policy Actually Looks Like When It Works
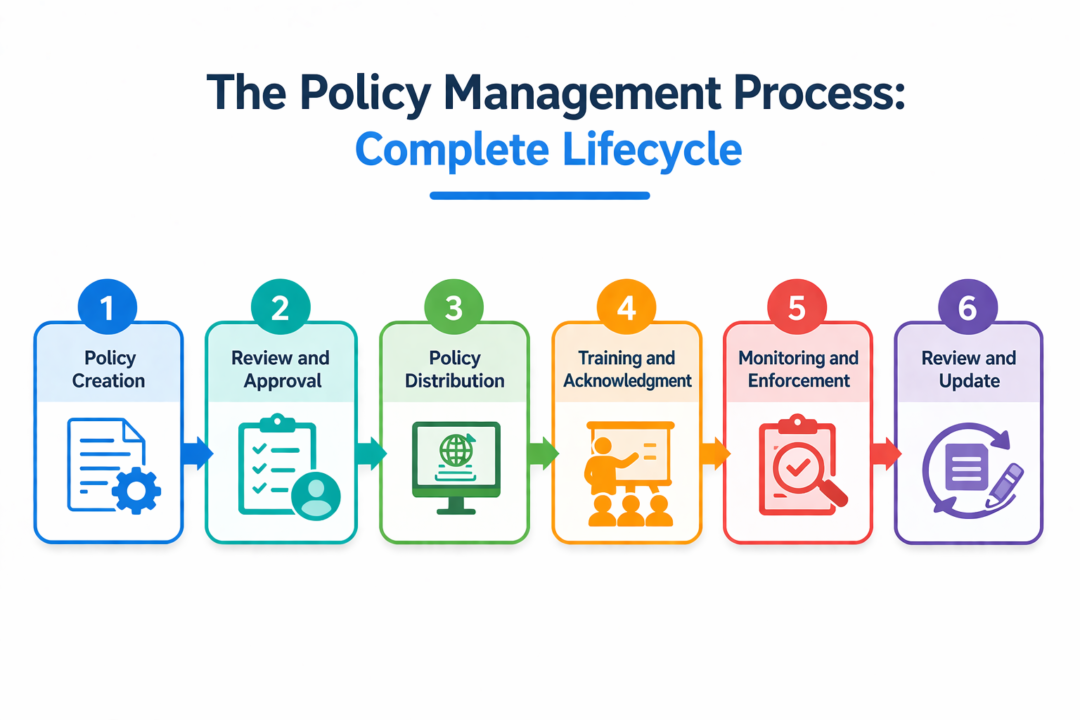
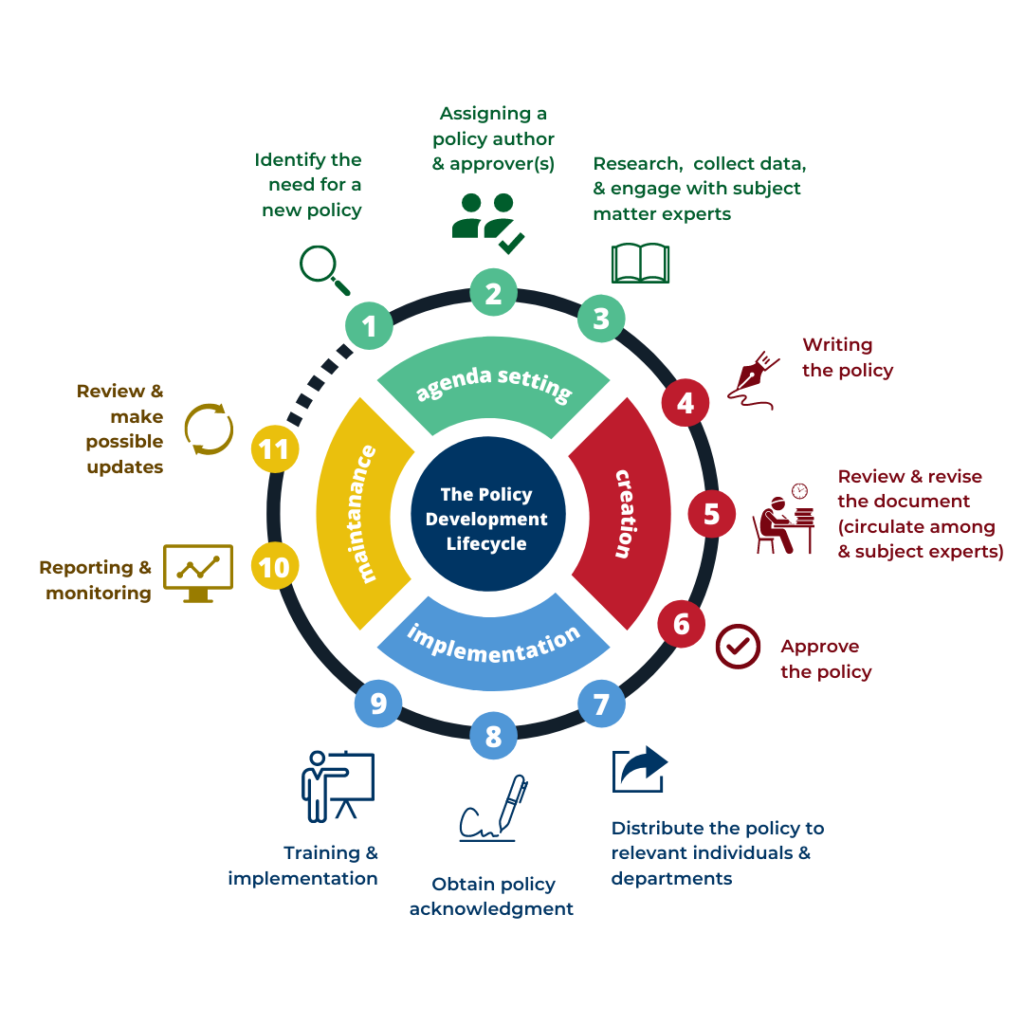
A Management Policy is the written framework that defines how an organization makes decisions about its operations, resources, and compliance requirements. It is not a set of ideals. It is a reference document that people are expected to consult when they encounter ambiguity in their daily work. I once spent a month mapping a company's legacy policy archive before they even had a coherent Management Policy in place. The documents were stored across at least twelve different shared drives, in formats ranging from Word to PDF to actual printed binders in a closet. The first issue was not writing new policy. The first issue was figuring out what existed and whether any of it was still current. I ended up creating a simple version-tracking spreadsheet that flagged which documents had been updated in the last 18 months and which had no recorded revision date. That spreadsheet alone became the foundation of the new Management Policy structure because it forced everyone to acknowledge what was actually in use versus what was assumed to be in use.
Core Components of a Functional Management Policy
The structure of a management policy should follow a consistent format so readers know where to find what they need. The standard sections you will see across most functional policies include: scope, purpose, definitions, roles and responsibilities, policy statements, procedures and controls, exceptions and escalation paths, and review schedule. The scope section should be specific enough that a reader can immediately tell whether the policy applies to their situation. Generic scope statements like "this applies to all employees" are common and useless. A more functional scope statement specifies the organizational units, geographic regions, system types, and data classifications covered. The policy statements themselves should be written as requirements, not suggestions. Words like "should," "may," and "recommended" create ambiguity that gets exploited when people need to make decisions under pressure. Use "shall" for mandatory requirements. Use "must" for things that have hard compliance implications. The difference matters more than most organizations account for.
Roles and responsibilities are where most management policy documents fail in practice. A common pattern I have seen repeatedly is listing job titles without defining the actual decision authority attached to each role. "The department head shall approve requests" tells you nothing about what qualifies as a request, what the approval threshold is, or what happens when the department head is unavailable. The fix is to define decision authority matrices that map specific scenarios to specific roles with clear fallback conditions.
Get the Full Details
How to Write a Management Policy That People Actually Follow
The biggest mistake organizations make is writing policies based on how work should be done rather than how work is actually done. I watched a team produce a comprehensive IT resource management policy that required dual approval for any cloud service provisioning above a certain cost threshold. The policy looked good on paper. It took approximately three weeks for the team to realize that the dual approval process was adding seven business days to every procurement cycle, and that nobody was actually following it because the workaround was faster than compliance. The policy was rewritten within a month to reflect the actual workflow. The approval threshold was adjusted based on real spend data, the dual approval was replaced with a single approval plus a quarterly audit review, and the policy now included an explicit exception process that took less than 24 hours to complete. The revised version cut the average provisioning time from 10 business days to 2 business days. Before you write anything, spend at least a week shadowing the people who would be subject to the policy. Ask them to walk through a recent decision they made that involved judgment calls. The gaps between what they describe and what your draft policy requires will show you exactly where the friction points are. This process alone will save you from publishing a document that gets filed away and forgotten within two weeks.
Advanced Considerations Most Guides Skip
There is a counter-intuitive relationship between policy complexity and compliance adherence. Organizations with the highest compliance rates typically maintain shorter, simpler policies with extensive linked procedures and standards. The management policy itself should be a high-level reference. The detailed step-by-step instructions belong in supporting documents that are easier to update independently. Another issue that goes unnoticed is the review cadence. Most organizations schedule annual policy reviews. Annual reviews are inadequate for any organization where technology, regulation, or operational scale changes meaningfully within a 12-month period. I recommend trigger-based reviews tied to specific events: a regulatory change, a security incident, a major system migration, or a reorganization. Between triggered reviews, a lightweight quarterly scan of affected policy sections prevents documents from drifting into irrelevance without requiring a full rewrite on a fixed schedule. The version control mechanism matters more than organizations tend to acknowledge. A Management Policy without a clear version history becomes a liability because auditors cannot determine which requirements were in effect at any given point in time. Maintain a revision log that records the date, the author, a summary of changes, and the document identifier. Do not rely on file modification timestamps. Those can be wrong.
Limitations and When This Approach Breaks Down
A Management Policy will not solve problems that are fundamentally organizational rather than procedural. If leadership consistently violates the policy themselves, no amount of documentation will change behavior. The policy can only codify what the organization has already decided to enforce. It cannot create enforcement where there is none. There is also a ceiling on how much detail a policy can contain before it becomes unmaintainable. I have seen management policies exceed 80 pages. They are never read. They are referenced during audits and then ignored. Anything beyond 20 pages of core policy text should almost certainly be split into separate supporting documents. The management policy should state what must be done. Supporting documents should explain how to do it. The approach also assumes that the organization has some baseline of accountability. In environments where roles are unclear, decision rights are disputed, and consequences for non-compliance are inconsistent, a Management Policy will either be ignored or weaponized as a tool for political maneuvering rather than operational guidance.

If you are starting from zero, do not attempt to write a comprehensive policy covering every possible scenario. Start with the top five decisions that cause the most friction or risk in your organization. Document those. Get them approved. Live with them for six months. Then expand. The alternative is producing a document that looks impressive and achieves very little.