Getting Paste Content Out of Pastebin Without Losing Your Mind
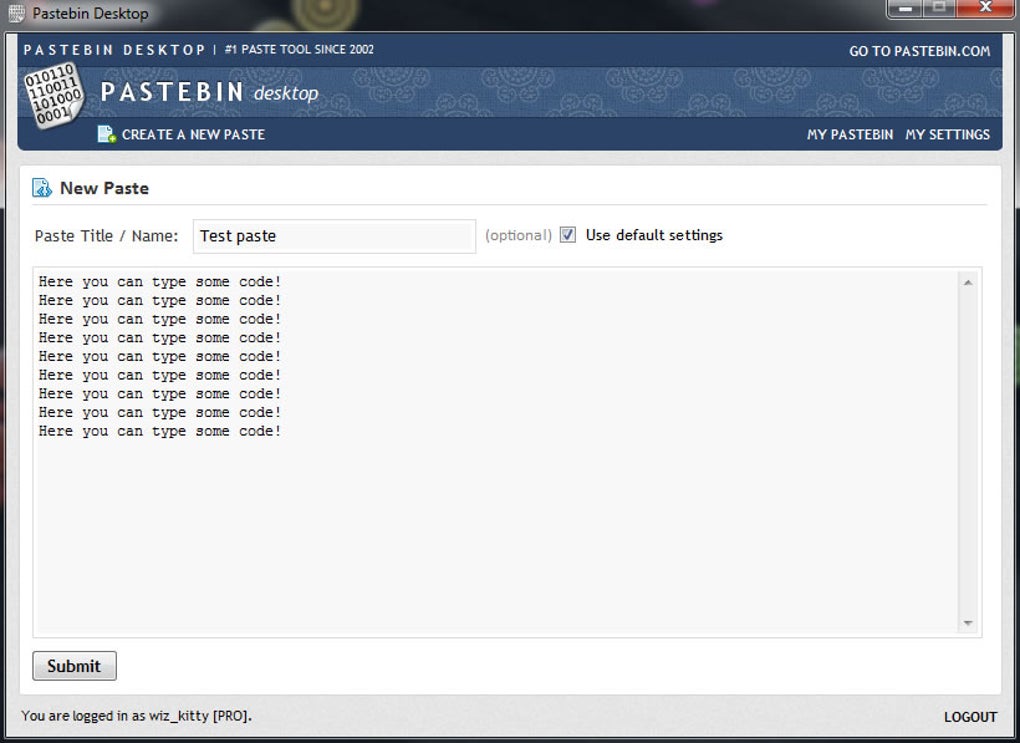
Pastebin is one of those sites that has survived because it does one thing and does it well. You paste text, you get a URL back. People have been using it since 2002 to share code snippets, logs, configuration files, and occasionally something they probably shouldn't have. The basic mechanics haven't changed much, which is both its strength and its weakness. The process itself is trivial. Go to pastebin.com, type or paste your content into the editor, choose a title if you want one, select a syntax highlighting language from the dropdown, pick an expiry setting if you care about it, and hit Create New Paste. The page gives you a URL like pastebin.com/AbCdEfGh and a few other link variations for embedding or raw access. That's it. The interface is ugly as hell but it works. I've spent years dealing with paste content in automated workflows, mostly for log collection and bug reproduction. One thing that trips people up constantly is the raw URL. The paste link displays the formatted version with syntax highlighting and a sidebar. The raw version — what your scraper or parser actually needs — is pastebin.com/raw/AbCdEfGh. I lost about two days once trying to debug why a script kept pulling the HTML wrapper instead of the actual content because I wasn't using the /raw/ endpoint. The site doesn't really advertise this anywhere obvious.
Using Pastebin in Production Pipelines
If you're pulling paste data programmatically, there are a few nuances worth knowing. The free API has rate limits — roughly one request per second per IP if you're not authenticated. That's not much if you're scraping multiple pastes or processing a queue. I ended up writing a simple token bucket throttler in Python that buffers requests and sleeps when it hits the limit. It added maybe ten minutes of development time but saved me from getting IPs blocked entirely. Another thing nobody tells you: paste expiry is not always reliable. The default expiry is never, which means your paste lives indefinitely unless someone deletes it. The timed expiry options are 10 minutes, 1 hour, 1 day, 1 week, 1 month, or 6 months. But I've seen pastes with "1 day" expiry stick around for weeks. The system is not rigorous about enforcement. If you need something gone, delete it yourself and verify by checking the raw URL directly. The syntax highlighting dropdown covers most languages — Python, JavaScript, Go, Rust, Terraform, YAML, JSON, SQL, and about forty others. But it doesn't cover everything. Custom or niche languages won't highlight properly, and sometimes the auto-detection picks the wrong one. I had a paste of HCL config that got highlighted as PowerShell because the keywords overlapped enough to fool the heuristic. Manually selecting the language fixes this but costs you nothing more than a click.
Pastebin also offers paste expiration through their API with authenticated requests, which raises your rate limit to about five requests per second. You generate an API key from the site settings page and pass it as a header. The documentation is adequate but thin on examples. The endpoint structure is straightforward though — POST to create, GET to retrieve, DELETE to remove. There's no batch delete, which is annoying if you're cleaning up a bunch of temporary test pastes. Here's the part where I should mention the limitations because they matter. Pastebin strips some characters and normalizes line endings in ways that can corrupt certain file types. I found this out the hard way when someone pasted a base64-encoded binary payload and the trailing padding got mangled during transmission. The paste looked fine visually but decoded to garbage. This happens with any content that's sensitive to whitespace or special characters. If you're sharing executable scripts or encoded data, verify the round-trip before sending the link to anyone. Security-wise, pasting secrets is a non-issue only if you understand how the platform works. Paste content is public by default unless you set it to private, and even private pastes are accessible to anyone who knows the URL. There's no encryption at rest that I'm aware of from the user side. I once saw a junior engineer paste an AWS access key into a "private" paste and share the link in a public Slack channel. The key was rotated within hours but it was entirely preventable. Use environment variables or a secrets manager instead. Always.
Get the Full Details

For people who just want a quick way to share a chunk of text without creating an account, Pastebin handles that fine. For anything involving sensitive data, large files over a few megabytes, or content that needs to persist with access controls, you're better off with something like a Gist with a secret, a private pastebin alternative, or just a shared document with proper permissions. Pastebin is a tool, not a solution. It works well until the scenario it was never designed for shows up.