What You Actually Get With the Practice Labs Ethical Hacker V10
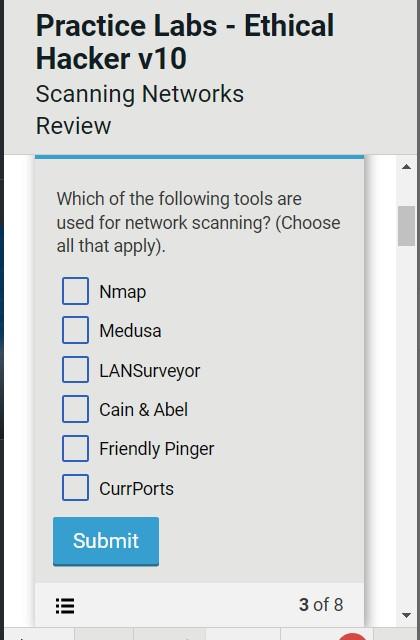
Practice Labs Ethical Hacker V10 is a cloud-hosted virtual lab environment designed to simulate real-world penetration testing and ethical hacking scenarios. It runs entirely in your browser using a remote desktop protocol, so there is nothing to install on your local machine. The platform handles provisioning, network isolation, and lab resets on the backend. You log in, launch a lab, and work inside a pre-built target environment that looks like a corporate network segment. The interface itself is unremarkable. You get a toolbar with a lab browser on the left, a console area in the center, and a timer at the top. Labs are organized by category — reconnaissance, web application attacks, privilege escalation, network exploitation, and so on. Each lab has step-by-step instructions, a points-based challenge structure, and an automated scoring system. The idea is to complete objectives before the timer expires and before you run out of points for failed attempts.
Getting Started With Practice Labs Ethical Hacker V10
You need an active subscription to access the content. Practice Labs sells this through enterprise contracts and also offers individual accounts through their website. Once you have credentials, you log into the Practice Labs portal, navigate to the lab catalog, and filter by "Ethical Hacking" or "Cybersecurity." The V10 content set includes over 100 hands-on labs spanning multiple difficulty tiers. Most labs take between 30 and 90 minutes to complete on a first pass. The provisioning process usually takes 3 to 5 minutes. When you click "Launch," Practice Labs spins up a containerized Windows target, sometimes a Linux target, and occasionally both. Your session gets isolated on a virtual private network with no internet access except for the tools intentionally provided inside the lab. This isolation is important because it means you cannot accidentally scan a real production system or hit a public IP by mistake. The tradeoff is that some labs feel slightly artificial since the targets are static images rather than live services. One thing most people figure out quickly: you need a decent monitor or at least a second screen. The lab interface uses three main panels simultaneously — the instructions, the remote desktop, and your notes. On a single 15-inch laptop screen, this becomes painful within ten minutes. I switched to a dual-monitor setup and the time I spent fighting with window management dropped significantly.
How the Labs Actually Work
Each lab presents a scenario with a clear objective. You might be told to find a vulnerable web application running on an internal server, exploit a buffer overflow in a custom service, pivot through a compromised host to reach a domain controller, or extract credentials from memory. The lab provides whatever tools are necessary inside the guest OS. You typically get Metasploit, Burp Suite Community, Nmap, John the Ripper, Hashcat, Wireshark, and various scripting environments depending on the lab topic. The scoring engine tracks your actions. It checks whether you have obtained the target credential, captured the flag, or achieved the stated goal. You earn points for successful objectives and lose points for certain actions depending on the lab's ruleset. Some labs penalize you for excessive recon traffic or for triggering certain IDS alerts. This is one of the more useful design elements because it forces you to think about operational security even inside a sandboxed environment. Here is a specific problem I ran into that took me about two hours to resolve: in one of the Active Directory exploitation labs, the Domain Controller would not respond to SMB queries after the initial enumeration phase. The target was still reachable via ping, and the RDP session remained stable, but `Get-Domain` and `BloodHound` queries would hang indefinitely. I tried restarting the AD services inside the VM, resetting the lab, and even re-launching the entire session. None of it worked. The workaround was to use `nbtstat -a` to discover the NetBIOS name resolution was failing while TCP connectivity remained intact. I then ran my queries against the IP address directly instead of the hostname, which bypassed the broken DNS resolution in that particular lab instance. I reported it through the support ticket system and it got marked as a known issue within a week.
Get the Full Details

What Beginners Miss About This Platform
The biggest mistake people make is treating the step-by-step instructions as a tutorial to follow linearly. The instructions exist to help you get unstuck, not to teach you the methodology. The actual learning happens when you deviate from the instructions and figure out the exploit path on your own. I recommend reading the objective only, launching the target, and spending at least ten minutes reconnoitering before you look at any guidance. This changes how you engage with the material entirely. Another thing that catches people off guard: the labs do not perfectly mirror real penetration test conditions. The vulnerabilities are often misconfigured services on deliberately vulnerable operating systems like Windows Server 2008 R2 or older Ubuntu releases. Real clients rarely run EOL operating systems with default credentials. The labs are excellent for learning tool proficiency and attack chain logic, but they are not a reliable proxy for modern enterprise security assessment. If your goal is to understand current threat landscapes, you should supplement this with live bug bounty platforms or CTF-style challenges that use newer software stacks. The timeout mechanism is another design choice worth discussing. Labs expire after a set duration, and when they do, your progress is lost unless you save your work externally. I started keeping a detailed notes file in a text editor alongside the lab, logging every command I ran, every IP address I discovered, and every successful exploit vector. This practice pays off when you return to a lab for review or when you need to document findings for a mock report. The built-in note feature exists but is limited to basic text input with no code formatting or command history retention.
Limitations You Should Know About
Practice Labs Ethical Hacker V10 has clear constraints. The virtual environment is resource-bound. If you run a CPU-intensive task like a full brute-force password attack with Hashcat, the lab VM will slow down noticeably. The provider throttles virtual CPU allocation per session, so complex crypto attacks that take seconds on bare metal can take minutes inside the lab. This is not a dealbreaker, but it affects pacing during timed challenges. The platform also lacks advanced red team scenarios. There is no living-off-the-land toolkit simulation, no custom payload development environment, no multi-stage lateral movement with realistic network segmentation, and no anti-analysis techniques built into the targets. If you are preparing for a CEH certification exam, this platform aligns reasonably well with the curriculum. If you are preparing for an OSCP or a real-world red team engagement, you will outgrow it quickly. I would recommend pairing it with TryHackMe for beginner-to-intermediate progression and then moving to Hack The Box or Proving Grounds for more realistic challenge environments. Another practical limitation is the lack of offline access. Everything requires an active internet connection to the Practice Labs infrastructure. If your connection drops during a lab, you lose your RDP session and potentially progress depending on the lab's auto-save configuration. I have lost two labs to ISP outages where the auto-save had not triggered yet. There is no downloadable VM version or local hosting option, so you are entirely dependent on their uptime and your own network stability.
Who Should Actually Use This
The platform works best for individuals who need structured hands-on practice in a safe environment and who do not want to build their own lab infrastructure from scratch. If you are studying for a certification that emphasizes practical skills — CompTIA PenTest+, CEH Practical, or similar — the lab content maps fairly well to those exam objectives. The point system also gamifies the experience in a way that keeps you moving through topics systematically rather than cherry-picking interesting ones. If you already have a homelab running VirtualBox with vulnerable machines like VulnHub targets or Metasploitable instances, you may not need this platform. Building your own lab gives you unlimited reset cycles, no timeouts, no resource throttling, and the ability to modify target configurations to match specific scenarios. The initial investment is higher in terms of hardware and setup time, but the long-term flexibility is substantially better. I maintain both options myself and use Practice Labs when I need quick scenario-based practice without the overhead of spinning up new virtual machines. The cost structure is subscription-based, which means you pay monthly or annually for access. Pricing varies depending on whether you are an individual or an enterprise customer. For a solo learner, the cost is comparable to other lab platforms on the market. For organizations sending multiple employees through training, the per-seat pricing can add up quickly, especially if team members rotate through labs frequently and consume concurrent session slots.
A Few Practical Tips From Actual Use
Save screenshots of your work inside every lab. The scoring system does not store your command history, and when a lab expires, you cannot go back and review what you did unless you documented it yourself. I organize my screenshots in folders by lab name and date, which makes it easy to reference during study sessions or interview preparation. Learn to use the built-in proxy and packet capture tools inside the lab VMs before you start attacking. Several labs include HTTPS inspection proxies preconfigured, and knowing how to route your browser traffic through Burp Suite inside the guest OS saves you from guessing at network configurations mid-challenge. This is especially relevant for web application labs where you need to intercept and modify requests on the fly. Do not rush through labs just to complete them. The value is in understanding the attack chain, not in checking boxes. I have seen people finish a lab in twenty minutes by blindly following instructions and then fail to explain the underlying vulnerability in an interview. Spend the time to read the MITRE ATT&CK mapping that Practice Labs provides for each lab objective. This connects your hands-on work to a recognized framework and makes the knowledge transferable to other contexts.