What actually shows up when you need it
You are standing in front of a production server at 2 AM. The application is erroring out and you need a systemctl command you cannot remember. You open a browser and search for Red Hat Linux Commands Cheat Sheet because your muscle memory has failed you. This is exactly what these sheets are built for. They are not reference documents you read cover to cover. They are emergency lookup tables for the commands you use once a week and immediately forget. A Red Hat Linux Commands Cheat Sheet is a condensed reference that maps commands to their flags, options, and common use cases. It covers things like package management with dnf and yum, filesystem navigation, process control, networking tools, and systemd management. The Red Hat variant differs from a generic Linux cheat sheet mainly in its focus on RPM-based package management and systemd-centric service control. Debian and Ubuntu cheat sheets will emphasize apt, dpkg, and different network configuration approaches. I spent three years managing a fleet of RHEL 8 servers before I ever stopped needing a printed sheet under my monitor. The one I kept at my desk covered about forty commands across six categories. It was dog-eared, had coffee stains on the dnf section, and I used it daily. That sheet saved me probably two hours per week in lookup time. Time I would have otherwise spent reading man pages for commands I just needed to run once.
The thing nobody tells you is that cheat sheets have a shelf life. A RHEL 7 sheet will mislead you on RHEL 8 if it does not account for the switch from systemctl legacy units to the newer namespace conventions. A sheet from 2019 will show you yum when you should be using dnf as the primary package manager. Always verify the OS version the sheet targets before you rely on it. I learned this the hard way when I followed an outdated guide and spent twenty minutes troubleshooting why a package installation command kept failing with a dependency resolution error that had nothing to do with the actual packages.
Core command categories you will actually use
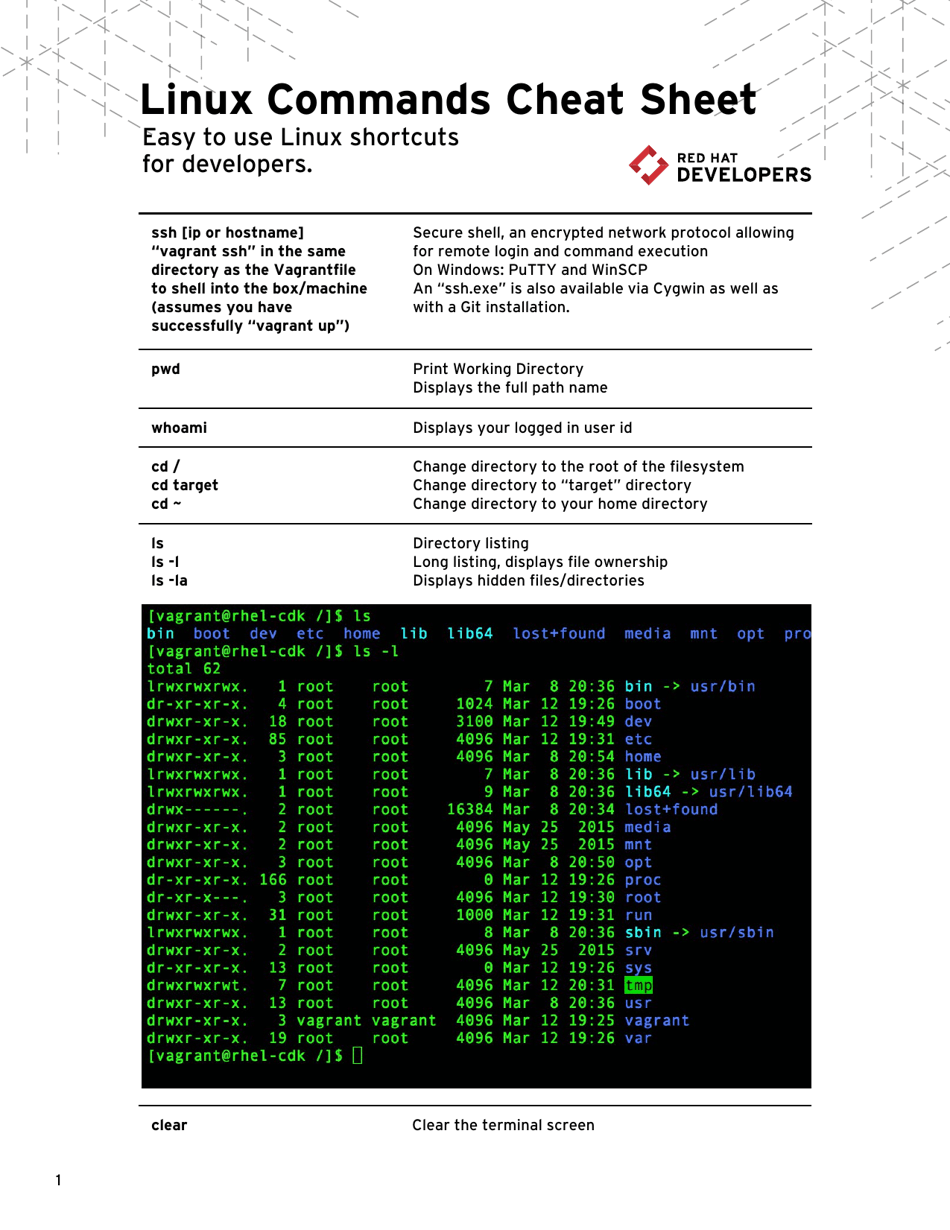
Filesystem operations form the backbone. cd changes directory. ls lists files with flags like -la for long format including hidden entries. pwd shows your current location. cp copies files. mv moves or renames them. rm removes files and directories, and you should always mean what you type when you use rm -rf because there is no recycle bin. find locates files by name, size, or modification time. grep searches text content within files. These are the commands that eat up most of your interactive shell time. Process management comes next. ps displays running processes. top and htop give you real-time resource monitoring. kill terminates processes by PID. pgrep finds processes by name. nohup and & allow background execution. job control with fg and bg switches between foreground and background tasks. I once had a compilation job that hung for six hours because I forgot to check the CPU temperature and the thermal throttling kicked in. The process was still running, but it was processing at about ten percent speed. Something a simple top command would have shown me in thirty seconds. Systemd commands replaced the old init scripts and they are now central to everything. systemctl status checks a service state. systemctl start and stop manage services. systemctl enable makes services start at boot. journalctl reads system logs. The key insight beginners miss is that systemctl is not just a service manager. It manages targets, sockets, timers, and mount points all through the same interface. When a service fails to start, the first thing you should run is systemctl status followed by journalctl -u to see the actual error. Most people just retry the start command and wonder why it keeps failing.
Get the Full Details

Package management on Red Hat systems
RPM is the underlying package format. DNF is the user-facing package manager. Yum still works but it is essentially a symlink to dnf in modern releases. Understanding the difference matters when you are automating installations or debugging dependency issues. dnf install
Yum remains in documentation everywhere. You will see it in tutorials, Stack Overflow answers, and older blog posts. Do not be confused into thinking yum is a separate tool you need to learn. On RHEL 8 and Rocky Linux 8 it is functionally identical to dnf. On RHEL 7 it is the primary tool and dnf is available as an alternative. The command syntax is the same across both. Just use whatever is already on the system you are working on.
Network commands and troubleshooting
IP addressing and interface management use the ip command now. Ifconfig and route are deprecated but still present on many systems for backward compatibility. ip addr shows network interfaces and addresses. ip link shows link layer information. ip route displays the routing table. ss shows socket statistics and replaced netstat. curl handles HTTP requests. wget downloads files. ping tests reachability. nslookup and dig query DNS records. netstat is still useful for legacy scripts but ss gives you the same information faster. The counter-intuitive thing about ss is that its output format is actually more useful than netstat for most debugging scenarios. Netstat sorts connections by state in a way that can hide active transfers. Ss shows you the exact socket buffer sizes and current transfer rates. When I was debugging a slow database connection last year, netstat showed the connection as ESTABLISHED and looked normal. Ss revealed that the socket buffer was stuck at 64 kilobytes when it should have been auto-negotiating to 256 kilobytes. The real issue was a firewall rule somewhere in the path that was fragmenting packets. Something neither command showed directly, but ss gave me the starting point for the investigation. Firewall management on Red Hat systems uses firewall-cmd or firewalld. Firewall-cmd --state checks if the service is running. Firewall-cmd --list-all shows current rules. Firewall-cmd --permanent adds rules that persist across restarts. Firewall-cmd --reload applies permanent changes. The permanent flag is where most people make mistakes. Adding a rule without --permanent means it disappears on the next reboot. Adding with --permanent without --reload means it does not take effect until you reload or restart firewalld. I have lost count of the number of times I have seen someone add a permanent rule, forget to reload, and then spend an hour wondering why the rule is not active.
File permissions and ownership
Chmod changes file permissions. The numeric system uses 4 for read, 2 for write, and 1 for execute. So 755 means owner has rwx, group has rx, and others have rx. 644 means owner has rw, group has r, others have r. Chown changes ownership. Chgrp changes group ownership. The -R flag applies changes recursively. ACLs with getfacl and setfacl provide more granular control when standard permissions are not enough. What people miss is that permission bits are only half the story on Linux. Extended attributes and SELinux contexts also control access. A file might have 777 permissions and still be inaccessible if the SELinux context is wrong. I spent an afternoon chasing a permissions issue on a web server where Apache could not read a PHP file despite the file having world-readable permissions. The actual problem was the SELinux context. The file was labeled with a type that Apache was not allowed to read. Changing the context with chcon or fixing it permanently with semanage fcontext resolved it. chmod would have solved nothing.
Where to find a current sheet
The Red Hat documentation site hosts official command references. Many sites aggregate community-maintained cheat sheets. The ones worth bookmarking are those that specify which OS version they target and which update they were last verified against. A sheet without a date stamp is a guess at best. I keep a personal sheet in markdown format that I update whenever I learn something new or encounter a command I forgot. It lives in my dotfiles repository and syncs across machines. The version control history shows how my needs changed over time. Early entries were mostly basic filesystem and process commands. Later entries added systemd troubleshooting, dnf transaction history analysis, and journalctl filtering patterns. The sheet grew from eight pages to twenty-two over three years. Each expansion came from a real problem I encountered and needed to remember the solution to. If you want something immediately usable, search for Red Hat Linux Commands Cheat Sheet and pick a result that references RHEL 8 or Rocky Linux 8. Avoid any sheet that still leads with yum as the primary package manager or mentions service commands instead of systemctl equivalents. Those are indicators the content is outdated. The commands themselves may still work, but the organizational structure and emphasis will be off for modern systems.
A few commands worth memorizing past the sheet
systemctl status gives you more information than you probably realize. Run it with the --no-pager flag to see the full output without the interactive pager blocking the end. Add -l to see complete log lines instead of truncated ones. These flags save time when you are reading output through an SSH session with limited terminal width. Dnf history lists package transaction history. Dnf history undo rolls back the last transaction. This is your safety net when an update breaks something. I use it maybe once a month, but when I need it, it is worth about an hour of my life. Without it I would be rebuilding systems or restoring from backups. Journalctl -u

Fstrim runs filesystem trimming on SSD storage. It is not something you need to run regularly if the system is configured for automatic trim. But checking whether it is enabled and running is a good maintenance task. A filled SSD without trim can see write performance degrade by seventy percent over six months of heavy use. The system will not complain. It will just be slow. Something you notice when you are trying to do routine work and wonder why everything feels sluggish. The sheet you keep visible should reflect the systems you actually manage. A sheet loaded with Debian commands is not helpful when you are on RHEL. A sheet with commands for a server you managed five years ago may not apply to the version you are running now. Update it. Print it. Tape it to your monitor. Or keep it in a terminal tab you never close. However you use it, treat it as a living document rather than something you download once and forget about.


