Understanding How Gartner's Risk Based Vulnerability Management Actually Works
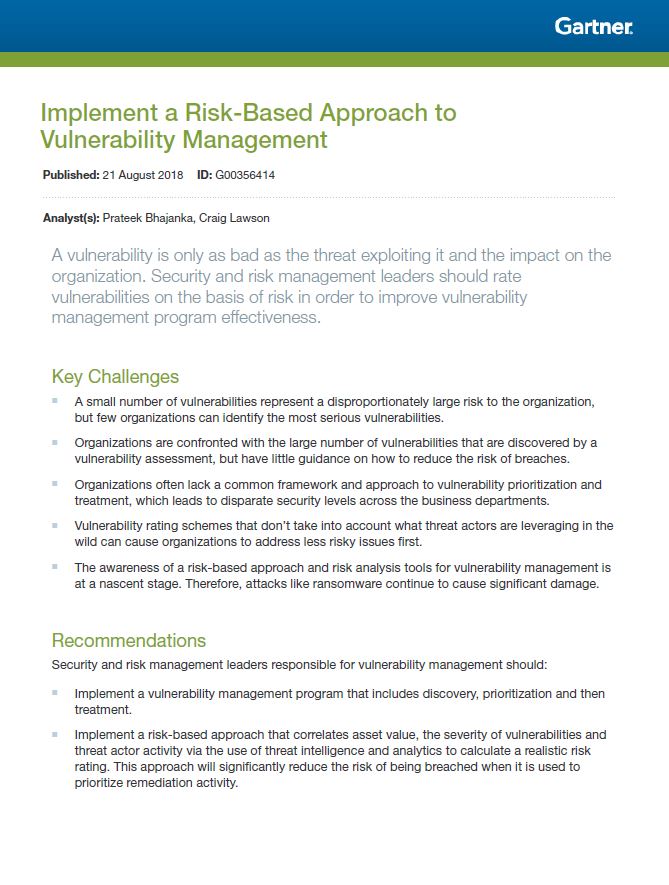
The Gartner approach to risk based vulnerability management Gartner is a shift away from chasing raw CVSS scores toward evaluating threats using business context, exploit likelihood, asset criticality, and compensating controls. Most vulnerability programs still operate on patch-everything-hunting for critical CVEs first. That method leaves teams burning through triage hours while the actual dangerous gaps remain unaddressed. Gartner's framework forces a structured conversation between vulnerability data, asset information, and threat intelligence before remediation starts. The core model combines three primary inputs. Vulnerability severity comes from standard scoring systems, though CVSS alone is insufficient. Asset criticality requires mapping each vulnerable host to its actual business function. Contextual threat intelligence pulls in real-world exploitation data, including whether the vulnerability is actively weaponized in your industry. Gartner argues that combining these inputs produces a risk score far more actionable than any single metric.
Implementing the Framework Step by Step
Start by inventorying every internet-facing asset with clear ownership. This sounds obvious but most organizations have critical servers running legacy applications where the owner is someone who retired four years ago. Without asset ownership, the contextual risk layer collapses because there is no one accountable for patching or compensating controls. Map assets to business processes using your CMDB or IT service management tool. Where the CMDB is incomplete, supplement it with passive network monitoring data and agent-based asset discovery. You will need to reconcile mismatches between tools manually, which is tedious. Next, integrate your vulnerability scanner output with external threat intelligence feeds. EPSS data from First Advantage works well here because it provides a probability score for exploitation within the next thirty days. Pair EPSS with vendor advisories and any applicable CISA known exploited vulnerabilities catalog. A vulnerability with a CVSS of 9.8 but an EPSS score below 0.01 and no active exploitation warrants a different response than one with a CVSS of 7.2 and confirmed ransomware usage in the wild. Gartner explicitly recommends using EPSS alongside CVSS because EPSS correlates more closely with actual compromise rates. Apply compensating controls as risk modifiers. Network segmentation, WAF rules, IPS signatures, and strict egress filtering can all reduce the effective risk of a vulnerability. Document these controls in your vulnerability management platform. Gartner notes that mature programs adjust risk scores dynamically based on control effectiveness, not static thresholds.
A Specific Problem I Ran Into and How I Fixed It
At a previous employer, we ran Qualys with CRD scoring enabled and the output consistently flagged our DMZ web servers as critical priority. The scanning tool was pulling CVSS 9.8 scores for a specific Apache Struts vulnerability and marking everything in the DMZ as urgent. The reality was that those servers sat behind three layers of network segmentation, a WAF with specific rule sets covering that vulnerability pattern, and strict outbound connectivity restrictions. The exploit path was severely limited despite the high base score. We were spending approximately forty hours per week triaging DMZ alerts that carried minimal actual risk, while internal database servers with weaker segmentation but lower CVSS scores were getting deprioritized. The workaround was straightforward but required manual configuration. I built a custom risk modifier in our vulnerability management platform that weighted compensating controls by effectiveness rating. Segmentation reduced risk by thirty percent, WAF coverage added another twenty-five percent, and restricted egress contributed fifteen percent. The composite risk score dropped the DMZ alerts into the medium-low category. Internal server risk scores increased proportionally because those assets lacked equivalent controls. This adjustment took roughly two weeks to configure and validate against historical incident data. After implementation, triage time dropped from forty hours per week to approximately twelve hours per week. The shift aligned our remediation queue with actual organizational risk.
Get the Full Details

Common Pitfalls That Break the Model
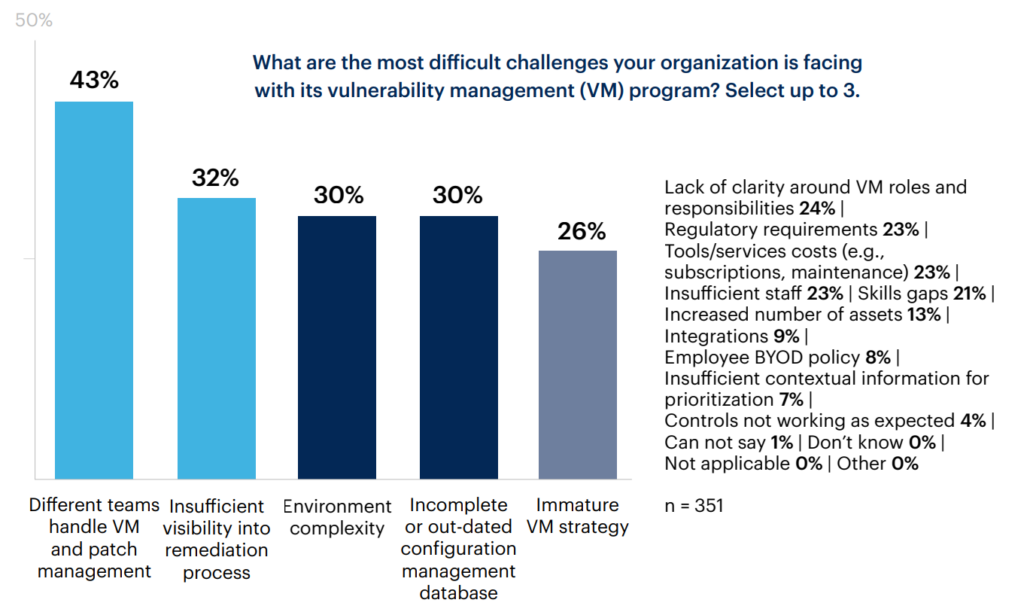
The biggest failure point is treating risk based management as a report generation exercise rather than a workflow integration exercise. If the risk scores stay in a PDF export and never feed into your ticketing system, nothing changes. The risk prioritization needs to exist inside the actual work order creation flow. Use API integration between your vulnerability platform and ServiceNow, Jira Service Management, or whatever ticketing system your team uses daily. Score-based filtering should auto-generate tickets with SLA targets tied to risk level, not publication date. Data quality is the second failure point. Asset criticality scoring depends on accurate CMDB data. When the CMDB contains outdated or fabricated entries, the risk calculation inherits the errors. I have seen environments where the criticality engine automatically classified all cloud workloads as low value because the CMDB lacked proper tagging. This caused a complete misallocation of remediation effort. Implement a monthly CMDB audit with automated reconciliation against live discovery data. Require business unit sign-off for any asset marked as critical. This adds bureaucratic overhead but prevents catastrophic scoring errors. The third pitfall is assuming EPSS data applies universally. EPSS coverage is strongest for widely scanned CVEs in common software stacks. Specialty applications, internal-only tools, and niche OT systems frequently have no EPSS data. When EPSS is unavailable, default to conservative assumptions based on CVSS vector completeness and known exploitation trends rather than dropping contextual scoring entirely. Setting a threshold where CVEs without EPSS automatically become high priority introduces its own bias and negates the risk-based approach.
When Risk Based Management Does Not Work
Organizations with fewer than five hundred endpoints and minimal complexity often see limited return on investment from a full Gartner-aligned implementation. The overhead of maintaining asset criticality mappings, threat intelligence integrations, and compensating control tracking typically outweighs the benefit when you are already managing patch cycles manually. A simpler prioritization model using CVSS plus basic asset classification produces comparable results with less operational friction. Scale matters significantly here. Regulated industries with prescriptive compliance requirements sometimes conflict with risk based approaches. PCI DSS, HIPAA, and certain government frameworks mandate specific patch timelines based on vulnerability severity levels. A risk adjusted schedule that defers a CVSS 9.0 patch for six months because compensating controls are in place may satisfy Gartner methodology but violates explicit compliance obligations. Build a separate compliance queue that runs parallel to the risk-based queue. Do not attempt to merge them.
Tool Selection Considerations
Gartner's framework is tool-agnostic but implementation complexity varies dramatically across platforms. Qualys VM with CRD scoring covers most of the methodology out of the box but requires configuration work for custom risk modifiers and compensating control weighting. Tenable.io offers similar capabilities through its prioritized vulnerability scoring feature. Rapid7 InsightVM builds contextual intelligence directly into its platform but the risk modeling is less transparent and harder to customize. Microsoft Defender for Endpoint provides risk scoring for endpoint-level vulnerabilities but lacks the broader asset context that the full Gartner model requires. If your organization already has a major platform deployed, evaluate whether upgrading to the advanced edition unlocks sufficient risk-based features to justify the cost increase. The licensing jump from standard to advanced typically runs between two thousand and eight thousand dollars annually depending on scope. The additional feature set includes EPSS integration, contextual threat data, and more granular compensating control tracking. These features directly support the Gartner framework. Skipping the upgrade and using standard editions requires building manual adjustments through custom reports and workflows, which reintroduces the very inefficiency the framework aims to eliminate. The fundamental shift risk based vulnerability management demands is accepting that not all vulnerabilities deserve immediate attention and not all systems deserve equal protection. That acceptance is uncomfortable for teams trained to treat every critical finding as an emergency. The methodology produces better outcomes precisely because it forces discipline around prioritization. The tradeoff is upfront investment in data quality, tool configuration, and workflow integration that most security budgets do not readily accommodate.