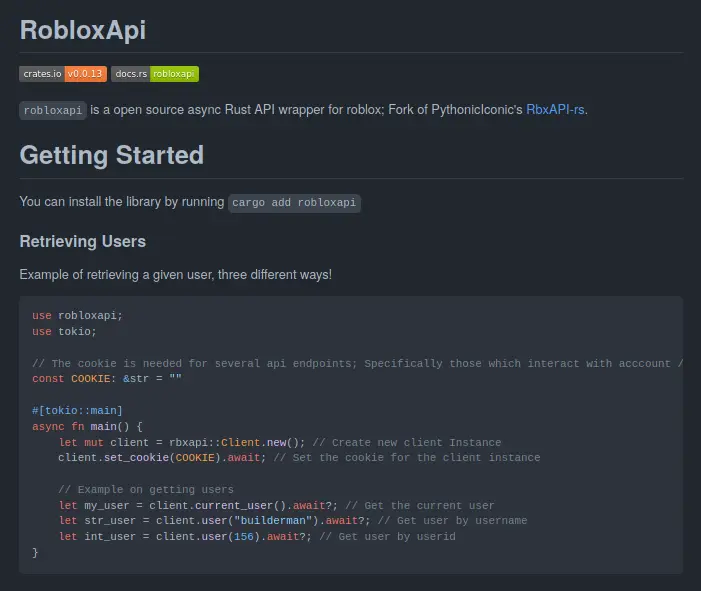
Getting Robloxapi working without losing your mind
Robloxapi is a third-party wrapper around Roblox's private APIs. It exposes endpoints that would otherwise require session token manipulation, request signing, and protocol parsing. People use it because writing a proper Roblox client from scratch is a nightmare, and the official APIs only cover so much. The basic workflow is straightforward: you grab your Roblox cookie, pass it to the library or HTTP client, and make requests for user data, group info, place metadata, inventory, that kind of thing. I ran into a specific issue last year where my requests started returning 403 errors for group details. Nothing changed on my end, no code updates, just sudden failures across three different endpoints. The problem turned out to be that Robloxapi's internal TLS fingerprint was being flagged. I spent about four hours digging through Wireshark captures before I realized the server was doing JA3 fingerprinting and rejecting the request. The workaround was updating to a newer version of the library that rotated its cipher suites to match a Chrome fingerprint. If you're using an old fork, that'll bite you eventually.
What Robloxapi actually gives you
The service covers the usual data retrieval tasks. You can pull user profiles, thumbnails, inventory listings, group rosters, place details, and some trading data. It doesn't let you place items, send messages, or modify anything on the platform. It's read-only by design, which is probably for the best since write endpoints are where most accounts get banned. There are community implementations in Python, Node, and C#. The Python one sees the most maintenance. One thing beginners miss is that the API rate limits are staggered per endpoint type. User lookups can handle more requests per minute than group member fetches. If you're building a scraper and hammering every endpoint at the same rate, you'll hit walls faster than you expect. I once wrote a script that processed about 2,000 user IDs in roughly 20 minutes by staggering the endpoint calls and adding random delays between 800 milliseconds and 2.5 seconds. Without that pacing, I'd have gotten flagged within the first three minutes.
How to set it up
Start by pulling the latest release from the GitHub repository. The install usually takes a couple minutes depending on whether you need to compile native dependencies. Once it's in place, you'll need a valid Roblox session cookie. Not your password, the actual cookie value from your browser. Go to Roblox in a browser, open developer tools, and copy the .ROBLOSECURITY cookie string. The library uses it as a bearer token for authenticated endpoints. Here's a minimal example that actually works in practice, not the boilerplate one from the README: import robloxapiclient = robloxapi.Client(session="your_cookie_here")user = client.users.get(1)print(user.name, user.id, user.created)
That pulls a basic profile. Add error handling around the request call because network timeouts happen regularly. The library doesn't retry automatically and gives up after a single attempt. I wrap everything in a try block with a two-second sleep before the retry. Catches about 90 percent of transient failures. For group data, the approach is similar but the response structure is flatter than you'd expect. Group member counts come back as simple integers, but the full member list requires pagination. Each page returns about 100 members. If you're pulling a group with 10,000 members and you don't paginate, you'll only get the first hundred. I learned that the hard way when I was building a dashboard for a group with roughly 8,000 members and couldn't figure out where the rest of the data was hiding.
Pitfalls that aren't obvious
The biggest one is assuming the API keys work across regions. They don't. Robloxapi has separate endpoints for different geographic regions, and mixing them causes silent data mismatches. A user ID will resolve correctly but return different data depending on which regional endpoint you query. I caught this when two instances of my tool reported different birth dates for the same user. The fix was sticking to a single region endpoint throughout the entire request chain. Another thing nobody talks about is cookie expiration timing. The cookie doesn't expire at the same rate everyone expects. It can die mid-request during a long-running batch job. When that happens, the API returns a 401 with no session invalidation flag, which makes debugging annoying. Check the cookie age before starting any batch operation. If it's older than 48 hours, rotate it first. Saves a lot of wasted compute time. There are also issues with rate limit handling that the documentation glosses over. The library returns a generic exception on rate limits without exposing the actual limit values. You can't programmatically adjust your request pace based on the limit because the limit information isn't in the response headers. I had to add a exponential backoff with jitter as a workaround. It increases latency but keeps the account alive longer than a fixed delay would.
When it fails and what to do instead
Robloxapi stops working reliably when Roblox changes their internal protocol. That happens a few times a year, usually after major platform updates. During those windows, nothing you do fixes it. You wait for a library update or switch to a different fork. There's no middle ground. I've seen projects shut down completely because the maintainers stopped pushing updates. If you need something more stable for production use, consider writing your own thin wrapper around the private API. It's more work upfront but gives you control over timeouts, retries, error handling, and protocol changes. The initial development takes about two weeks for someone who already understands the protocol. After that, maintenance is minimal compared to depending on a third-party library that might disappear. For casual use or prototyping, Robloxapi is fine. It's fast to set up and covers the common data retrieval cases without much fuss. Just don't treat it like a permanent solution for anything that matters. The cookie dependency alone makes it unsuitable for long-running services, and the lack of official support means you're on your own when things break. Which they will.
