What a Solution Architect Cyber Security Actually Does
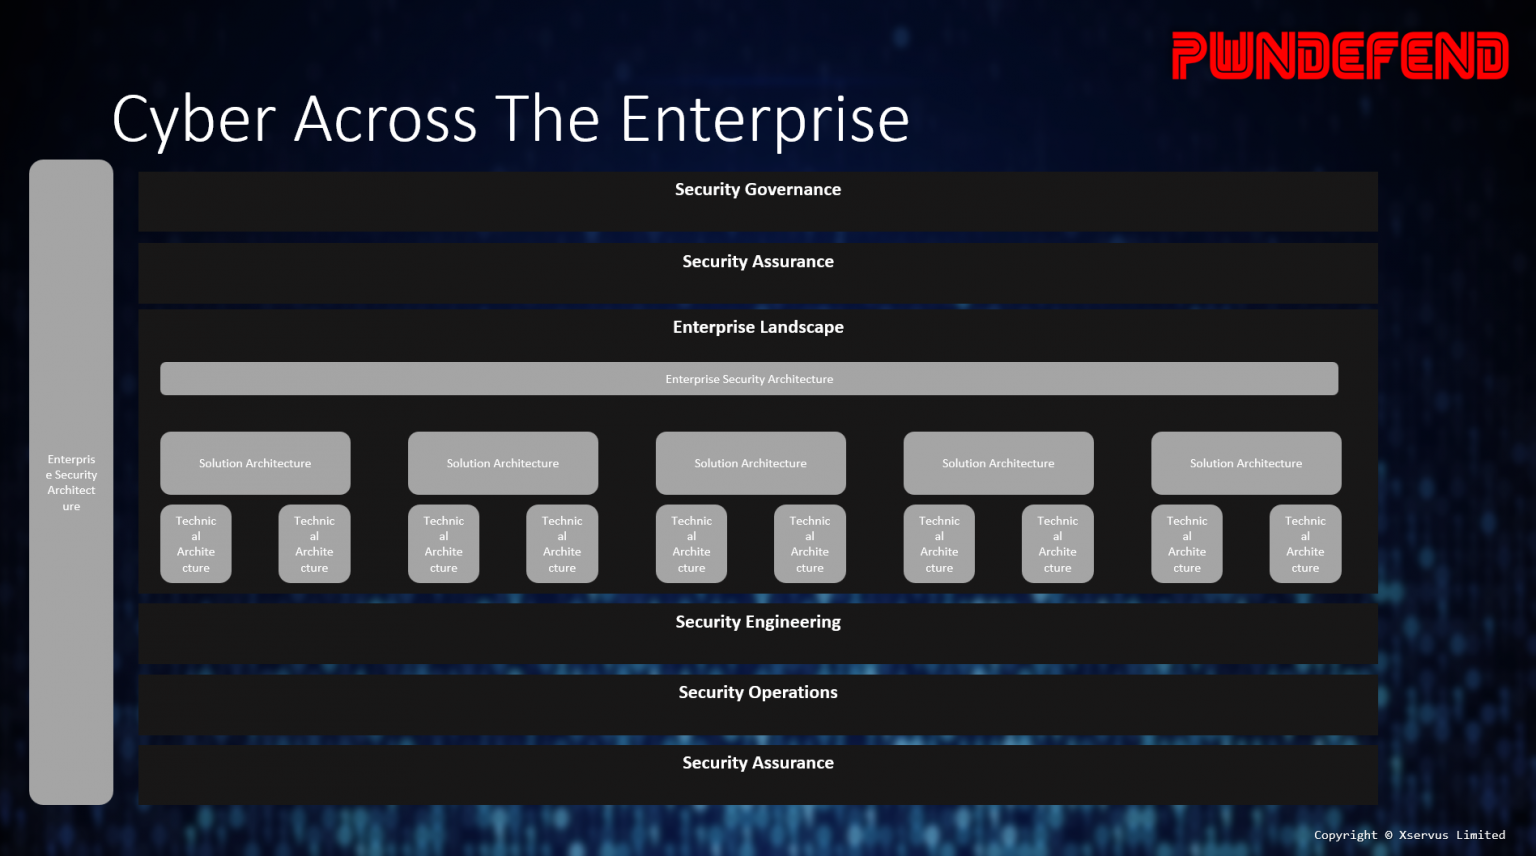
The role gets thrown around a lot in job postings. The reality is more boring and more specific than the titles suggest. A Solution Architect in cyber security is the person who translates business requirements into technical security controls, then makes sure those controls don't break the stuff they're supposed to protect. You design the architecture. You own the risk decisions. When something goes sideways at 2 AM, you're the one figuring out whether it's a false positive or a real breach before the CISO calls. I spent five years in this position before moving to a different angle of the industry. The work is less about picking tools and more about making decisions with incomplete information. Most of the time you're working from outdated assumptions about how your infrastructure actually behaves. I've seen more projects fail because the architect assumed a perimeter existed than because they couldn't find the right product.
Getting Into Solution Architect Cyber Security
There's no single certification that qualifies you. The path most people take involves a mix of hands-on infrastructure experience and formal security training. You need to understand networking at a level that lets you explain why something can or cannot talk to something else. That means knowing IP routing, DNS resolution, TLS handshakes, and what actually happens between a client and a server when you type a URL. Without that foundation, you'll design architectures that look correct on paper and collapse under real traffic patterns. Certifications like CISSP give you the vocabulary. A security+ or SSCP helps early on. But the things that actually matter come from experience with tools and incidents. I learned more about zero trust implementation from watching three production systems get misconfigured than from any course I took. The same goes for zero-day response, identity federation, and cloud security. These are skills you build by doing the wrong thing and then fixing it. Let me walk through how I actually approach designing a security architecture for a new environment. First, I map the data flows. Not the intended flows. The actual flows. I pull network diagrams from the infrastructure team and then verify them against packet captures or at minimum flow logs. The gap between documented and actual flows is where every security program fails.
Building the Architecture
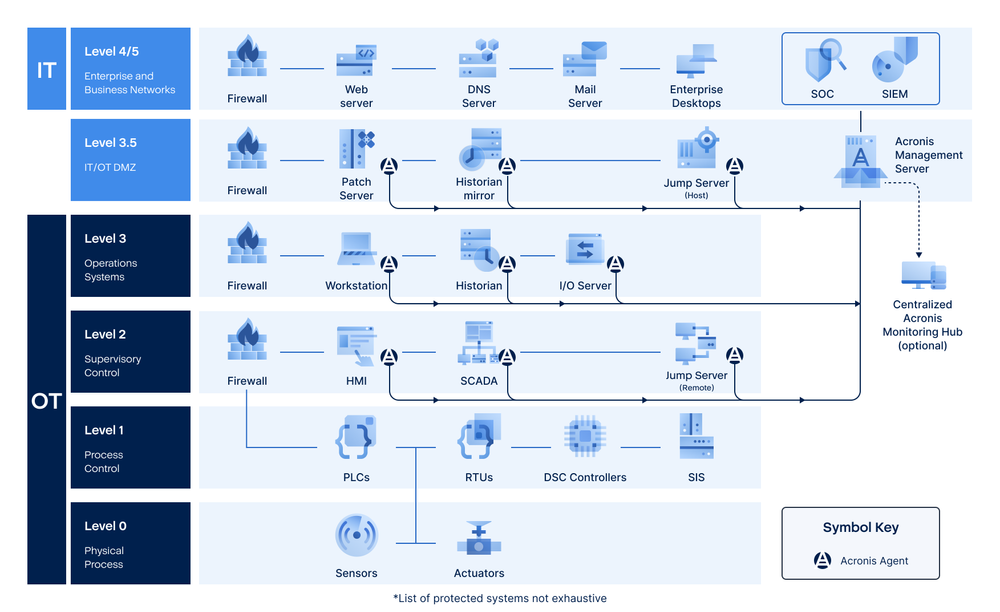
Start with the data. Identify what you're protecting, where it lives, who needs access, and what regulatory or compliance obligations apply. Then work backward to the controls. This is the part most people get wrong. They start with controls and try to fit data to them. That produces bloated architectures with overlapping tooling and zero coverage on the actual risk surface. I use a decision matrix that weighs three factors for each control: coverage, performance impact, and operational overhead. Coverage means how much of the threat landscape it actually addresses. Performance impact is non-negotiable in production environments. Operational overhead is the hidden killer. I've seen teams pick a solution because it covered a framework requirement and then spend eighteen months trying to make it manageable. That's not architecture. That's spreadsheet compliance. One specific example from my experience. I was working on a hybrid cloud deployment where the existing on-premises firewall rules were never documented beyond a sticky note in someone's desk drawer. The application team wanted to move to AWS without changing any network controls. I had to reverse-engineer the firewall rules from ACL logs spanning six months while simultaneously designing a replacement architecture using security groups and NACLs in the cloud environment.
Get the Full Details
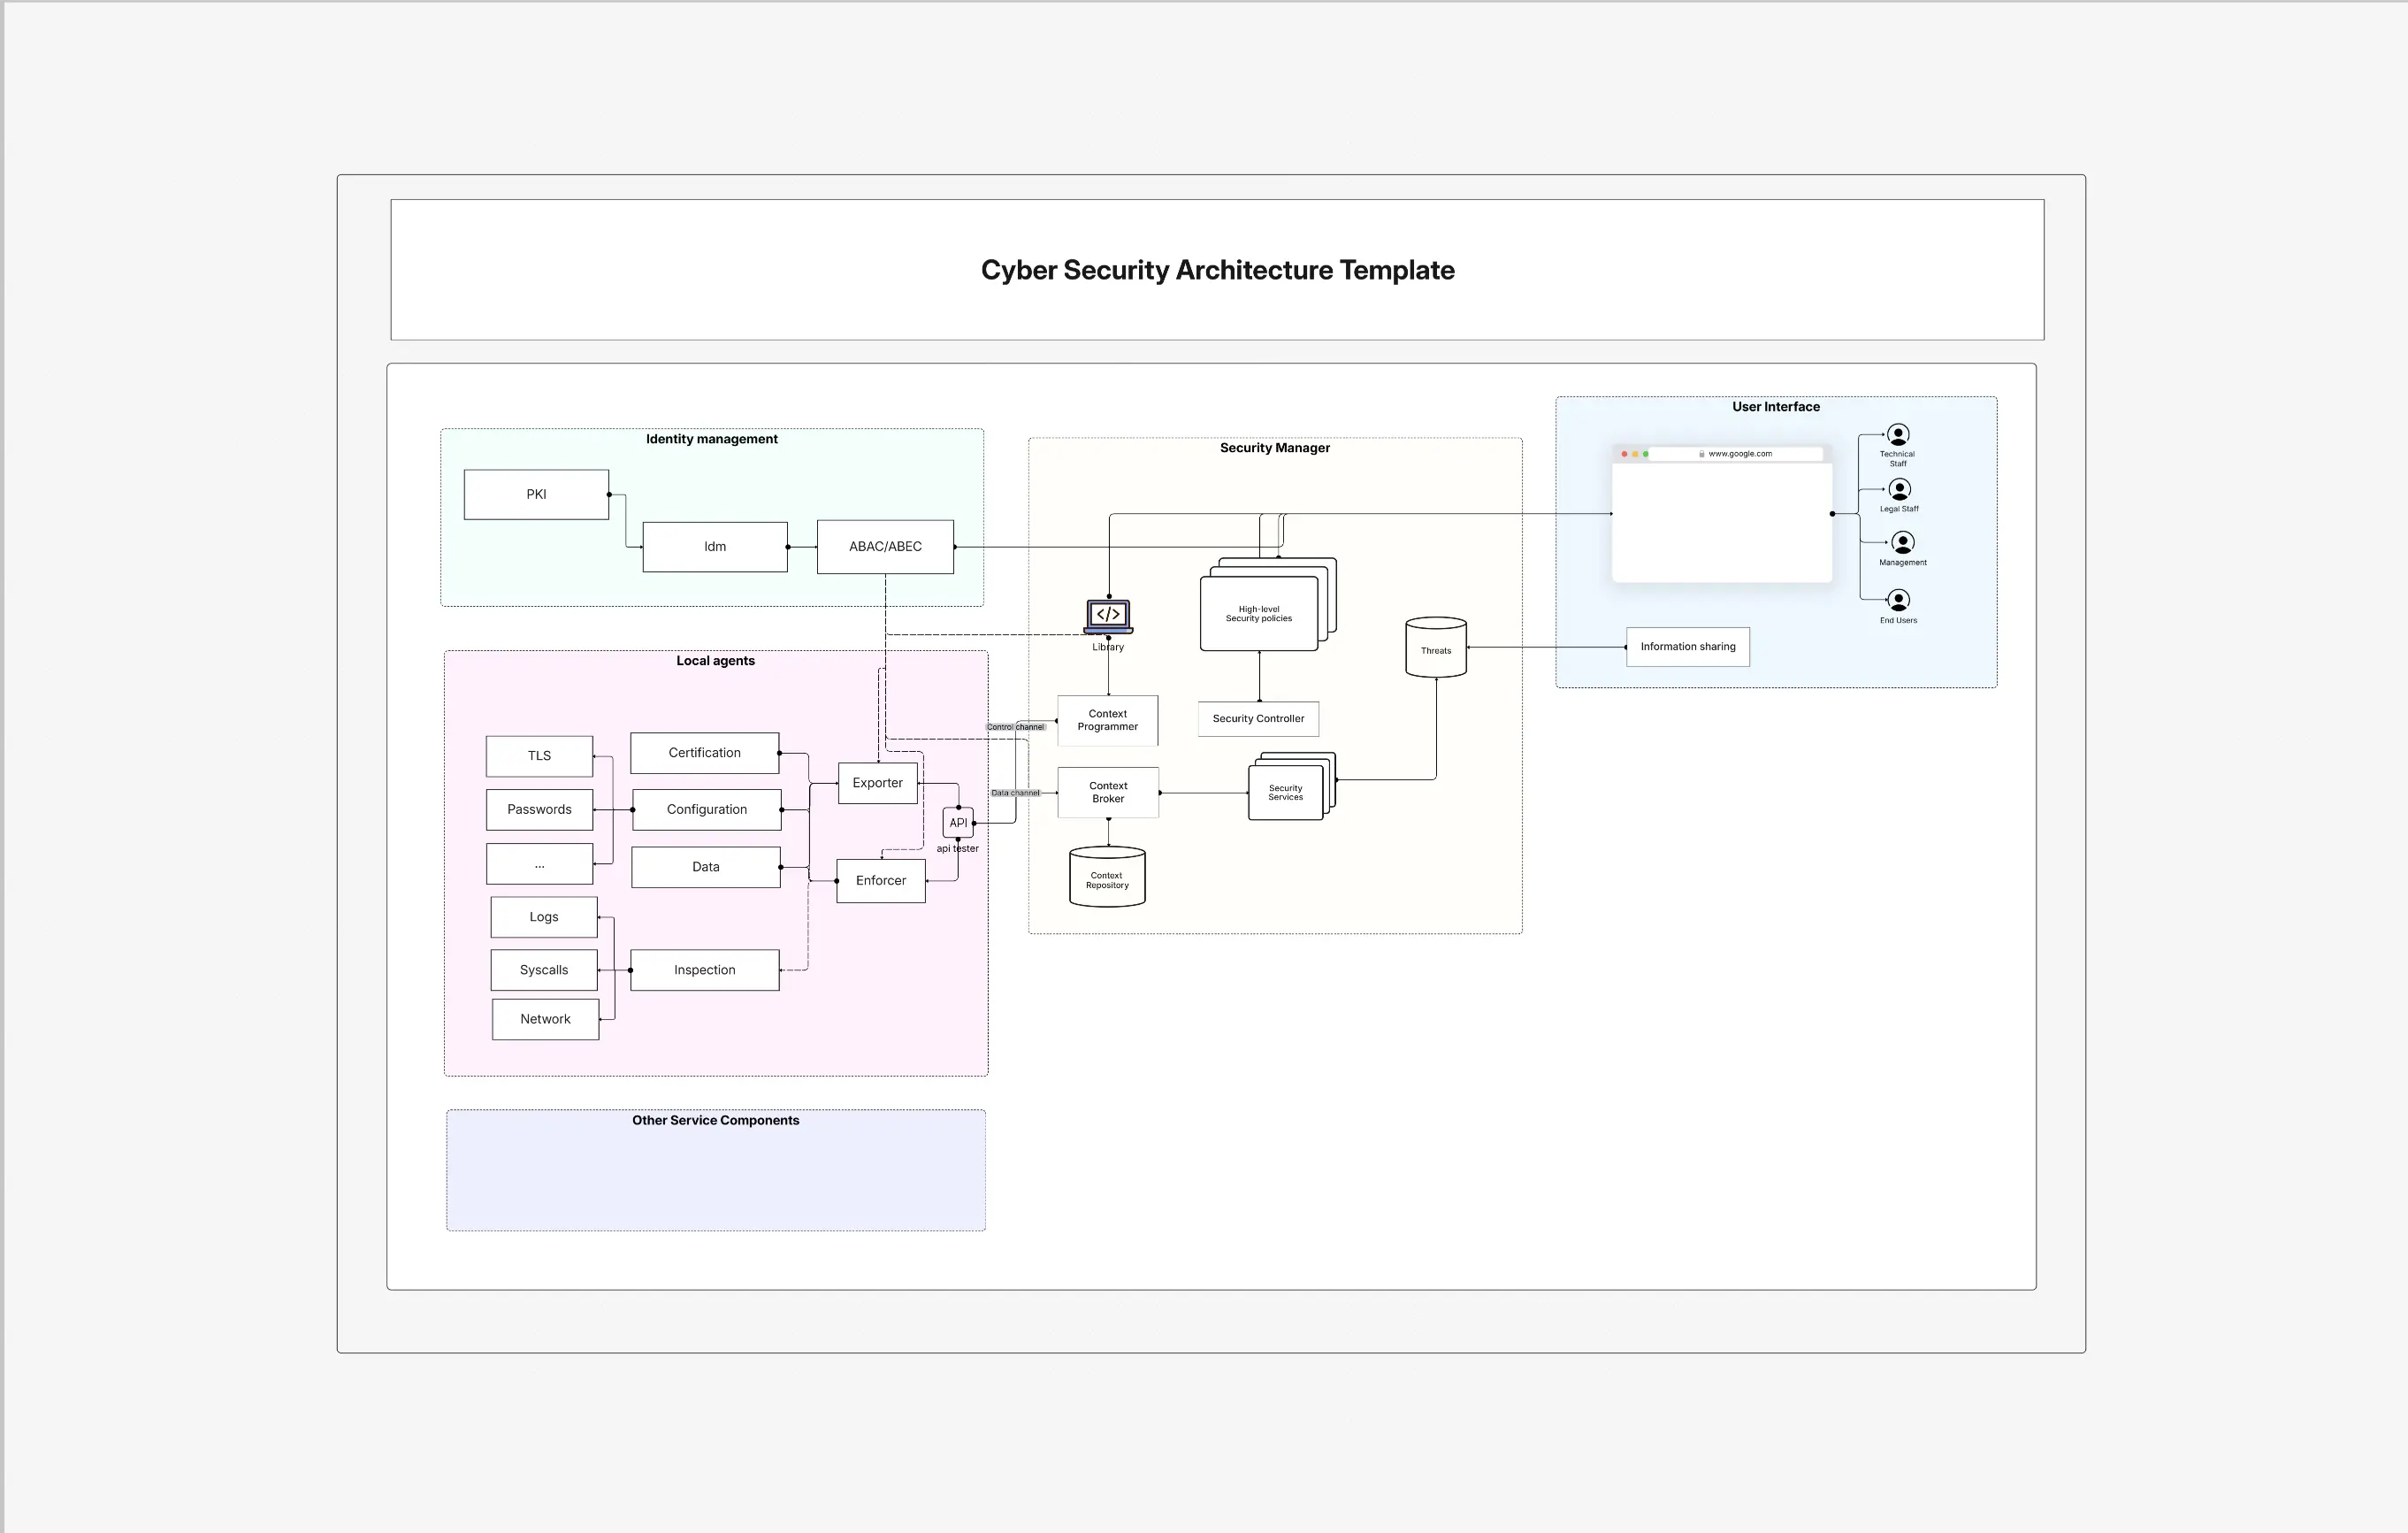
The workaround I used was to instrument every edge router with sFlow and feed it into a temporary analysis pipeline. That gave me visibility into actual traffic patterns. I then built the new architecture around observed behavior rather than assumed behavior. The project would have been delayed for weeks trying to get sign-off from the infrastructure team on undocumented rules. Instead, we had data within two weeks and could make decisions based on what was actually happening. Identity architecture is where most teams struggle. Zero trust isn't a product you buy. It's an architecture pattern that requires you to authenticate and authorize every request regardless of where it originates. I've seen organizations implement zero trust by adding another VPN. That's not zero trust. That's just VPN rebranding. The counter-intuitive part of zero trust is that it usually requires MORE authentication, not less, and it makes single sign-on a liability if not designed correctly. When I build identity architectures, I separate discovery from authorization. Discovery identifies who or what is making the request. Authorization determines whether that entity should have access to the specific resource at that moment. These two functions should never share the same policy store. Mixing them creates authorization sprawl that becomes impossible to audit.
Common Pitfalls in Solution Architect Cyber Security Work
The biggest mistake I see is designing for the ideal state instead of the current state. You'll see it in projects where the target architecture looks beautiful in a slide deck but requires changing every system at once to implement. That never works. You need to design the migration path with equal care to the destination. I usually define three phases: immediate remediation of known gaps, medium-term restructuring of vulnerable control planes, and long-term alignment with the target architecture. Each phase should produce measurable risk reduction that you can report to stakeholders. Another pitfall is over-relying on perimeter-based controls. This is especially relevant now with cloud workloads and remote workers. A traditional DMZ model assumes you can identify and protect the network boundary. Modern architectures often have no clear boundary. I shift the security focus from network perimeter to workload identity and data classification. Controls should travel with the data, not protect a location. Here's something people don't expect. Microsegmentation often reduces security more than it improves it when implemented incorrectly. I ran into this on a project where we segmented every workload into its own VLAN and applied strict access policies. The result was that legitimate management traffic couldn't reach certain endpoints because the segmentation rules didn't account for out-of-band management channels. We ended up with a network that was harder to manage and not significantly harder to compromise. The fix was to segment by data sensitivity rather than by workload type and apply different controls based on classification level rather than network location.
Cloud security architectures have their own set of problems. Multi-cloud setups tend to produce duplicate tooling and inconsistent policies. I recommend a centralized security policy layer that maps to each cloud provider's native controls. This means writing your policies in a provider-agnostic format and then translating them during deployment. Tools like Open Policy Agent or cloud-native policy languages help here, but the translation step is manual and error-prone. I spend more time on the policy mapping than on the actual implementation.

What Nobody Tells You About the Role
You'll spend a significant amount of time explaining your decisions to people who don't have the technical background to understand them. This is part of the job. A security architecture that can't be communicated to stakeholders will get modified or abandoned. I've had architectures rejected because the risk explanation required more than three slides. That's a feature of the role, not a bug. Learn to explain complex technical concepts in plain language. The role also requires constant context switching. You might be designing a microservices security model in the morning and troubleshooting an SSL certificate issue in the afternoon. The mental shift between architectural thinking and incident response is real and it's exhausting. I've learned to keep a personal knowledge base of common patterns and solutions. It saves about an hour per day compared to reconstructing context from scratch. One limitation of this work is that architecture decisions are often irreversible without significant cost. When you choose a specific encryption key management approach or a particular identity federation standard, you're making commitments that affect the entire system lifecycle. I've seen teams lock themselves into a proprietary solution because it was easier to implement initially. The vendor lock-in cost was three times the original savings within two years. Always consider the exit path before choosing the entry point.
Another practical limitation is that no architecture handles insider threats effectively without sacrificing operational efficiency. Full monitoring of every user action creates too much noise to be useful and raises serious privacy concerns. The realistic approach is to combine behavioral anomaly detection with least-privilege access and regular access reviews. This catches the majority of insider incidents without requiring surveillance-level monitoring that most organizations can't sustain. The Solution Architect Cyber Security role isn't about picking the best tools. It's about making trade-offs with incomplete information and living with the consequences. The best architects I've worked with were the ones who admitted uncertainty clearly and built decision frameworks that could be revisited as new information became available. Security architecture is an iterative process, not a destination. Treat it that way.