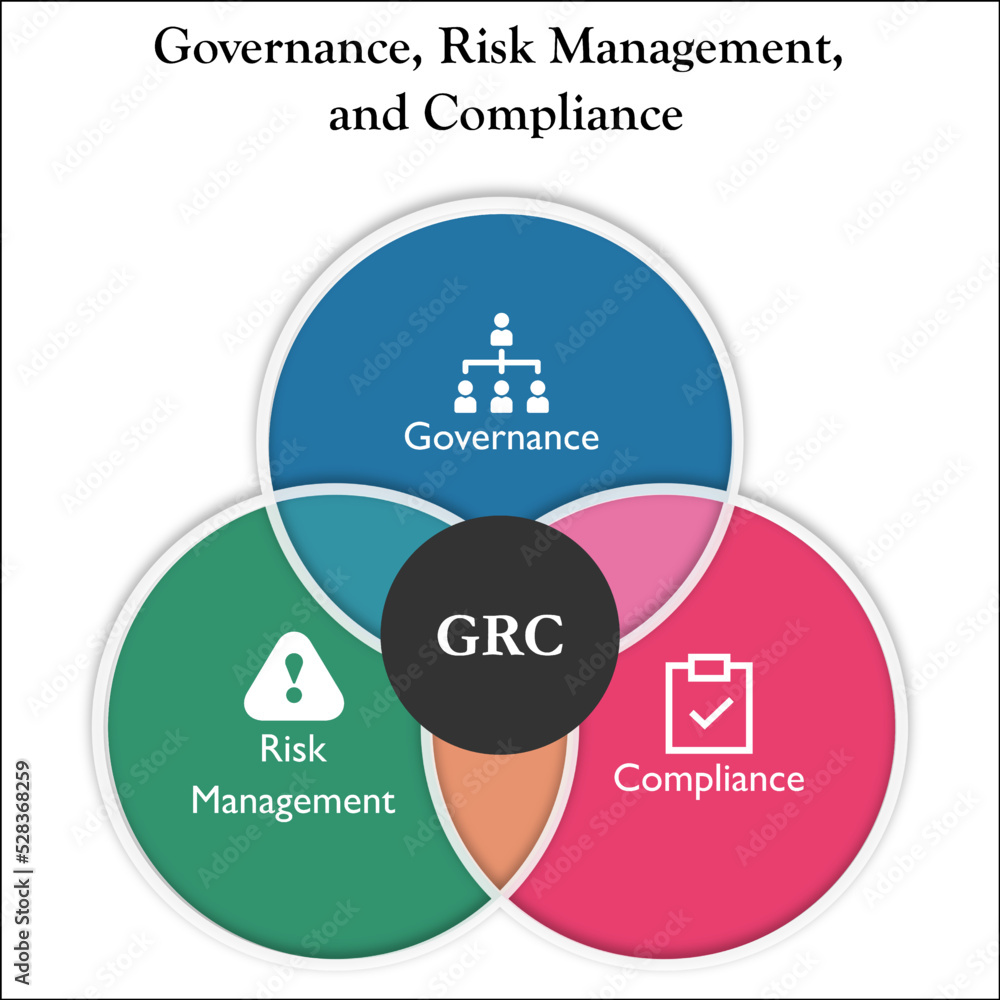
Understanding How GRC Laws Actually Work in Practice
Governance, Risk, and Compliance law isn't one single document you can download and follow. It is a sprawling intersection of federal regulations, industry-specific statutes, and international frameworks that shift depending on where you operate and what data you handle. If you are running a SaaS company in the EU handling health data, you are looking at GDPR combined with HIPAA obligations. If you are in financial services in the US, you are dealing with SOX, FFIEC, and SEC rules simultaneously. These layers don't sit neatly on top of each other. They overlap, contradict, and create gaps that auditors will exploit. Most people entering this space start by looking for a checklist. That approach breaks down quickly because the legal requirements change faster than any static document can track. A more functional way to think about it: GRC law exists to establish accountability for how an organization identifies risk, governs its response, and demonstrates compliance to regulators. The "law" part varies by jurisdiction and sector. The structure part is consistent. I spent several years building compliance programs from scratch for mid-market tech companies. One specific problem stands out. We had just implemented SOC 2 Type II controls for a client in the payment processing space. The auditor came in and asked for evidence of access reviews. Standard requirement. But the access review process we had in place pulled from Active Directory logs only. We missed a secondary admin panel that the engineering team had built six months prior and never added to the IAM system. The auditor flagged it as a material weakness. Fixing it required retrofitting an entire shadow infrastructure segment into the review cycle. We ended up implementing a quarterly discovery scan using tooling like SailPoint identity intelligence to catch unauthorized admin paths before auditors did. That workaround cost us about three weeks of engineering time and roughly $12,000 in tool licensing, but it prevented a repeat finding on the next audit cycle. It also exposed that we had at least four other undocumented systems with elevated permissions we hadn't known about.
The deeper insight most people miss is that GRC law cares less about perfect security and more about demonstrable process. An auditor cannot audit a feeling. They audit documentation, change logs, training records, incident reports, and review signatures. This means a messy but well-documented process will pass an audit more often than a clean but undocumented one. I have seen both outcomes repeatedly.
Practical Implementation Steps
Start with a regulatory mapping exercise. Do not skip this even if it feels bureaucratic. You need to know exactly which laws apply to your organization based on data type, geography, and industry. Create a matrix that lists every applicable regulation alongside your current control status. Green for compliant, yellow for partial, red for absent. This matrix becomes your living document. Update it quarterly. Next, build your risk assessment framework. NIST RMF and ISO 31000 are the standard references. Neither is perfect. NIST is thorough but heavy on documentation overhead. ISO 31000 is more flexible but lacks the granular control taxonomy that auditors expect. The pragmatic approach is to use ISO 31000 for the actual risk assessment methodology and map the outputs to NIST SP 800-53 control families so you satisfy both frameworks with a single effort. This dual mapping typically cuts reassessment time by about forty percent during annual audits. Then implement continuous monitoring. GRC law expects ongoing oversight, not a once-a-year box check. Automated configuration auditing tools like AWS Config rules, Azure Policy, or open-source alternatives such as Open Policy Agent can provide real-time drift detection. Manual spreadsheet-based compliance tracking usually falls behind within six months and becomes a liability during inspections.
Get the Full Details

Training and awareness is the weakest link in most programs. I recommend mandatory quarterly sessions with scenario-based assessments rather than annual compliance video marathons. Realistic phishing simulations tied to actual incident data from your environment perform significantly better than generic training modules. Engagement rates jump from around twenty-two percent to over sixty-eight percent when the material reflects actual threats your organization faces.
Common Pitfalls and Where Programs Fail
The biggest failure mode is treating compliance as a project with an end date. It is not. Regulations get updated. GDPR amendments come out regularly. CCPA expands. New state privacy laws appear in the US almost every legislative session. Your program needs a permanent budget line and a designated owner who reports to the C-suite or board level. Programs owned by mid-level managers without executive sponsorship tend to get defunded the moment revenue pressure increases. Another pitfall is control duplication. Companies often implement separate control sets for different frameworks without reconciling them. You end up with three different incident response procedures for three different certifications, each with different escalation paths and documentation requirements. This creates confusion during actual incidents and multiplies audit preparation work by two or three times what it should be. Merge the procedures into a single unified playbook and map each section to the relevant framework controls in a crosswalk matrix. This usually reduces documentation workload by roughly thirty-five percent while improving actual operational consistency. GRC law also struggles in environments with high contractor or third-party reliance. Supply chain risk management is now a legal requirement under frameworks like the EU's Cyber Resilience Act and the US CMMC 2.0 for defense contractors. You cannot outsource compliance. Every third party processing your data must meet equivalent standards, and you must verify it. This means contractual requirements, audit rights clauses, and regular third-party assessments baked into vendor management processes.
Tooling and Resources
Commercial platforms like OneTrust, ServiceNow GRC, and Drata handle much of the automation burden. Drata in particular has become popular with startups because it integrates directly with cloud infrastructure and can automate control evidence collection in most cases within two to four weeks of deployment. For smaller organizations on tighter budgets, open-source options like LTG's Compliance as Code framework combined with Ansible or Terraform can achieve similar outcomes with more manual effort. The tradeoff is roughly six to eight weeks of initial setup time versus immediate platform functionality, but ongoing operational costs drop significantly after the first quarter. For regulatory text itself, the best free sources are the official registries. The EU's EUR-Lex database for European regulations, the Federal Register for US federal rules, and ISO's catalog for international standards. Commercial aggregators like Thomson Reuters or Wolters Kluwer add convenience but the primary sources are free and legally authoritative. Never rely solely on secondary summaries for compliance decisions. They sometimes miss recent amendments.

When GRC Frameworks Don't Apply
There are edge cases where strict regulatory compliance frameworks are neither required nor practical. Early-stage startups under a certain revenue threshold in most jurisdictions face minimal formal GRC law obligations. Small businesses below fifty employees with no regulated data are generally exempt from most mandatory reporting requirements. In these cases, adopting lightweight governance practices still makes sense. Documented basic policies, simple access controls, and annual risk reviews cost very little and provide meaningful protection. The moment you handle personal data at scale or operate in a regulated sector, those light practices become insufficient and expose the organization to regulatory action. International operations add another layer of complication. The EU's GDPR applies extraterritorially. Any organization worldwide that processes EU resident data must comply. The China PIPL has similar reach. Multinational companies often face conflicting legal requirements. Data localization laws in countries like Russia and China may prohibit transferring certain data to servers in the US or Europe, directly contradicting GDPR's data subject rights to erasure and portability. There is no clean legal resolution for this conflict. Companies typically resolve it through geographic data segmentation, keeping EU and Chinese user data on separate infrastructure with strict access controls preventing cross-border transfers. This adds operational complexity and usually increases hosting costs by fifteen to twenty-five percent but it is the only legally viable approach currently.