What This Actually Covers
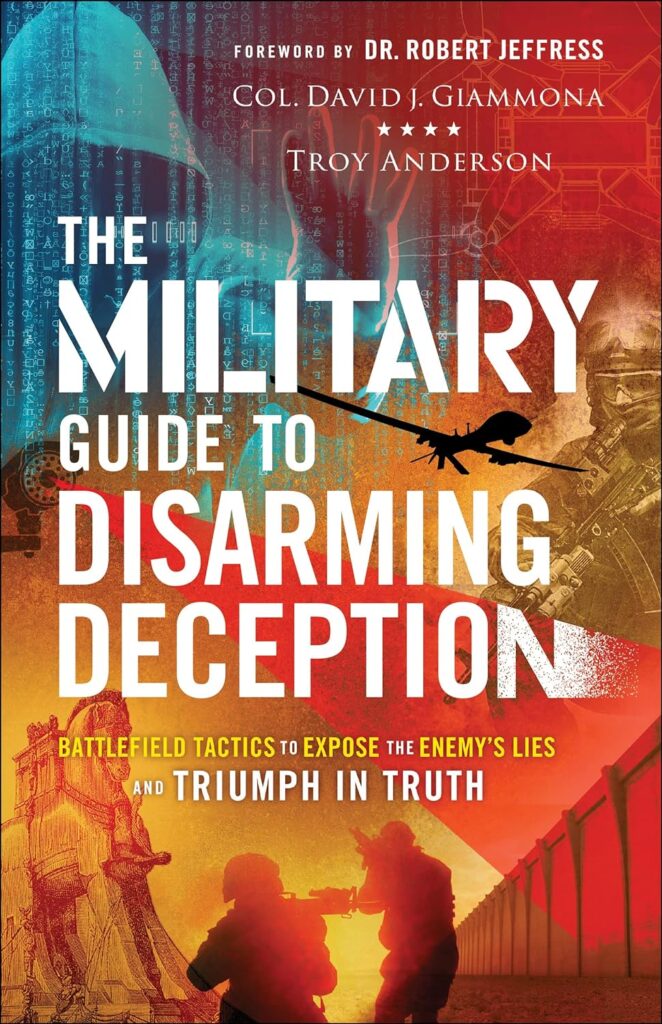
Most people hearing about disarming deception in a military context picture interrogations or enemy propaganda. The reality is broader and more mundane. It covers how operators at all levels learn to spot when information has been deliberately distorted, compressed, or fabricated — and how to strip that distortion down fast enough to make a decision before the window closes. The guide itself is not a textbook. It is a field reference built from after-action reviews, deception case files, and debriefs from units that have been burned by staged events, doctored imagery, and layered misdirection. It starts with one principle that most beginners miss: deception rarely arrives as an obvious lie. It usually comes dressed in partial truths, cherry-picked context, and plausible logistics. The trick is learning to recognize the shape of the distortion rather than getting stuck arguing about whether a single claim is true or false. A single verified detail in a report does not make the whole thing trustworthy. You have to look at the framing, the gaps, and the incentives behind who pushed the information forward. I will say plainly that working through this material feels slow at first. When I went through it during a deployment cycle, the hardest part was unlearning the instinct to trust the first coherent narrative. I spent too long trying to find the smoking gun in a piece of intel that was never about one lie. It was about six things arranged to look like one story. We had a situation where a local source gave us a route for a supply convoy, and the details were tight — times, vehicle types, even a partially correct radio frequency. I caught it because the frequency matched a pattern we had seen from a different region three weeks earlier. Someone was recycling an old signature to make a new tip look legitimate. The workaround was simple. We stopped treating the source as right or wrong and started treating the tip as a template, checking each element against independent sources instead of trusting the coherence. That cut our verification time from hours down to maybe twenty minutes because we knew exactly which pieces were redundant.
The guide organizes the work into phases, but not in the order most people expect. You do not start by defining deception. You start by learning to identify confirmation pressure, which is the internal urge to accept a claim because it matches what you already want to believe. Military operators are trained to be decisive, and that training can backfire when the information environment rewards speed over skepticism. The manual pushes you to separate the pace of your decision from the pace of your belief. That distinction matters more than any technique for spotting a planted story. From there it moves into signature analysis, which sounds technical but is mostly about pattern literacy. Every deception leaves a pattern. Staged events repeat minor inconsistencies. Fabricated documents over-index on certain descriptors. Doctored media often has artifacts that repeat across multiple versions. The guide gives you a checklist for running through these signals without turning every report into a forensic investigation. In practice, you are looking for repetition, over-polish, and gaps that serve a purpose. Real information is messy. Deception is usually too smooth.
How The Verification Process Works In Practice
The core method is called cross-hatching, and it is not as fancy as the name suggests. You take each major claim in a piece of information and run it through at least two independent channels before treating it as actionable. The channels should not be related to the original source. If a tip comes from an asset, you verify it through signals, open sources, or a second contact who has no reason to agree with the first person. The whole point is to break the echo chamber before it forms. I ran into a problem early on that the guide does not fully address. Cross-hatching slows you down if you treat every claim the same way. In a live operation, you cannot verify everything. The workaround is triage by consequence. You ask which claims, if wrong, would cause the most damage. You verify those first. Low-consequence claims you treat as working hypotheses until something forces you to reconsider. This usually cuts the verification workload by half without sacrificing safety, because most deception schemes rest on one or two key claims rather than every single detail. Another nuance that beginners miss is the role of plausible deniability traps. These are pieces of information designed so that if you act on them, you look foolish even if the information turns out to be true. The guide calls them confidence traps, but they function the same way. A common version is a report that includes a small, verifiable error deliberately planted to make you doubt the entire package when you discover it. The error is real, but it is bait. The correct response is to verify the surrounding claims independently rather than discarding the whole report.
Get the Full Details

The guide also covers digital deception, which has become the dominant problem over the last several years. Deepfakes, staged photos, spoofed communications, and AI-generated text are now routine. What people get wrong is assuming that advanced tech means advanced detection. Most digital deception is low quality. The high-effort stuff is rare. The practical approach is to look for metadata inconsistencies, lighting mismatches, audio artifacts, and logical gaps in the narrative rather than running every image through expensive forensic tools. A quick check of file age, geolocation clues, and source reliability usually catches the majority of attempts. Only the polished cases require the heavier equipment.
Common Mistakes That Waste Time
The biggest mistake is treating disarming deception as a one-time filter. It is not. Deception evolves. What worked last quarter may be predictable this quarter. You have to keep updating your mental checklist based on what you see in the field. Another mistake is assuming that if someone is lying about one thing, they are lying about everything. That is not how professional deception operators work. They mix truth into lies because total fabrication is hard to sustain. A source who has lied once is still a valuable source. You just adjust your verification weight. There is also the problem of overcorrection. After a unit gets burned by a deception, leadership sometimes orders a blanket freeze on acting until everything is fully verified. That is worse than the original problem. You lose operational tempo and signal your own caution to the other side. The better approach is to act on verified high-consequence claims and keep lower-consequence ones in a holding pattern until you have more certainty. You move forward while you confirm.
When This Approach Fails
I want to be honest about the limits. Cross-hatching and signature analysis depend on access to independent information channels. In environments where you control the data flow and cannot reach outside sources, the method collapses. You cannot verify anything if you only have one pipe. In those cases, the best you can do is track internal consistency over time and watch for shifts in tone, pacing, and detail level. It is a weaker signal, but it is all you have. Another scenario where the guide struggles is mass-scale information warfare. When the objective is not to trick one commander but to shape public perception across thousands of accounts, individual cross-hatching is too slow. You need aggregate analysis — trend tracking, network mapping, and source reputation scoring over time. The military has started building tools for this, but they are not part of the standard field reference yet. If your problem is broad narrative manipulation rather than targeted deception, you will need to supplement this guide with organizational-level intelligence methods. The bottom line is that disarming deception is a discipline, not a trick. It requires habit, not insight. The more you practice checking your own assumptions and cross-verifying before committing, the less likely you are to be led down a staged path. The guide gives you the framework. The work is in applying it consistently when you are tired, pressured, and tempted to accept the easy answer.