How the underground actually evolved
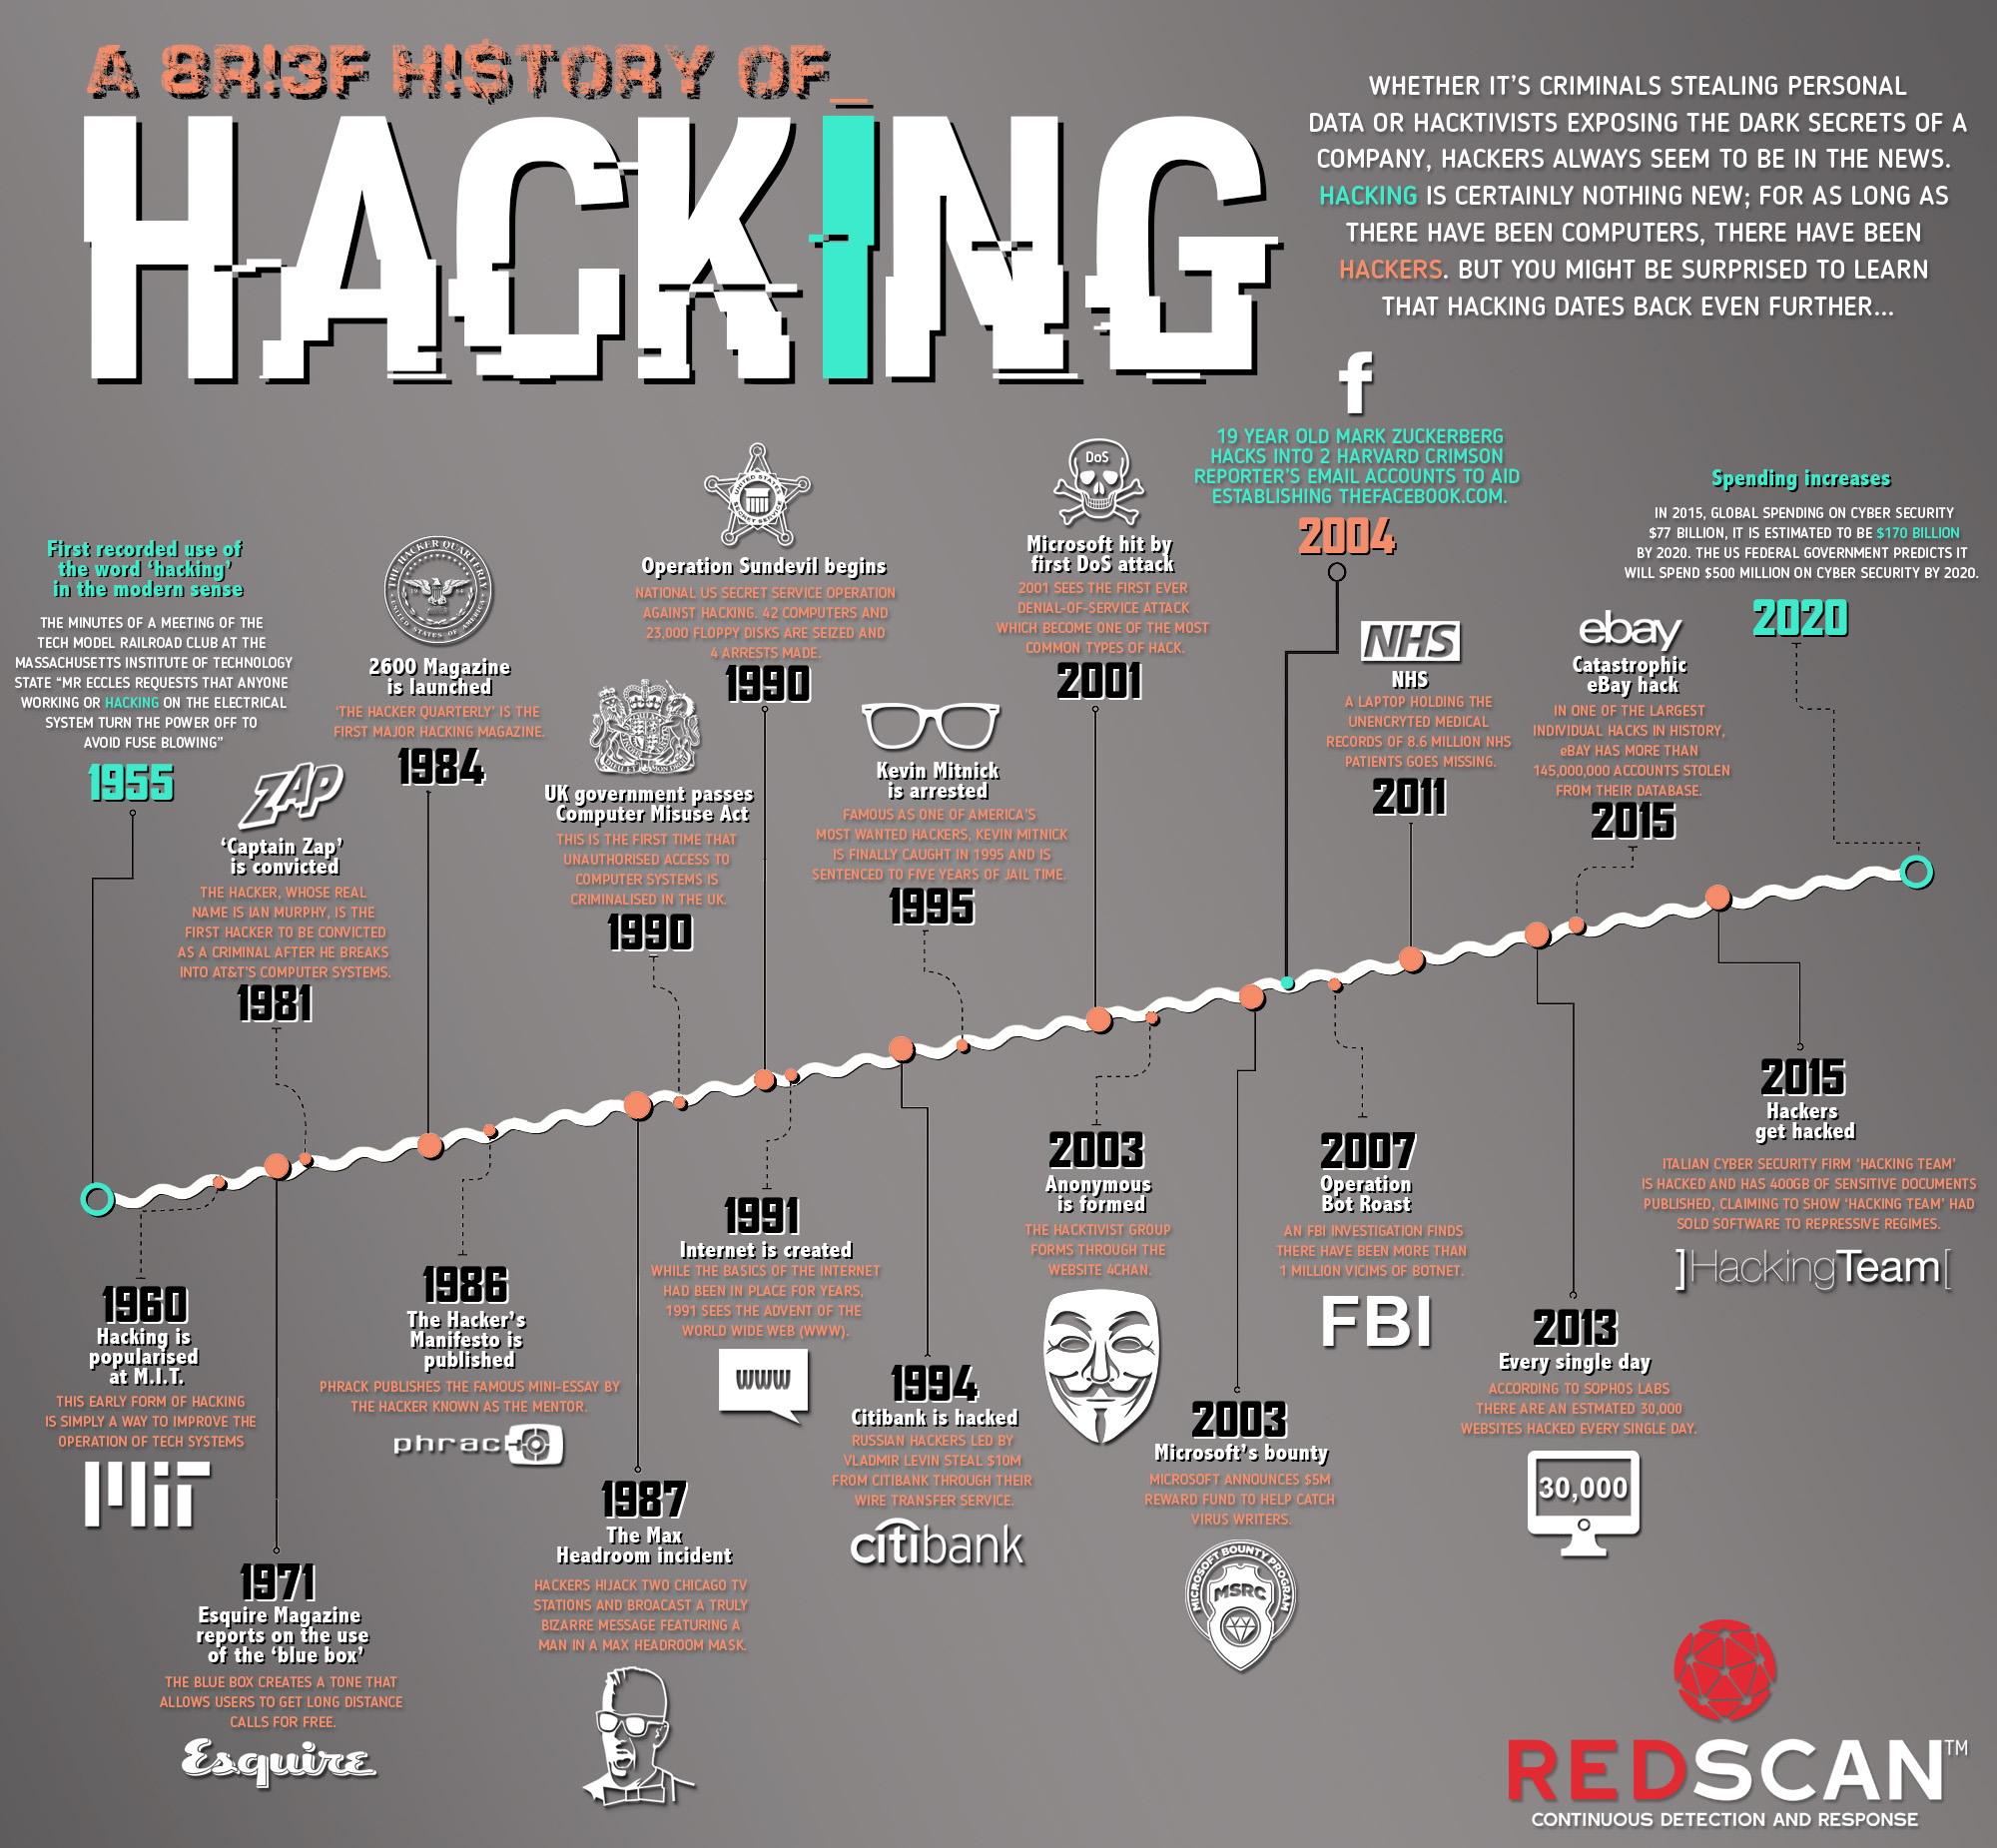
The idea of a "secret history" is mostly marketing. The real evolution of computer exploitation didn't happen behind closed doors. It happened in plain sight, scattered across bulletin board systems, Usenet newsgroups, academic papers, and conference halls. People talk about the mystique, but the mechanics are mundane. Understanding what actually happened requires separating the mythology from the technical reality. The timeline is messy, and most summaries get at least three significant events wrong.
The timeline most people mess up
Popular accounts usually begin with the 1983 movie WarGames and jump straight to the early 1990s Phreaking and the formation of groups like the Legion of Doom. This is incomplete and creates a distorted picture of what was actually happening on the technical side. The real story starts earlier, with ARPANET-era research and the 1972 Morris worm experiment by Robert Morris Sr. at Princeton. That was a networking vulnerability study, not a malicious attack, but it planted an idea in the heads of a lot of college students who would go on to shape the culture for the next decade. Then came the phone phreaking era, which most people think is just stories about blue boxes and John Draper. The technical work during that period was serious signal analysis. Researchers at Bell Labs were publishing papers on toll fraud mechanisms that the press ignored entirely. Those same mechanisms later became the foundation for VoIP exploitation techniques that are still relevant today.
What the Secret History Of Hacking Actually Looks Like
The pattern repeats across every major era. A vulnerability gets discovered, usually by accident, published in an academic setting, then quietly adapted by hobbyists who have nothing to lose and everything to learn. The knowledge flows from research into practice through mailing lists and underground forums. By the time mainstream media covers it, the techniques have already been through three iterations and nobody outside a small community has read the original source material. I encountered this pattern repeatedly throughout my career. Around 1998, I was working on network security for a mid-sized company when we discovered a buffer overflow in a widely used FTP server. The vulnerability had been known in the academic literature for about eighteen months. The exploit code was circulating on a private list, completely unmaintained, written by someone who clearly never intended it to be deployed in production environments. I spent two weeks cleaning up the copy-pasted code just to understand what it was actually doing. The final fix took approximately forty-five minutes once I understood the root cause. That is the typical workflow, not the dramatic Hollywood version.
Get the Full Details
The BBS underground and why it matters technically
Bulletin board systems were not just social networks. They were distributed learning platforms that operated without any central authority. People exchanged exploitation techniques through carefully coded messages. The culture of documentation that existed there is largely gone now, replaced by public vulnerability databases and CVE tracking. One thing that most beginners miss is the role of vulnerability disclosure practices before responsible disclosure became a standard concept. Researchers would sometimes release raw exploit code to test whether vendors would actually patch a flaw. This was brutal and often harmful to unsuspecting users, but it produced results faster than the current coordinated disclosure model in certain cases. The tradeoff is rarely discussed. I worked on a project in the mid-2000s where we needed to assess the exposure of legacy systems to a newly published vulnerability. The responsible disclosure timeline meant we had only seventy-two hours before full public exploit details appeared. We ended up building a passive scanning methodology that identified affected instances without triggering any active exploitation. This approach required deep understanding of the protocol implementation, not just the vulnerability signature. Active scanning would have been faster but would also have created additional risk for systems that were already unstable.
The academic pipeline that nobody talks about
Most significant vulnerability research originates from universities. The papers are behind paywalls, written in dense language, and rarely read by the people who could actually use the information. This is a structural problem, not a quality problem. The researchers are following normal academic incentives. The transfer from academic paper to practical exploit tool usually happens through a process I would describe as translation. Someone reads the paper, reconstructs the vulnerable environment, writes a working proof of concept, and then the technique spreads through underground channels. This translation step is where the actual knowledge transfer happens, and it is almost never documented. A counter-intuitive point that beginners consistently miss: the most dangerous vulnerabilities are often the ones described in the least dramatic academic papers. A paper titled something dry and technical about a minor edge case in a protocol implementation is frequently more exploitable in practice than a flashy presentation about a critical remote code execution flaw. The flashy ones tend to have well-known constraints or mitigations that the presenter mentions in passing but the audience skips over.
Tools and methodologies that actually shaped the culture
Debuggers. Network analyzers. Disassemblers. These are the real tools, not the cartoonish terminal interfaces with green text on black backgrounds. The early hackers who built lasting communities spent more time reading documentation and source code than running automated tools. Automation came later, and it solved different problems than the ones that defined the earlier eras. GDB, Wireshark before it had that name (Ethereal), IDA Pro, and source code analysis using tools like cscope formed the core toolkit. Understanding how to navigate a core dump or trace a network handshake manually was the skill that separated people who could exploit a system from people who could only run other people's scripts. Even now, in 2024 and beyond, this distinction matters more than most people realize. Automated vulnerability scanners will find the low-hanging fruit. They will miss the logic flaws, the race conditions, and the state machine violations that require understanding how the system actually works. I have seen engagements where a team spent two weeks running scanners and found exactly what the scanners are designed to find, while missing three critical vulnerabilities that required five minutes of manual protocol analysis to identify.
The surveillance and counter-surveillance evolution
Every technique develops a counter-technique. This is the part of the history that commercial security companies rarely acknowledge because it undermines their product narratives. The development of intrusion detection systems directly shaped how attackers changed their approaches. The evolution of encryption protocols directly responded to traffic analysis capabilities. This is an arms race, not a progression, and treating it as anything else creates false assumptions about the current state of security. One specific edge case that comes up constantly: attribution is almost impossible to determine reliably from technical evidence alone. The tools, techniques, and procedures leave patterns, but those patterns are deliberately designed to be misleading. IP addresses can be routed through multiple layers of infrastructure. Tool signatures can be copied or modified. Timeline manipulation is trivial. I have reviewed incidents where the initial attribution conclusion was almost completely wrong, and the correction came from behavioral analysis rather than technical indicators. This is uncomfortable for organizations that need clear answers for their boards and regulators.
Legal frameworks and why they matter more than most think
The Computer Fraud and Abuse Act, the GDPR, various national cybersecurity laws — these shape what is studied, published, and shared. Research that would have been freely discussed in the 1990s now exists in a legal gray area in many jurisdictions. This has had a measurable chilling effect on academic publishing in certain subfields. The change is not uniform. Some areas have become more open through responsible disclosure programs and bug bounty platforms. Other areas have become more constrained. The net effect is a redistribution of knowledge rather than a simple increase or decrease.
What actually persists from the early culture
Documentation. Sharing. The expectation that knowledge should be free. These values originated in the hacker culture of the 1980s and 1990s and they survive in open source software, in security research communities, and in the daily work of people who maintain the systems that modern infrastructure depends on. The romantic version of this history is wrong. The technical version is less exciting but more useful. The people who shaped this field were not secret master hackers operating from dark rooms. They were engineers, researchers, students, and sometimes vandals. They made mistakes. They got caught. They learned from each other. The record is available if you know where to look, and it is far less dramatic than the mythology suggests. If you want to understand this history, start with the primary sources. Read the original papers, not the summaries. Look at the mailing list archives from the late 1980s and early 1990s. Examine the source code of early security tools. The patterns become obvious when you see them in context rather than through the lens of later retellings.
The practical takeaway is straightforward: the techniques evolve, the tools change, but the fundamental dynamics remain the same. Vulnerabilities exist in software. People find them. Some share the findings responsibly. Some do not. Systems get patched. New systems introduce new vulnerabilities. This cycle has been running since the first networked computer was connected, and it will continue regardless of how the story gets told.