What You Actually Need to Know About Complying With Third Party Risk Management Regulations
The regulatory landscape around third party risk management has gotten messier in the last few years, and if you're trying to keep your organization compliant, most of what you'll find online will either oversimplify the problem or push a compliance software tool. Neither approach actually helps. What follows is a practical breakdown of how these regulations work in practice, where they overlap, and the few concrete steps that matter for keeping your audit findings to a minimum. Third Party Risk Management Regulations refer to the growing set of laws, standards, and supervisory guidance that require organizations to assess, monitor, and mitigate risks arising from their relationships with vendors, suppliers, and other service providers. These aren't a single regulation. They come from multiple sources: sector-specific rules like the EU's DORA (Digital Operational Resilience Act) for financial services, the OCC's guidance on third-party relationships for banks, state-level privacy laws that flow downstream to your vendors, and emerging frameworks from regulators like the SEC regarding cybersecurity disclosures. The common thread is that regulators now expect documented processes for due diligence, continuous monitoring, and incident response involving any third party that touches your operations or data. The tricky part nobody mentions often enough is that compliance isn't just about having a vendor assessment questionnaire. Regulators look for evidence that you're actually using those assessments to make risk-based decisions. If you send out a 200-question risk assessment to every vendor and then treat the responses as a checkbox exercise, you haven't met the spirit of the regulation. I learned this the hard way during an audit where my team had a complete vendor risk assessment program on paper but no one could explain why we had classified a cloud infrastructure provider as low risk when that provider processed 80 percent of our customer data. The auditor asked me to show the risk scoring methodology and the justification for each risk level assigned. We couldn't produce anything coherent. That audit resulted in a finding.
The workaround we implemented was straightforward but required organizational change rather than just process change. We tied our risk classification to concrete data: data classification level of what the vendor handles, the integration complexity with your core systems, and whether the vendor has sub-processors in jurisdictions with weaker data protection. This eliminated the subjectivity that was causing problems. It also meant that when we reassessed, we had actual criteria instead of a senior analyst's gut feeling, which auditors clearly prefer even if it feels less flexible.
Where the Real Regulatory Pressure Comes From
Most people think about GDPR or CCPA as privacy regulations and separate themselves from third party risk rules. They're not separate. When a regulator investigates a data breach, they examine whether you conducted adequate due diligence on the vendor that caused the breach. The question isn't whether GDPR mandates third party risk management directly. The question is whether your failure to vet that vendor constitutes a violation of GDPR Article 28 requirements for processor agreements and due diligence. That's how these regulations connect in practice. DORA is arguably the most aggressive example currently in force. It requires EU financial entities to manage operational risk from ICT third-party service providers with a level of rigor that goes well beyond what most standard vendor risk programs already do. Key requirements include direct oversight of critical ICT service providers, contractual clauses covering audit rights and exit strategies, concentration risk analysis, and incident reporting frameworks. If your organization falls under DORA's scope, standard vendor management processes won't cut it. You need a dedicated framework. Most teams treat this as a project. It's better treated as an ongoing operational capability because DORA doesn't have a one-time compliance window. For non-financial organizations, the regulatory pressure is more fragmented but no less real. The SEC's cybersecurity disclosure rules, effective for fiscal years ending after December 15, 2023, require public companies to disclose material cybersecurity incidents within four days and describe their material cybersecurity risk management processes in annual filings. If a breach involves a third party, that third party's role becomes part of your disclosure narrative. Regulators will scrutinize whether your risk management processes were adequate given the involvement of that vendor. Same pattern repeats in healthcare with HIPAA's Business Associate Agreement requirements, in healthcare IT with HITRUST expectations, and in payment processing with PCI DSS requirement 12.8.
Get the Full Details
Building a Program That Actually Satisfies Regulators
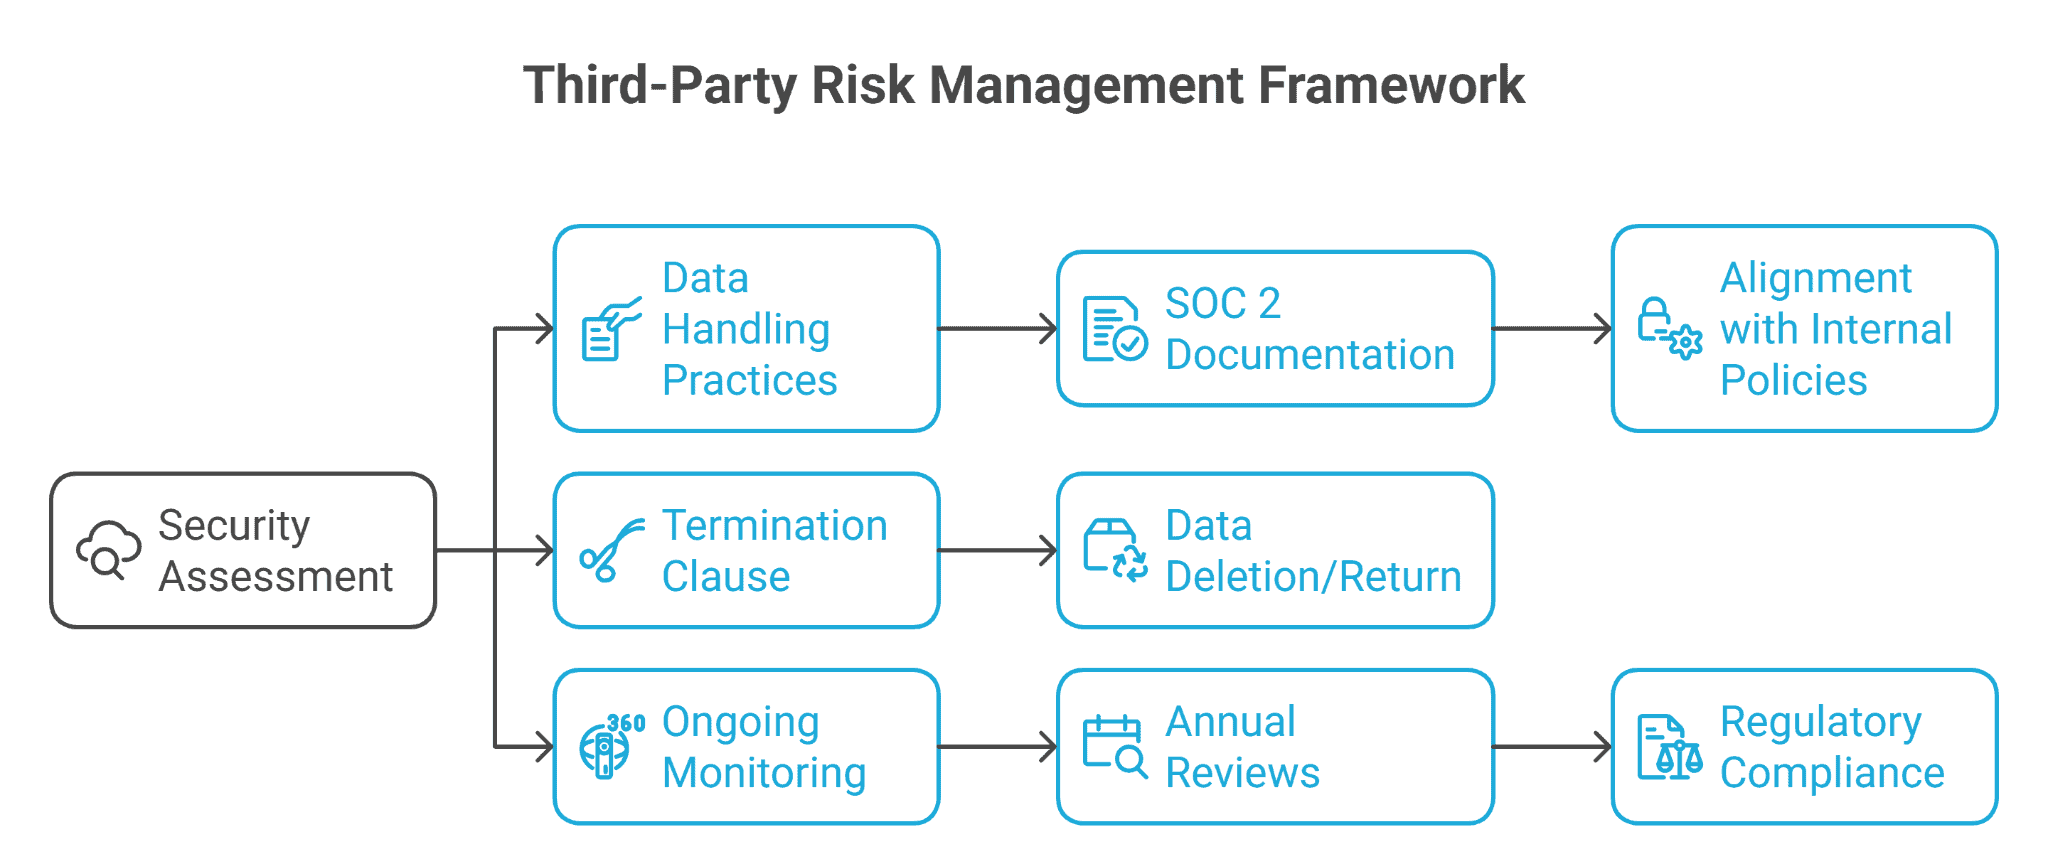
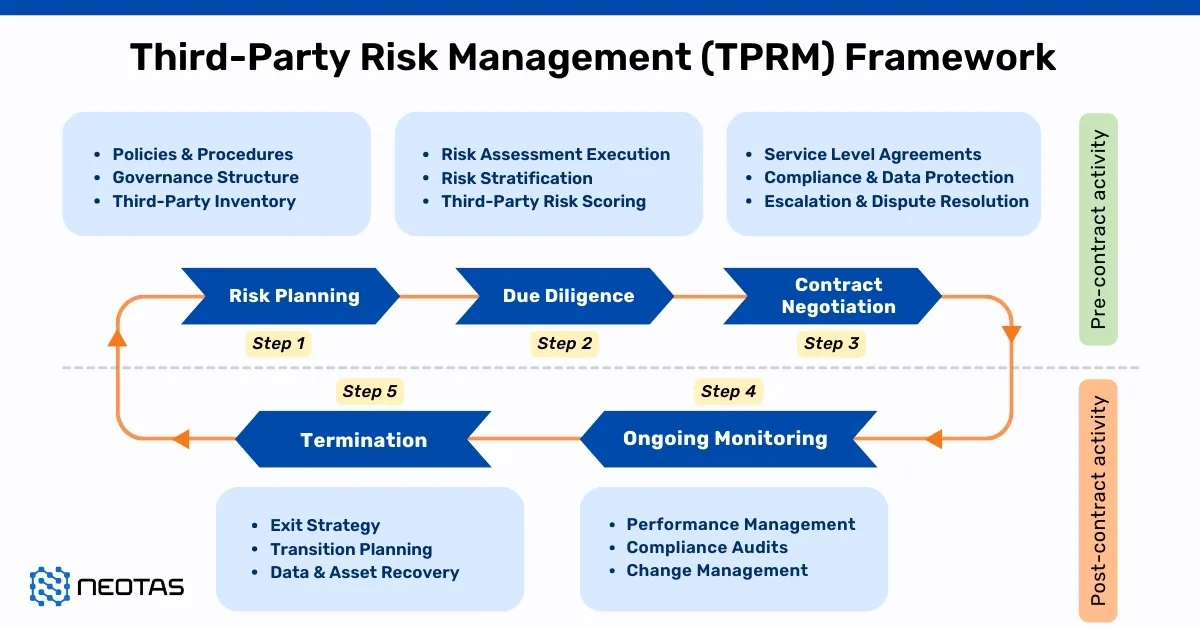
The most effective third party risk management programs share a few structural elements. They classify vendors by risk tier rather than treating all vendors equally. They perform due diligence proportionate to that risk tier. They maintain ongoing monitoring rather than doing assessments once a year and then forgetting about the relationship until renewal. They have clear escalation paths when a vendor issue emerges. And they can demonstrate to an auditor that their decisions are consistent and traceable. The tiered approach is where most programs fail. A common mistake is using vendor spend as the primary risk classifier. A vendor costing $50,000 annually might handle access management for your entire corporate network. Another vendor costing $2 million might supply office furniture. Spend-based classification would rank the furniture vendor as higher risk, which is backwards. Risk classification should be based on data sensitivity, operational criticality, regulatory exposure, and substitution difficulty. The security vendor and the furniture vendor should land in very different tiers, and the volume and intensity of your oversight should reflect that difference. I encountered a specific edge case recently that illustrates how brittle these programs can be. We had a vendor that passed every assessment stage, had SOC 2 Type II certification, responded to our annual questionnaire adequately, and was classified as medium risk. Six months into the contract, they acquired another company and started routing a subset of our data through the acquired company's infrastructure in a different jurisdiction. Our existing monitoring process had zero visibility into this change. The workaround was implementing contractual notice provisions that require vendors to alert us within a specified timeframe of any material change to their service delivery model, combined with periodic review of their public filings and security certificates to catch changes they might not proactively report. Even with these controls, there's a gap between what a vendor discloses and what actually happens operationally. No current framework closes that gap completely.
Another counter-intuitive point: continuous monitoring technologies that promise automated third party risk assessment tend to over-index on signals that are easy to measure and under-index on signals that matter more. A vendor changing its SOC 2 report is a measurable signal. A vendor's engineering team turnover rate is a meaningful risk indicator but rarely captured in any monitoring system. Budget your program design around this limitation. Automated tools should handle routine checks. Human judgment should handle the contextual analysis that the tools can't provide.
Contractual Requirements That Matter
Your contracts with critical vendors need specific provisions, not just a standard data processing agreement. Regulators increasingly expect to see audit rights that let you verify the vendor's compliance claims directly, not just rely on their self-assessments or third-party certificates. You need notification provisions that specify timeframes for breach disclosure that align with your regulatory obligations, not just whatever the vendor's default template says. Exit and transition provisions are now a regular part of regulatory expectations under frameworks like DORA, and most standard contracts don't address this adequately. The most commonly overlooked provision is the right to require corrective action with defined timelines. If an audit or monitoring activity reveals a deficiency, you need contractual authority to mandate remediation within an agreed period. Without this, you're relying on the vendor's willingness to cooperate, which is exactly the kind of dependency that regulatory findings target. I've seen vendors who had solid security postures degrade over time because there was no contractual mechanism to require them to maintain it. The absence of corrective action provisions in the contract made it impossible to escalate internally or demonstrate to regulators that the organization had enforceable controls.

What Still Doesn't Work Well
Third party risk management as a discipline has real limitations that no amount of process maturity eliminates. Vendor cooperation varies wildly. Some vendors will fill out your entire assessment thoroughly. Others will return a one-page response and claim they can't provide more detail due to confidentiality. There's no universal solution for this. The best approach is tiered: critical vendors get comprehensive assessments with potential on-site audits. Lower-tier vendors get streamlined questionnaires. But even the streamlined approach fails when a vendor refuses to engage, because the regulatory expectation is usually that you've assessed the risk, not that the vendor cooperated willingly. Another hard limitation is the lag between assessment and reality. A SOC 2 report is a snapshot. Your annual assessment is a snapshot. Vendors change configurations, personnel, and security practices constantly. No assessment frequency closes this gap entirely. The industry standard of annual reassessment for most vendors is adequate for medium-risk relationships but insufficient for high-risk ones. Several financial institutions under DORA are moving toward quarterly or continuous assessment for critical ICT providers, though the cost implication is significant. If your organization is small and your third-party exposure is limited, building a full program matching enterprise-scale requirements is inefficient. In those cases, mapping your existing practices against the relevant regulatory framework and filling gaps selectively is more practical than adopting an elaborate process you can't sustain. The regulators generally recognize that proportionality matters, even if the written guidance doesn't always emphasize it clearly.
Getting Started Without Overcomplicating It
Start with an inventory. You can't manage risk from third parties you haven't identified. This sounds obvious but many organizations discover during an assessment that they have shadow IT relationships, departmental contracts, and legacy vendor arrangements that no one centrally tracks. Build that inventory first. Then classify each vendor by risk tier using objective criteria. Then apply assessment depth proportionate to that tier. Then establish monitoring cadences that match the classification. Then ensure your contracts include the provisions I mentioned above. The sequence matters because skipping ahead to assessment tools without an inventory produces false confidence. The regulatory environment will keep tightening. More jurisdictions are adding third-party oversight requirements, and existing frameworks are expanding their scope. The organizations that handle this well aren't the ones with the most expensive tools. They're the ones with clear processes, proportionate risk classification, and the ability to explain their decisions to an auditor in a way that demonstrates consistent judgment rather than arbitrary checkboxes.