What USDA Security Awareness Training Actually Looks Like When You're Doing It
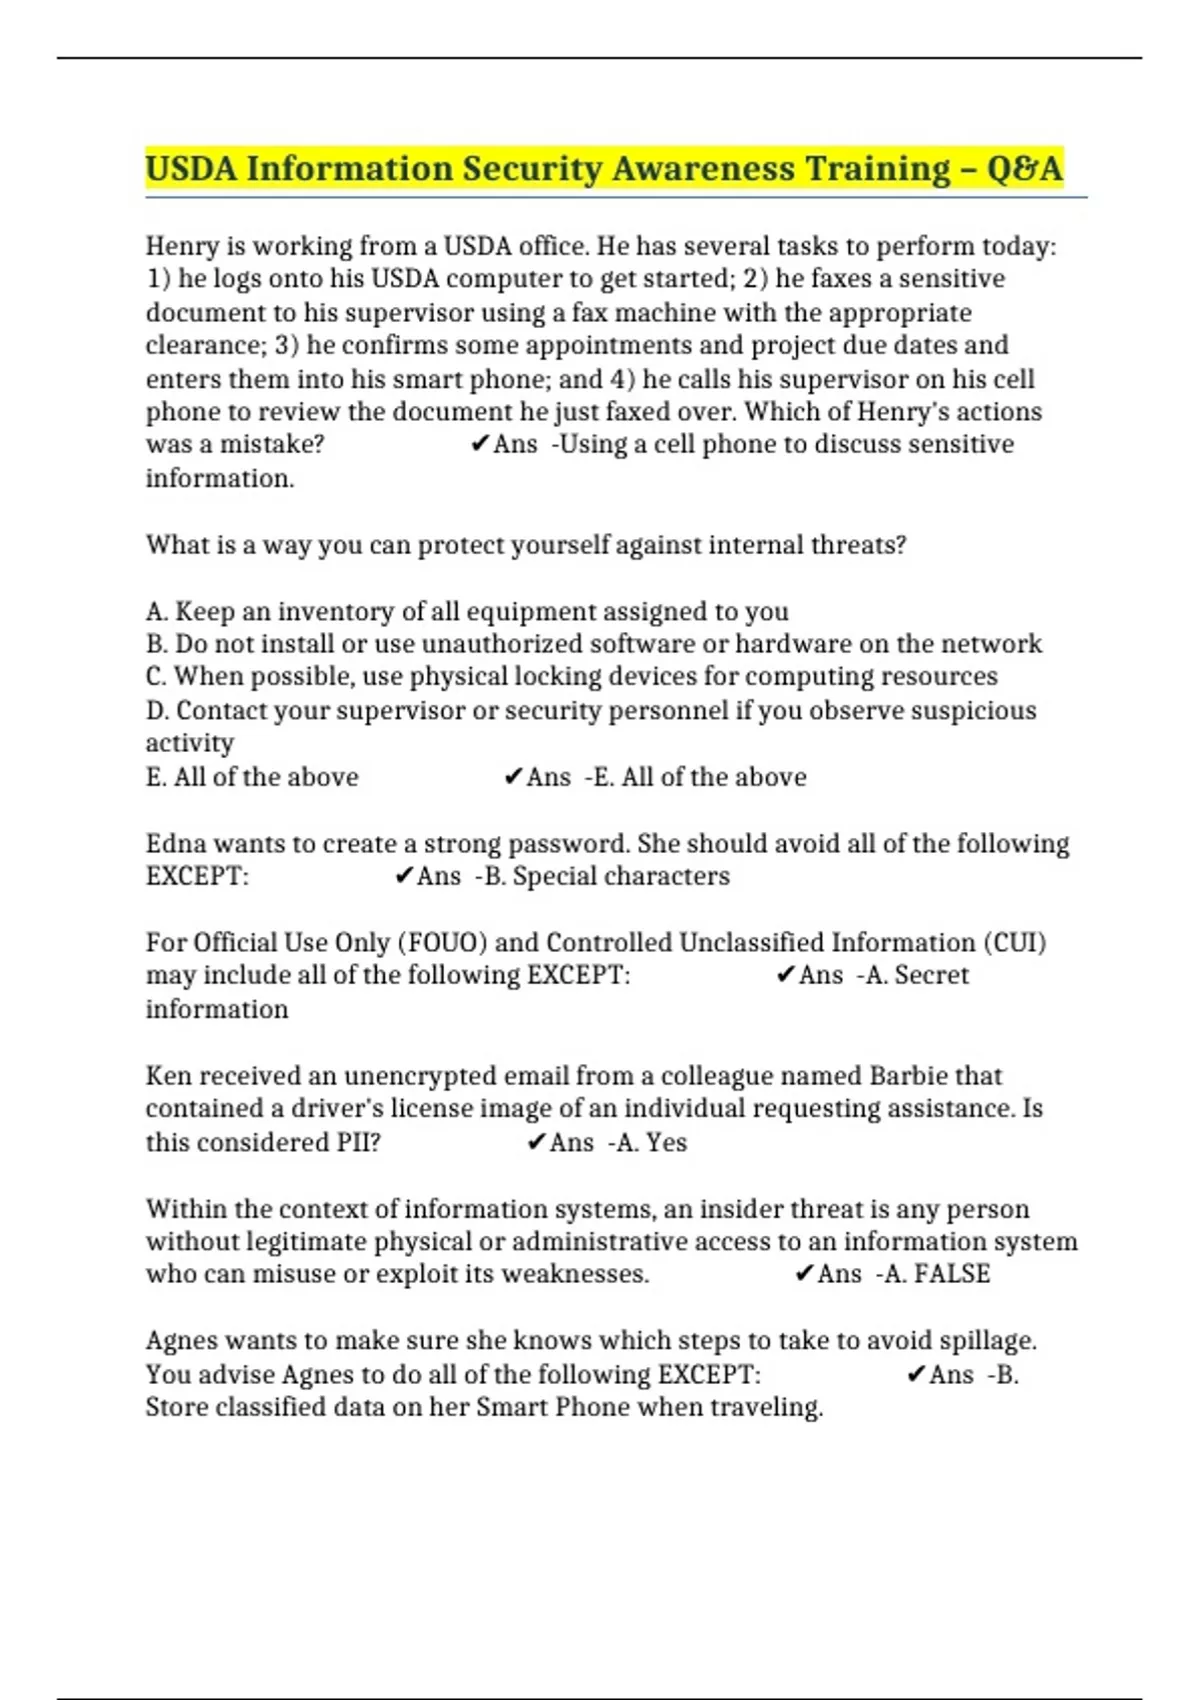
If you work for the USDA or a contractor processing their data, you've gotten the email. It lands in your inbox with a subject line like "Action Required: 2025 Security Awareness Training." There's a link. There's a deadline. There's not much else. The training itself runs about 45 to 60 minutes depending on your role and whether you need any supplemental modules. It covers phishing recognition, password requirements, incident reporting procedures, handling of Controlled Unclassified Information, and the basics of acceptable use for government systems. You click through slides, answer a few quiz questions at the end of each section, and hit submit. That's the surface version. What they don't always tell you is that the USDA LMS (the OneUSDA Learning platform) tracks completion against your PSID or contractor badge number, and if you fall behind it auto-notifies your supervisor. The first email is polite. The fifth is less so. You've probably already seen that. But here's the thing nobody warns you about: the training modules rotate, sometimes without announcement. I went through my annual refresher last year and the phishing module had been completely rebuilt from the ground up. The old one had straightforward examples. The new one used realistic internal screenshots of USDA webmail and even a mocked-up IT helpdesk ticket. Some of my colleagues failed the first attempt because they were still thinking in terms of the old content. I retook mine on the second try after reviewing the actual examples from the module carefully. The takeaway is that the material is more dynamic than "click through and forget."
Usda Security Awareness Training: How It Actually Gets Assigned
The USDA distributes training through two main pathways. Federal employees get assigned courses through the OneUSDA Learning LMS. Contractors and grantees go through a parallel system, typically the USDA's contractor training portal, which pulls from the same course library but enforces completion separately. Both feed into the agency's FISMA compliance reporting. If you're a subcontractor working under a prime USDA contract, your prime contractor is responsible for ensuring your training completion makes it into their tracking, but the USDA can and does audit that directly. You need to understand that the training isn't one-size-fits-all. There are role-based variants. An analyst handling procurement data will get different scenario modules than someone in research handling agricultural survey data. Both cover the same core concepts, but the examples diverge. The LMS tries to auto-assign the right track based on your role in the system, but I've watched new hires get placed in the wrong track because their HR record hasn't been fully synced yet. If your training dashboard shows a module that looks irrelevant to your actual job, flag it to your agency's security team before wasting hours on it.
The Modules and What They Actually Test
Breaking this down by section, you're looking at roughly these core areas: Phishing and Social Engineering: This is the heaviest module. It covers email-based threats, spear phishing, USB device risks, and phone-based social engineering. The quiz at the end will show you real-looking emails and ask you to identify red flags. The counter-intuitive part most people miss is that the newer versions focus less on obvious spam indicators and more on subtle cues. A legitimate-looking sender address with a minor typo in the subdomain. An email from someone you actually work with whose account was compromised. The quiz will test whether you recognized those. Password and Authentication: Password requirements for USDA systems follow NIST 800-63B guidelines now. The module explains why long passphrases are preferred over complex short passwords, why you shouldn't reuse credentials across government and non-government systems, and how multi-factor authentication works with USDA smart cards and CAC/PIV cards. Common pitfall: people skim through this section because they think they already know it. But the quiz sometimes asks specific questions about USDA's current MFA exceptions or how to report a lost PIV card. Those details aren't common knowledge.
Get the Full Details
Incident Reporting: This section is shorter but the quiz weight is misleadingly high. You need to know the exact process for reporting a suspected breach at the USDA. That means knowing your agency's Security Operations Center contact information and understanding the difference between a reportable event and something you just document. I remember a colleague who didn't report a clicked-link incident because the training hadn't clearly explained what threshold constituted a mandatory report. He found out the hard way during an audit. The reporting window is typically within one hour of detection for confirmed or suspected incidents. Data Handling and Classification: How to treat CUI, where CUI can and cannot be stored, transmission requirements, and the basics of FISMA moderate versus high impact systems. This is where the role-based divergence really shows. Procurement folks get examples about vendor data. Researchers get examples about agricultural datasets. The underlying rules are the same but the scenarios matter for the quiz.
Tracking, Compliance, and What Happens When You Fall Behind
Completion isn't just a checkbox. USDA's Office of the Chief Information Officer (OCIO) publishes compliance metrics quarterly to OMB and GAO. Your individual completion status feeds into those numbers. If your compliance number drops below the agency target (usually 95% within 30 days of hire and annually thereafter), it becomes a management issue. The OCIO sends escalation notices to agency component heads. At that point, your training isn't just an HR task anymore. It's a line item in a briefing. Here's the practical side most people don't understand: annual refresher and initial training have different deadlines. New hires get 30 days from start date for initial training. Existing staff get the annual refresher on a rolling schedule tied to their hire or last-completion date. Some components try to batch everyone into the same week for convenience. That creates bottlenecks in the LMS. If your component does that and the system stalls, don't wait. Contact the USDA ITS service desk and document your attempt to complete it. You'll need that paper trail if the deadline passes before the system recovers.
Common Problems and What Actually Works
The most frequent issue I've seen is the LMS session timeout. The training platform will log you out after about 20 minutes of inactivity. If you're on a long module and step away for coffee, you lose your progress on that particular session. The workaround is simple but people ignore it: save your progress frequently by clicking the "save and continue later" button between sections instead of waiting until the end. I've also seen people get stuck in a loop where the LMS marks a module as incomplete even after they passed the quiz. That's usually a browser cache issue or an outdated session cookie. Clear the cache, use a different browser, or try incognito mode. If it still fails, escalate to your component's training coordinator rather than repeatedly clicking through. There's a backend manual override they can apply. Another edge case that bites people: the training certificate. The LMS generates a completion certificate automatically, but it only appears in your transcript after all required modules are marked complete. If you have a supplemental module outstanding, your transcript will show partial completion and no certificate. Don't assume you're done because you passed the main quiz. Check your transcript explicitly. I once had a contractor finish every module except a 15-minute CUI add-on and then waste two weeks thinking everything was cleared because the main training completed fine. The certificate never appeared until the add-on was finished.
Limitations Worth Being Honest About
The training itself is functional but it has real gaps. It's designed for broad compliance coverage, not deep technical skill building. Completing the annual refresher will not make you a phishing analyst. It will make you aware of phishing, which is the goal but also the limit. Some components supplement the mandatory training with tabletop exercises or simulated phishing campaigns, but that's not universal. If you're in a component that doesn't do that, your practical security awareness may plateau at whatever level the slides can take it. There's also a tracking gap between the LMS and actual security monitoring. Passing the quiz doesn't mean your organization won't send you a simulated phishing email next week. The training completion rate and the organizational phishing click rate are reported separately and don't necessarily correlate. I've seen components with 99% training completion and a 12% simulated phishing failure rate. That disconnect is worth understanding. The training checks a compliance box. Your daily habits determine actual risk. If you're a contractor, one more thing: your training records belong to your employer's compliance file, not yours. You can request a copy of your completion certificate through the LMS transcript, but you won't get a detailed breakdown of your scores or module performance unless your contractor security officer provides it. Plan around that if you need documentation for another agency or auditor.