Why This Book Actually Matters
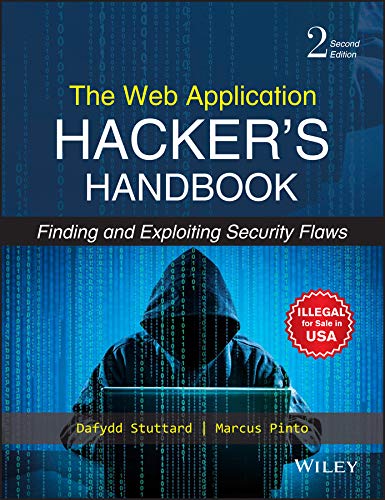
Most people who come into web application security start by running Burp Suite through a list of automated payloads and then stop. That gets you so far. The gap between someone who can click buttons in a scanner and someone who actually understands why a vulnerability exists is usually measured in books, not certifications. The Web Application Hackers Handbook is one of those books. It is not the flashiest read, but it has stayed relevant longer than most because it was written by people who actually break things for a living. The full title is The Web Application Hackers Handbook: Discovering and Exploiting Security Flaws. It was originally published in 2011, and the second edition came out around 2016. The core content covers the same ground it always has: how web applications talk to each other, where those conversations go wrong, and how to prove it. The techniques don't expire the way some tool-based guides do, because HTTP and state management are still the same protocols. What changes is the surface area and the defenses. I remember going through my first serious engagement after reading the chapter on buffer overflows in the browser. The theory was straightforward enough, but the real test came when I hit a legacy PHP application that accepted file uploads without proper extension filtering. The automated scanner flagged it as a low-severity issue. I followed the methodology from the handbook and found that the server was running an old version of ImageMagick with a known Policy.xml restriction. The scanner didn't understand that context. I spent about forty-five minutes crafting a malicious image file that triggered the convert binary through a side-channel exploit. That engagement was the moment I stopped treating vulnerability scanning as analysis and started treating it as a starting point.
What the Book Actually Teaches
The handbook is organized around the anatomy of a web application, not around specific tools. It starts with how the internet works at the HTTP level, moves into architecture patterns, then dives into each class of vulnerability with exploitation methodology. The structure mirrors how an actual assessment should flow. You enumerate the surface, you understand the architecture, you identify the flaws, and you demonstrate impact. Most training skips straight to injection and call it a day. One thing beginners consistently miss is the emphasis on mapping. The book spends real time on understanding what the application is trying to do before it tries to break it. There is a chapter on proxy configuration and session handling that seems basic until you are six hours into a test and realize you have been authenticated as the wrong user the entire time because you did not understand how the SSO token was being passed. I have seen engagements where the tester reported cross-site scripting but missed a privilege escalation path that was only visible once the session flow was properly mapped. The difference between those two outcomes is usually whether someone followed the mapping methodology in the book or rushed into exploitation.
Core Methodology Breakdown
The central approach the book teaches is what it calls the hacker methodology, and it is really just a structured way of thinking about an application. It breaks down into five stages that map closely to how any real assessment should proceed. First is information gathering. This means collecting everything publicly available about the application before you touch it. Who built it, what framework, what hosting environment, what technology stack. This is not recon for recon's sake. It tells you where the likely weak points are before you start sending requests. A Django application has different defaults than a Laravel application. A .NET app running on IIS handles authentication differently than a Node.js service on nginx. Knowing this upfront cuts your testing time significantly because you stop guessing and start targeting. Second is application architecture identification. You need to understand the flow of data through the system. Where does input come from? Where does it go? What components process it? How does the application talk to the backend? This step separates the people who shoot random payloads at forms from the people who understand why those payloads might or might not work. I tested an application once where the input validation was completely opaque because the front end was a single-page React application and the back end was a microservice mesh. The handbook's guidance on mapping the application's behavior helped me identify that one of the internal services was accepting requests directly from the public internet through an API gateway that had no rate limiting.
Get the Full Details

Third is configuration and deployment management testing. This is the step most people skip because it is not glamorous. Checking default credentials, exposed administration interfaces, backup files, version control leaks, and misconfigured servers. These issues are boring to find but devastating when they exist. I once spent about ten minutes checking a staging environment and found that the production database credentials were hardcoded in a JavaScript file that had been accidentally deployed. That gave me direct database access without needing to exploit a single application-level vulnerability. Fourth is threat modeling. You take everything you have learned about the application and you build a model of what an attacker would actually try. This involves identifying the assets, the entry points, and the likely attack vectors. The book provides a framework for this rather than a checklist. A checklist approach leads you to test the same twenty vulnerabilities on every application regardless of context. The framework approach makes you think about what matters for that specific application. A file upload feature on a document management system deserves more attention than the same feature on an internal forum. Fifth is vulnerability analysis and exploitation. This is where the bulk of the book lives. It covers injection flaws, authentication issues, access control problems, session management weaknesses, business logic flaws, and client-side attacks. Each section follows a consistent pattern: what the flaw is, how it manifests, how to detect it, how to exploit it, and how to mitigate it. The detection and exploitation sections are where the practical value is. They include specific payloads, request examples, and tools you can use.
What the Book Gets Wrong or Leaves Out
I want to be blunt about the limitations because the book does not do this well itself. It was published in 2016, and the web application landscape has moved significantly since then. Modern applications use OAuth 2.0 and OpenID Connect extensively, and while the book touches on authentication, it does not cover the protocol-level attacks that have become common. JWT manipulation, token binding failures, and OAuth misconfigurations are now among the most impactful vulnerabilities in web applications, and they are barely addressed. API security has also evolved. The book focuses heavily on traditional browser-based applications. REST APIs, GraphQL endpoints, and mobile backends operate on similar principles but have different attack surfaces. GraphQL in particular introduces query complexity attacks and introspection exposure that the book does not cover. If you are testing a modern API-first application, you will need to supplement the handbook with current resources on API security. Another gap is the rise of client-side frameworks. The book discusses cross-site scripting in the context of traditional server-rendered pages. Single-page applications change the delivery mechanism of scripts and the timing of execution. While the underlying vulnerability classes remain the same, the detection and exploitation methods require adaptation. Content Security Policy misconfigurations, for example, interact differently with SPAs than with classic applications.
The most honest thing I can say about this book is that it is a foundation, not a complete reference for contemporary web application security. It will teach you how to think like an attacker and give you the vocabulary to describe what you find. It will not keep you current on its own. You need to pair it with ongoing research and hands-on practice.

How to Actually Use This Book
Reading it cover to cover is not the most efficient approach. I recommend starting with the methodology chapters if you are new to this, because they frame everything that follows. Then pick a vulnerability class that you are least comfortable with and work through that section carefully. The exploitation examples are not trivial, and you need to practice them in a controlled environment before you attempt them on anything real. Set up a local lab. DVWA, WebGoat, or PortSwigger's Web Security Academy are all viable options. The PortSwigger labs in particular are free and cover the exact vulnerability classes the book discusses. Work through each one while referencing the relevant section of the handbook. Take notes on the detection technique, the payload, and the confirmation method. After about three weeks of daily practice, you will find that the manual testing approach the book teaches becomes faster and more reliable than most automated tools for certain vulnerability types. When you move to real engagements, use the book as a reference guide, not a script. The scenarios you encounter will not match the examples exactly. I tested an e-commerce platform once where the checkout flow used a JSON Web Token to pass order state between the front end and back end. The token was not cryptographically signed, which the book would classify under broken authentication, but the specific exploitation vector involved manipulating the token claims to change the product quantity from one to negative values. The scanner reported the unsigned token as informational. The actual financial impact required understanding the business logic around quantity validation, which the book covers in the business logic flaws section.
The book also includes appendices with tools and techniques. The Burp Suite appendix is useful but dated in its specifics. The proxy configuration guidance is still accurate. The certificate management section is worth reading if you plan to do SSL/TLS testing. The exploit development appendix is relevant for the rare cases where you encounter buffer overflows in web application contexts, though those are increasingly uncommon in modern stacks.
Where to Get It
The book is available through major retailers and the publisher's website. The second edition is published by Wiley. There is no official free version, and I do not recommend piracy for this one because the content is technical enough that you need the exercises and the precise terminology. Use the physical copy or an eBook that supports annotation. The value increases dramatically when you can mark up the pages during practice. After you finish the book, the natural next step is hands-on bug bounty work or a professional penetration testing engagement. The methodology will hold up, but you will discover quickly that real applications do not follow the clean examples in the text. That is where the experience compounds. The book gives you the map. Walking the terrain is what makes you competent.