Breaking Numbers Down Without Losing Your Mind
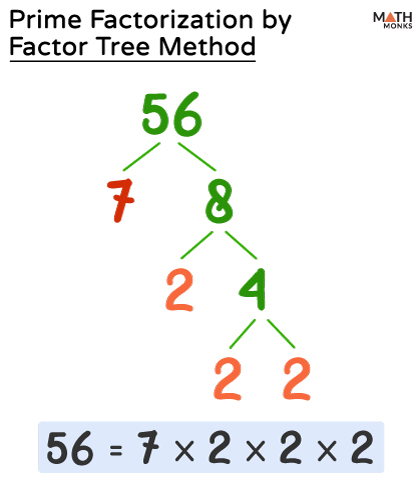
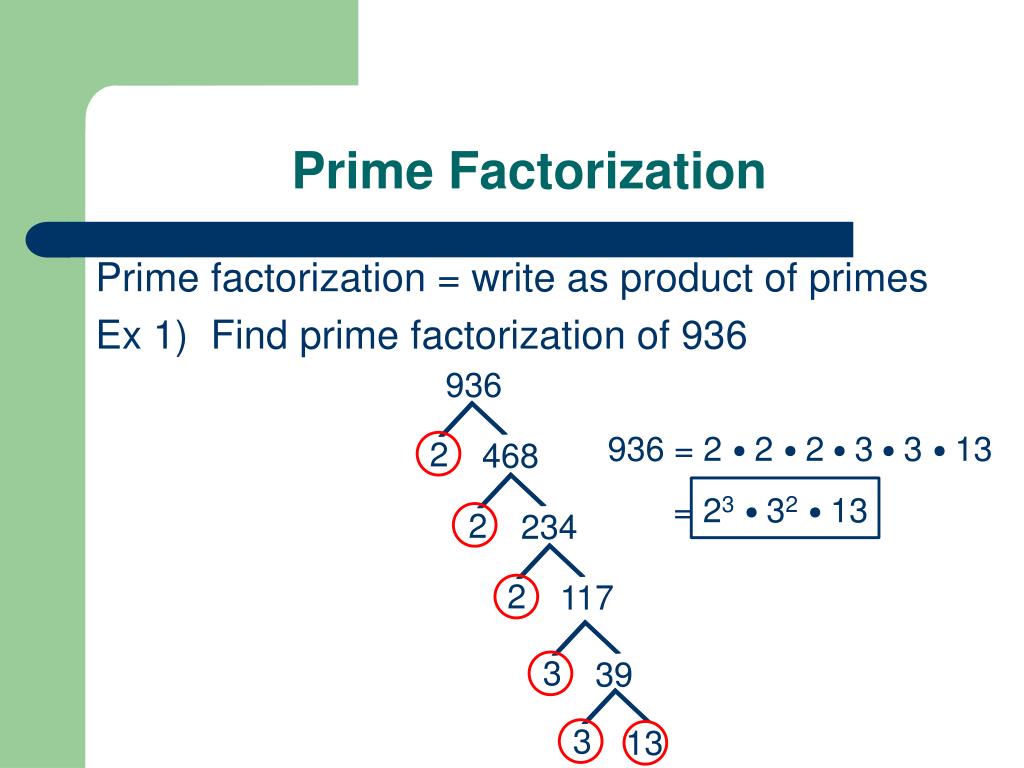
Prime factorization is just breaking a number into the prime numbers that multiply together to make it. That's it. When someone asks what is the prime factorization of something, they want to know which primes you'd multiply to reconstruct that original number. Take 60 for example. You'd get 2 × 2 × 3 × 5. Every composite number has exactly one unique set of prime factors, and that uniqueness is the whole reason this concept matters in practice. I used to do this by hand for client work back when I was smaller and cheaper. These days I just write a quick script, but the method itself hasn't changed in three thousand years. Start with the smallest prime, which is 2, and see if it divides evenly. If it does, write it down and divide again. Keep going until it doesn't divide anymore, then move to the next prime, which is 3, then 5, then 7, and so on.
What Is The Prime Factorization and Why Should You Care
Most people learn this in middle school and immediately forget it because nobody told them when they'd actually need it. In cryptography, prime factorization is the thing keeping your online banking from being trivially breakable. Large numbers that are products of two huge primes are easy to multiply but absurdly hard to factor back apart. That asymmetry is literally the foundation of RSA encryption. When you do SSL/TLS, you're trusting that factoring a 2048-bit number would take longer than the current age of the universe with classical computers. The practical side is different though. If you're working with smaller numbers, like under a million, trial division is fine. I've factored numbers up to around 10^9 by hand in a pinch using a systematic approach. You write down the primes in order: 2, 3, 5, 7, 11, 13, 17, 19, 23, 29, 31. Test each one. Most numbers will collapse quickly because they have small prime factors. The annoying ones are products of two primes that are close to each other and both fairly large. Here's a specific problem I ran into recently that nobody warns you about. I was cleaning up some numerical data for a project and encountered the number 999999937. It looked completely normal, so I fed it into a basic trial division script running up to the square root, which is roughly 31622. The script ran for about forty seconds and returned nothing. That number is actually prime. A naive implementation might waste time checking all the way to the square root when it could stop early if it found a factor. My workaround was to add a probabilistic primality test like Miller-Rabin before attempting factorization. If it passes as probably prime, you skip the expensive trial division entirely. Cuts wasted computation by orders of magnitude on inputs like that.
The Method Without the Fluff
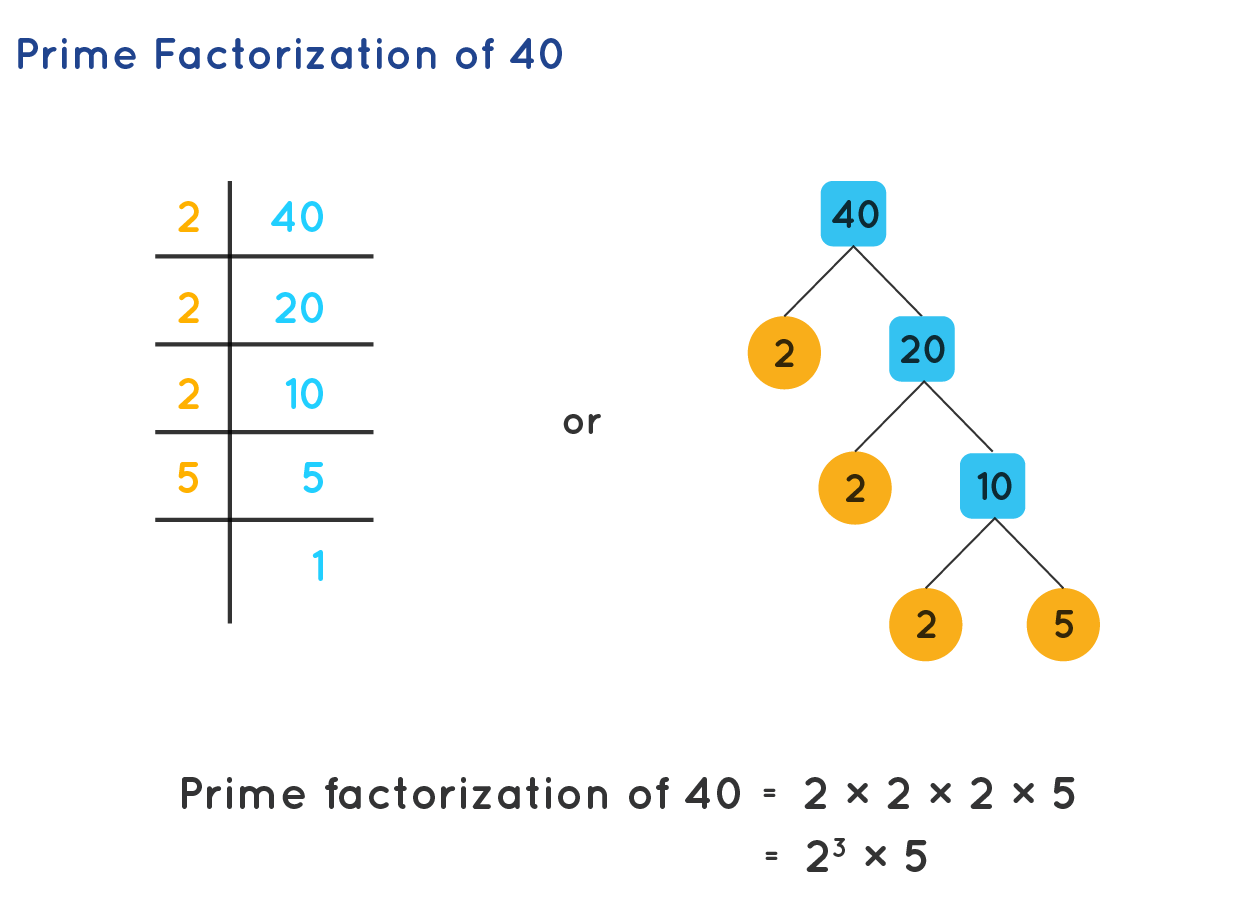
Write the number at the top of a T-chart. Left column is the divisor, right column is the quotient. Divide by 2 as many times as possible, writing each 2 on the left and the new quotient on the right. Move to 3, then 5, then 7. Stop when the quotient on the right becomes 1. The left column is your prime factorization. For 840, the process looks like this. Divide by 2 three times to get 105. Divide by 3 once to get 35. Divide by 5 once to get 7. That final 7 is prime, so it goes on the left too. The answer is 2³ × 3 × 5 × 7. Simple, mechanical, and it works every time for reasonable numbers. The edge cases are where people trip up. Zero has no prime factorization and trying to factor it breaks everything. One also has no prime factorization by convention, which annoys people who expect it to be trivial. Negative numbers get a -1 factor and then the absolute value gets factored normally, but most implementations just don't handle negatives at all. And if you're factoring in modular arithmetic, like in a finite field, prime factorization doesn't apply the same way and you need different tools entirely.
Get the Full Details
Pitfalls That Will Waste Your Time
The biggest mistake beginners make is stopping the trial division too early. You have to check divisors all the way up to the square root of the current quotient, not just the square root of the original number. As the quotient shrinks, so does the search space, which is why this is efficient, but you still need to recompute the bound each time. I've seen scripts that compute sqrt(n) once at the top and never update it, which causes wrong results when the quotient drops significantly. Another trap is assuming you need to check every odd number after 2. You don't. You only check primes. But generating primes on the fly is more expensive than just trying 3, 5, 7, 9, 11 and accepting that 9 won't divide anything that 3 already took care of. The redundancy is minimal and the code is simpler. Wheel factorization and precomputed prime tables help for bulk operations but add complexity that most projects don't need. Fermat's factorization method is worth knowing about but misunderstood. It works by expressing n as a difference of two squares: n = a² - b² = (a+b)(a-b). This is efficient when the two prime factors are close together, like if you're factoring a semiprime where the primes are within a few percent of each other. It fails badly when the factors are far apart because you're essentially doing a brute force search for a and b. I spent a frustrating afternoon on a challenge problem where the answer required Fermat's method because the factors were 100003 and 100019, nearly identical. A trial division script would have run for hours while Fermat's method finished in milliseconds. But then I hit another problem where the factors were 2 and a large prime near 500 million, and trial division won by a mile while Fermat's method was completely impractical. The lesson is that no single algorithm dominates across all inputs.
For really large numbers, there are better methods. The quadratic sieve handles numbers up to around 100 digits and is the practical choice for most cryptographic applications. The general number field sieve is asymptotically faster for numbers above 100 digits and is what's actually used in real factoring records. But for anything under 10^12, trial division with good optimizations or Pollard's rho algorithm is sufficient and dramatically simpler to implement.
When It Just Doesn't Work
Prime factorization becomes intractable at scale, and that's not going to change unless someone discovers a classical polynomial-time algorithm, which would break most of modern cryptography. Even with quantum computing and Shor's algorithm, factoring a 2048-bit RSA modulus requires millions of error-corrected qubits, which we don't have and may not have for a long time. So if you're building something that depends on factorization being easy, you're building on sand. Use it for teaching, for small-scale computation, and for understanding number theory, but don't rely on it as a security primitive for anything bigger than a toy problem. If you need to generate large primes for key generation, don't factor random numbers. Use established primality tests like Miller-Rabin with sufficient rounds, then multiply the primes yourself. Generating a 2048-bit RSA key takes maybe a second on modern hardware with proper libraries. Trying to factor a random 2048-bit number would not finish before the heat death of the universe even with a supercomputer. There's also the issue of perfect powers. Numbers like 2^100 or 3^50 are trivially factorable if you recognize the base, but a generic trial division algorithm wastes time because it doesn't know to look for repeated factors. A simple GCD-based check against small primes can detect this. Check if gcd(n, p#) is greater than 1 where pis the primorial, or just run a small-prime sieve first and strip out all small factors before moving to heavier methods.
A Practical Shortcut
If you're writing code and need a quick factorization routine, here's what I use. Strip factors of 2 first, then iterate odd numbers from 3 to sqrt(n), dividing whenever possible. If anything remains after that, it's prime. For the occasional large stubborn case, add Pollard's rho with Brent's improvement. That combination handles everything up to about 10^14 in reasonable time and is short enough to implement in an hour. I keep a copy of this in my personal utility library. Last month I needed to factor a few thousand integers in the range of 10^10 to 10^12 for a data analysis task. The trial division part handled maybe 90 percent of them in under a millisecond each. Pollard's rho picked up most of the rest. Only three numbers resisted and those were products of two primes around 10^6 each, which I just brute-forced with a precomputed sieve since the total count was so small. The whole batch finished in about twenty seconds on a laptop. The takeaway is that prime factorization is straightforward in principle and manageable in practice up to a point. Beyond that point, it's a research problem, not a homework problem. Know your input size, pick the right algorithm, and don't pretend that brute force will scale to anything that matters in the real world.