Getting WPA Working on a Windows 7 Machine
The Windows SDK that ships Windows Performance Analyzer is still the most reliable way to profile system performance on Windows 7. It isn't pretty, but it works better than most alternatives when you need kernel-level data. The install pulls in a handful of tools: WPA itself, Logman, Xperf, and the trace commands that actually drive the collection side of things. You can grab it from the Microsoft Download Center by searching for the Windows SDK for Windows 7 and .NET Framework 4. This is the last SDK version that includes WPA as a standalone installation package. Later SDKs moved toward ETW-centric tools and restructured the install, so going back to the Windows 7 SDK keeps things simpler for legacy systems. The download is roughly 3 GB. It took about 40 minutes on my machine with a solid SATA connection, and another 15 to 20 minutes for the install to finish.
Installing and Setting Up Windows Performance Analyzer Windows 7
Run the installer as Administrator. During setup, choose the full installation path rather than the default Program Files location if your drive has limited space. The SDK folders expand aggressively, and I usually hit the 4 GB mark in the target directory. After installation completes, navigate to C:\Program Files\Microsoft SDKs\Windows\v7.0\Samples\Systemdiagnostics\WPA. You will find Wpa.exe there alongside the supporting files. The first time you launch WPA on Windows 7, it asks you to select symbols and trace log folders. Point the symbol path to http://msdl.microsoft.com/download/symbols and create a local cache folder somewhere with at least 2 GB of free space. Symbols make or break your ability to read kernel stacks properly. Without them, you are just looking at addresses with no human-readable names. I ran into a specific issue one afternoon where WPA would import an ETL file but display a completely blank overlay view. No CPU usage, no disk activity, nothing. The profile was loaded, the columns existed, but the chart area showed zero data. What turned out to be the problem was that the Windows 7 SDK version of WPA defaults to an older schema profile when opening traces collected on newer systems. Even though the ETL came from the same machine, a registry change I had made to enable additional providers shifted the file structure just enough that WPA misread the event stream.
The workaround was straightforward but not obvious. I closed WPA entirely, opened a command prompt as Administrator, and ran xperf -i mytrace.etl -o mytrace_clean.etl. That command re-wrote the ETL file using the current system's schema, which WPA could then parse correctly. The process took about three minutes for a 500 MB trace and the resulting overlay graph populated within seconds of reimporting. This step saves a lot of frustration when you are dealing with traces that have been through driver updates or registry modifications since collection. Before collecting anything, you should create a stack trace configuration file. Open a command prompt and run: xperf -on PROC_THREAD+LOADER+PROFILE+DISKIO+FILESYSTEM -stackwalk Profile
Get the Full Details
Then start your trace with xperf -start C:\traces\base.etl. Run whatever workload you need to measure. Afterward, stop collection with xperf -stop and merge everything with xperf -merge base.etl merged.etl. The merged file is what you open in WPA. Skipping the merge step usually results in incomplete data in the overlay view, especially when multiple providers write to different ETL files simultaneously.
What Actually Shows Up and How to Read It
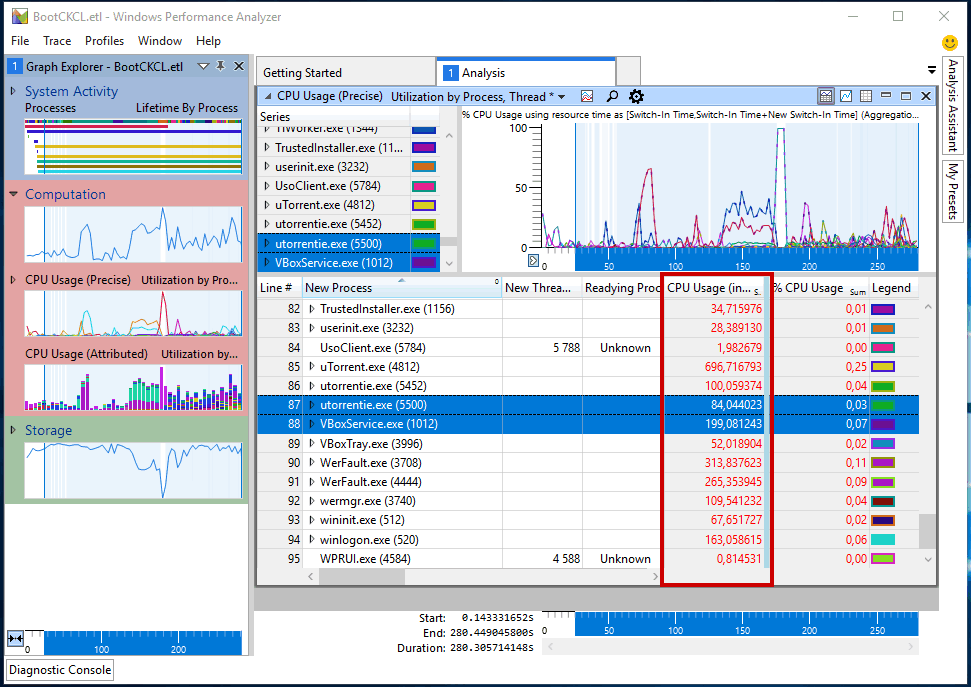
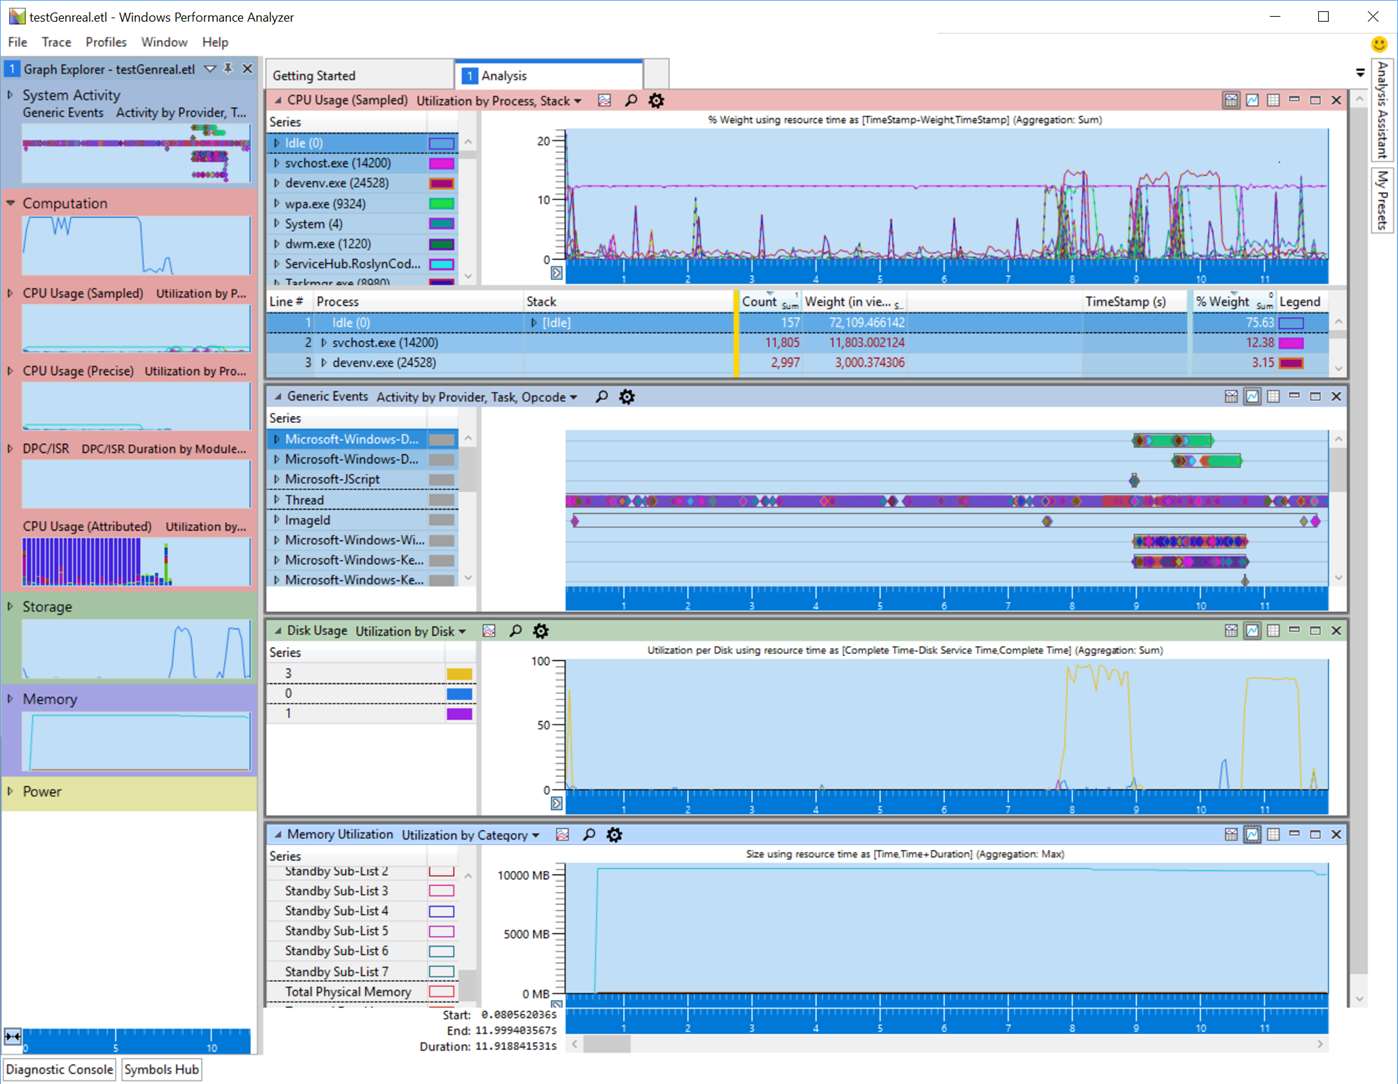
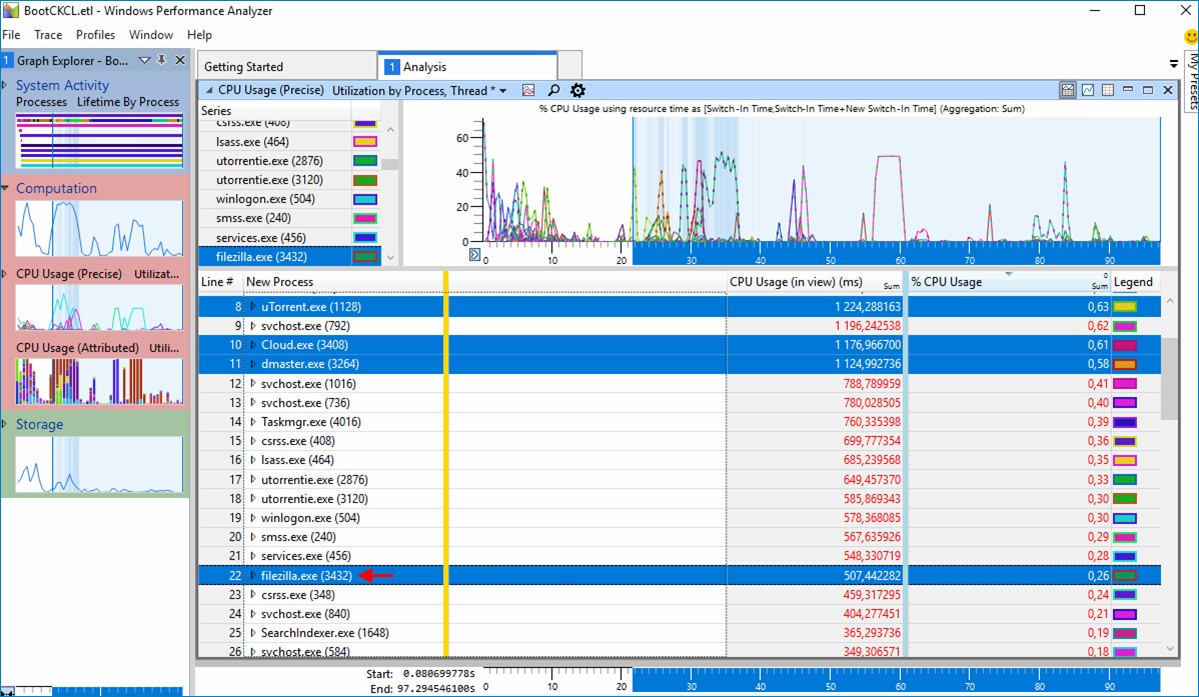
The overlay view is the most useful panel. It stacks CPU usage, disk queue length, context switches, and network I/O on the same timeline. This lets you see causality between events. A CPU spike followed immediately by a disk queue spike usually means something is spinning on I/O rather than doing real computation. The reverse pattern suggests CPU-bound work that eventually blocks waiting for data. The CPU Usage (Sampled) view uses statistical sampling at a default rate of 997 Hz. This is different from stack profiling, which captures actual call stacks at interrupt time. The sampled view is less precise but has far lower overhead. During a typical measurement run, I see overhead stay under 5 percent on a quad-core machine. Stack-based profiling can push that to 25 percent or more depending on the event rate. One thing beginners consistently miss is how WPA handles interrupted traces. If your system crashes or the ETL file is never closed properly, WPA can still open the file, but the timeline will show gaps where data was lost. The overlay view simply stops drawing at the point of interruption. There is no warning dialog. The only indicator is a hard cutoff in the data stream. I learned this the hard way during a stress test where the target machine froze due to thermal throttling. The trace file was 1.2 GB, but the last 180 seconds of data were gone. I had to correlate timestamps from a separate event log to figure out exactly when the freeze occurred.
Another common pitfall involves provider filtering. The default trace configuration captures everything from the kernel stack, including routine interrupts like timer ticks and idle loop activity. If you need to isolate a specific process, use xperf -d on -p <ProcessName> after the initial trace starts. This filters provider output at the kernel level rather than relying on post-collection filtering in WPA. The difference is significant. Post-collection filtering on a large ETL file can take 10 to 15 minutes on a typical workstation. Kernel-level filtering during collection takes zero additional time because the data is never written in the first place.
Limitations You Should Know About
WPA on Windows 7 does not support all the features present in later versions. The newer timeline search bar, the improved provider selector, and the enhanced filtering syntax simply do not exist in the Windows 7 SDK build. You are working with an older UI that lacks these conveniences. Searching through thousands of events requires manual scrolling or using the command-line tools to pre-filter before importing into WPA. The tool also struggles with very large ETL files. I have seen collection runs produce files over 5 GB when profiling applications with heavy file I/O on a system with limited RAM. WPA becomes sluggish past about 2 GB of trace data. The UI frame rate drops, zooming lags, and exporting screenshots takes noticeably longer. In those situations, splitting the trace into smaller segments during collection is more practical than trying to force WPA to handle the full file. For systems where WPA feels too limiting, the newer Windows Performance Toolkit available through the Windows 10 SDK offers better performance with larger files and a more responsive interface. However, those newer tools do not always run cleanly on Windows 7 due to missing runtime dependencies. It is a tradeoff between running on your target OS and having modern tooling features.
The real value of Windows Performance Analyzer Windows 7 comes down to understanding what your system is doing at the kernel level without guessing. The steps are straightforward, the data is reliable, and once you get past the initial setup friction, most problems become visible within a single trace session.