Why Most Risk Assessments Get Done Wrong
I've reviewed audit plans across manufacturing, finance, and healthcare orgs for about a decade now. The pattern is always the same: people treat the risk assessment as a checkbox exercise, not as the actual blueprint for where effort should go. They fill out a spreadsheet, rank things low-medium-high, and move on. Then two months later the audit team is chasing some low-risk process while a material control failure goes undetected. The tool that fixes this isn't complicated. It's an Audit Plan Risk Assessment Template, properly built. But most templates you find online are garbage. They're either too generic to be useful or so detailed they take three weeks to complete. There's a middle ground. I'll walk through it.
Using an Audit Plan Risk Assessment Template Correctly
Start with the framework, not the worksheet. You need to understand what dimensions of risk actually matter before you put anything into cells. In practice, there are five dimensions that separate a useful assessment from a decorative one: Inherent risk level — how likely is something to go wrong in this area without any controls in place? This requires actual knowledge of the business process, not a guess. Control environment strength — what controls exist, and more importantly, have they been tested recently? A control that hasn't been tested in over a year should carry more weight than one that passed its last test two weeks ago.
Financial materiality — what is the dollar impact if this area fails? This isn't just about total transaction volume. Look at variance. A high-volume, low-variance process is less risky than a lower-volume process where small errors compound quickly. Regulatory exposure — does this area touch regulated data, financial reporting standards, or compliance requirements? Even small breaches here can generate outsized consequences. Recent change velocity — has this process been modified, restructured, or staffed differently in the past twelve months? Change is the single best predictor of control breakdown. I learned this the hard way after missing a vendor management process that had been partially automated six months earlier. The old controls still existed on paper. The new ones weren't operating yet. We found it on our second visit instead of our first.
Get the Full Details
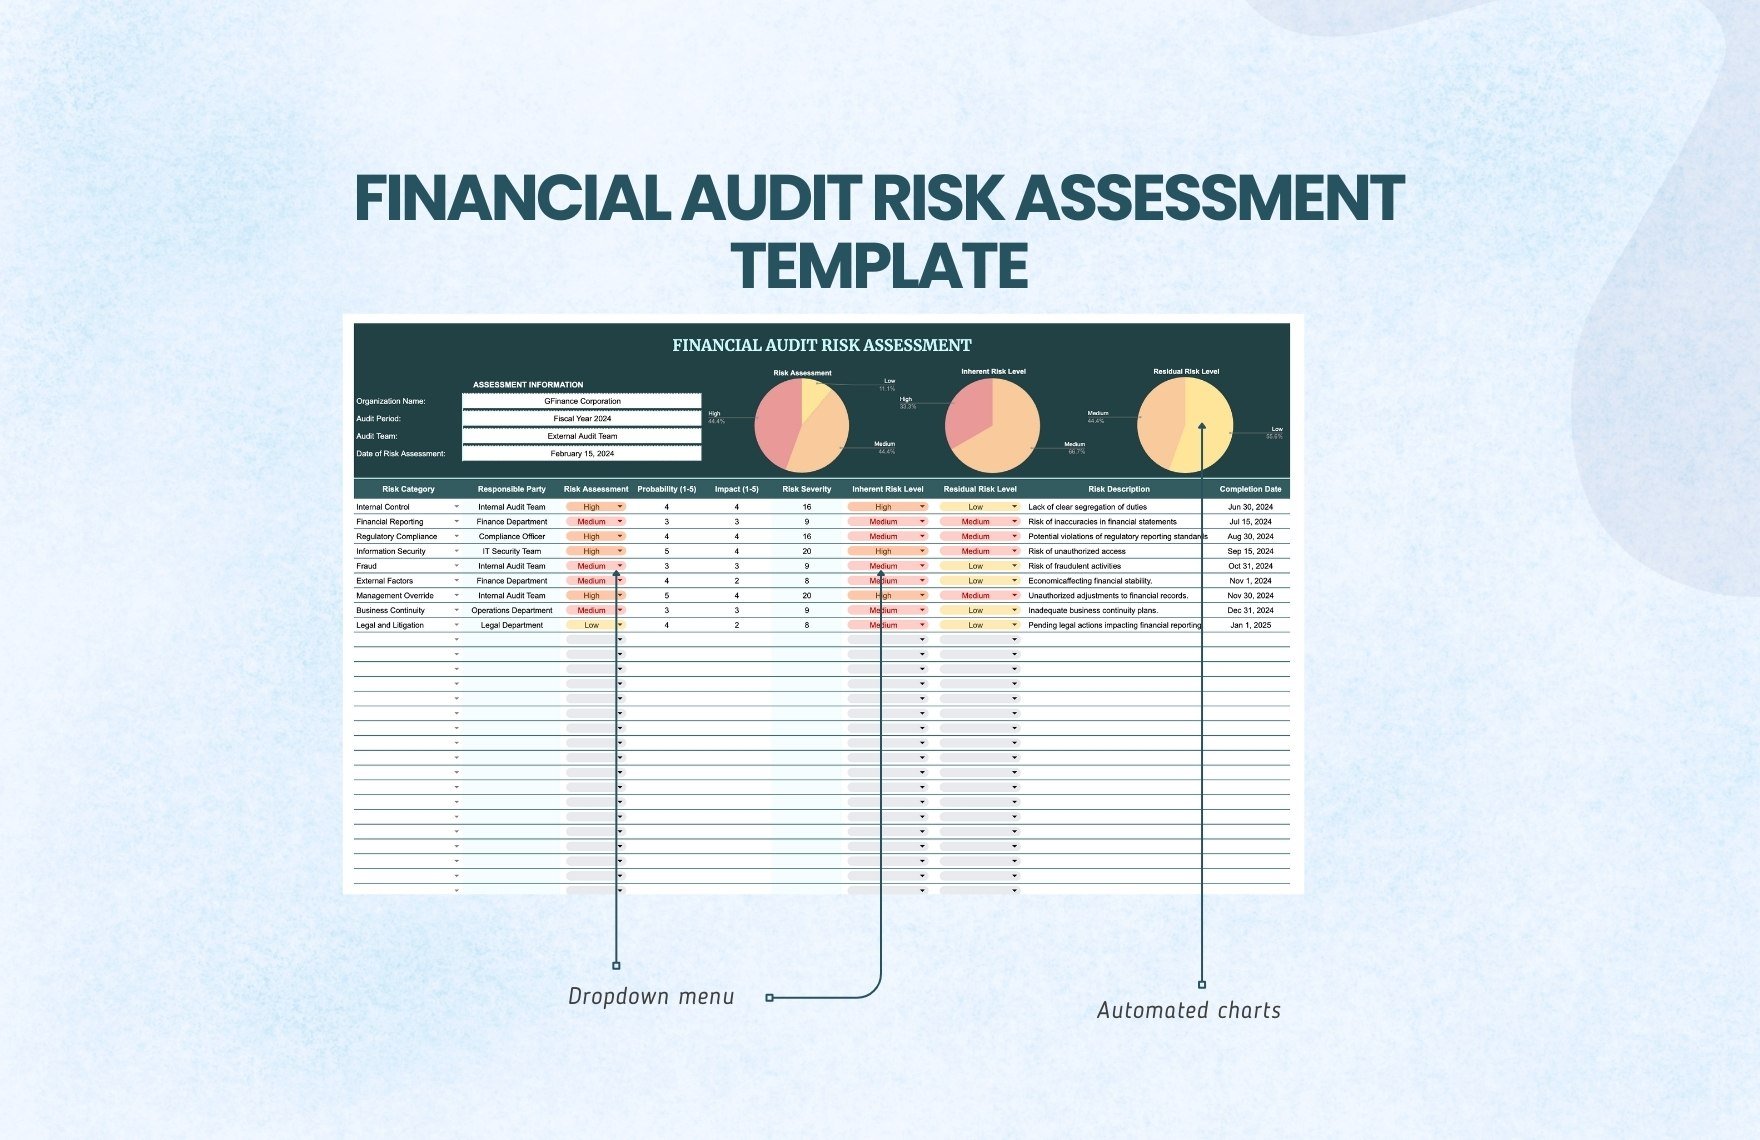
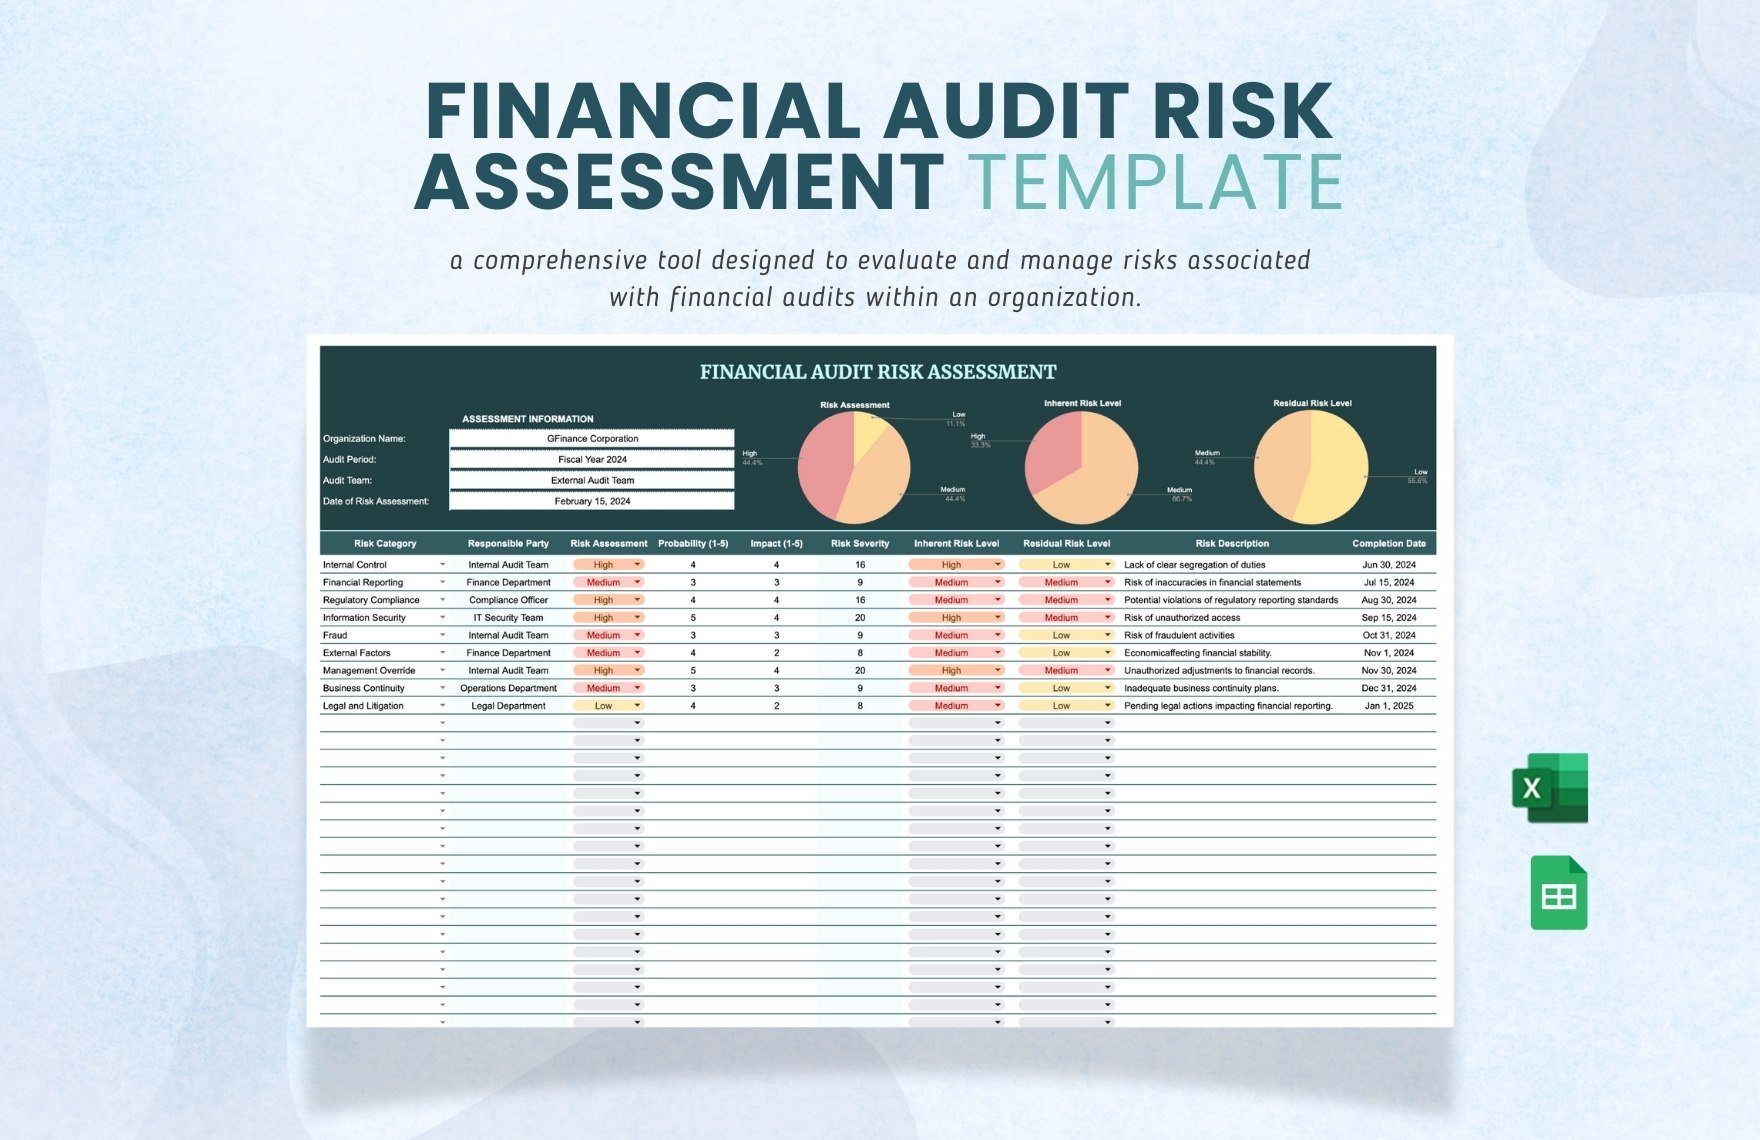
Once you have those dimensions mapped, you can build the template around them. Here's what a functional structure looks like in practice: Column one is the audit area or process name. Column two captures the inherent risk rating with a brief justification — not just "high" but why. Columns three through six handle each risk dimension. Column seven is your composite risk score, calculated by assigning weights to each dimension rather than treating them equally. Column eight is your recommended audit action: full audit, targeted review, monitoring, or accept and revisit later. The weighting matters more than people realize. I usually assign inherent risk at 25 percent, control environment at 25 percent, financial materiality at 20 percent, regulatory exposure at 20 percent, and change velocity at 10 percent. Those percentages aren't laws. Adjust them based on your organization's actual risk appetite. If you're in a heavily regulated industry, regulatory exposure might deserve 30 percent. If you're in a stable environment with mature controls, change velocity might matter more.
Building the Assessment Into Your Audit Cycle
The template is only as good as the process around it. I've seen good templates wasted because they were filled out once per year by a single person who didn't actually work in the areas being assessed. That produces lazy ratings. Here's what works: assemble a panel of three to four people who have direct knowledge of the processes being assessed. This might include the audit manager, a senior auditor, and one or two subject matter experts from inside the business units. Spend two to three hours reviewing each major area together. The friction of discussion improves the output. Someone will push back on a rating, and that's when you catch the assumptions that don't hold up. After the panel rates each area, you calculate composite scores and rank them. Then you cross-reference against your available audit capacity. This is where the plan becomes a plan instead of just an assessment. If you have capacity for twelve weeks of fieldwork and the top-ranked areas require fifteen weeks, you've just identified a resource gap. Document it. Raise it early. It's better to say "we're prioritizing based on risk but can't cover everything" than to quietly skip the important stuff and hope nobody notices.
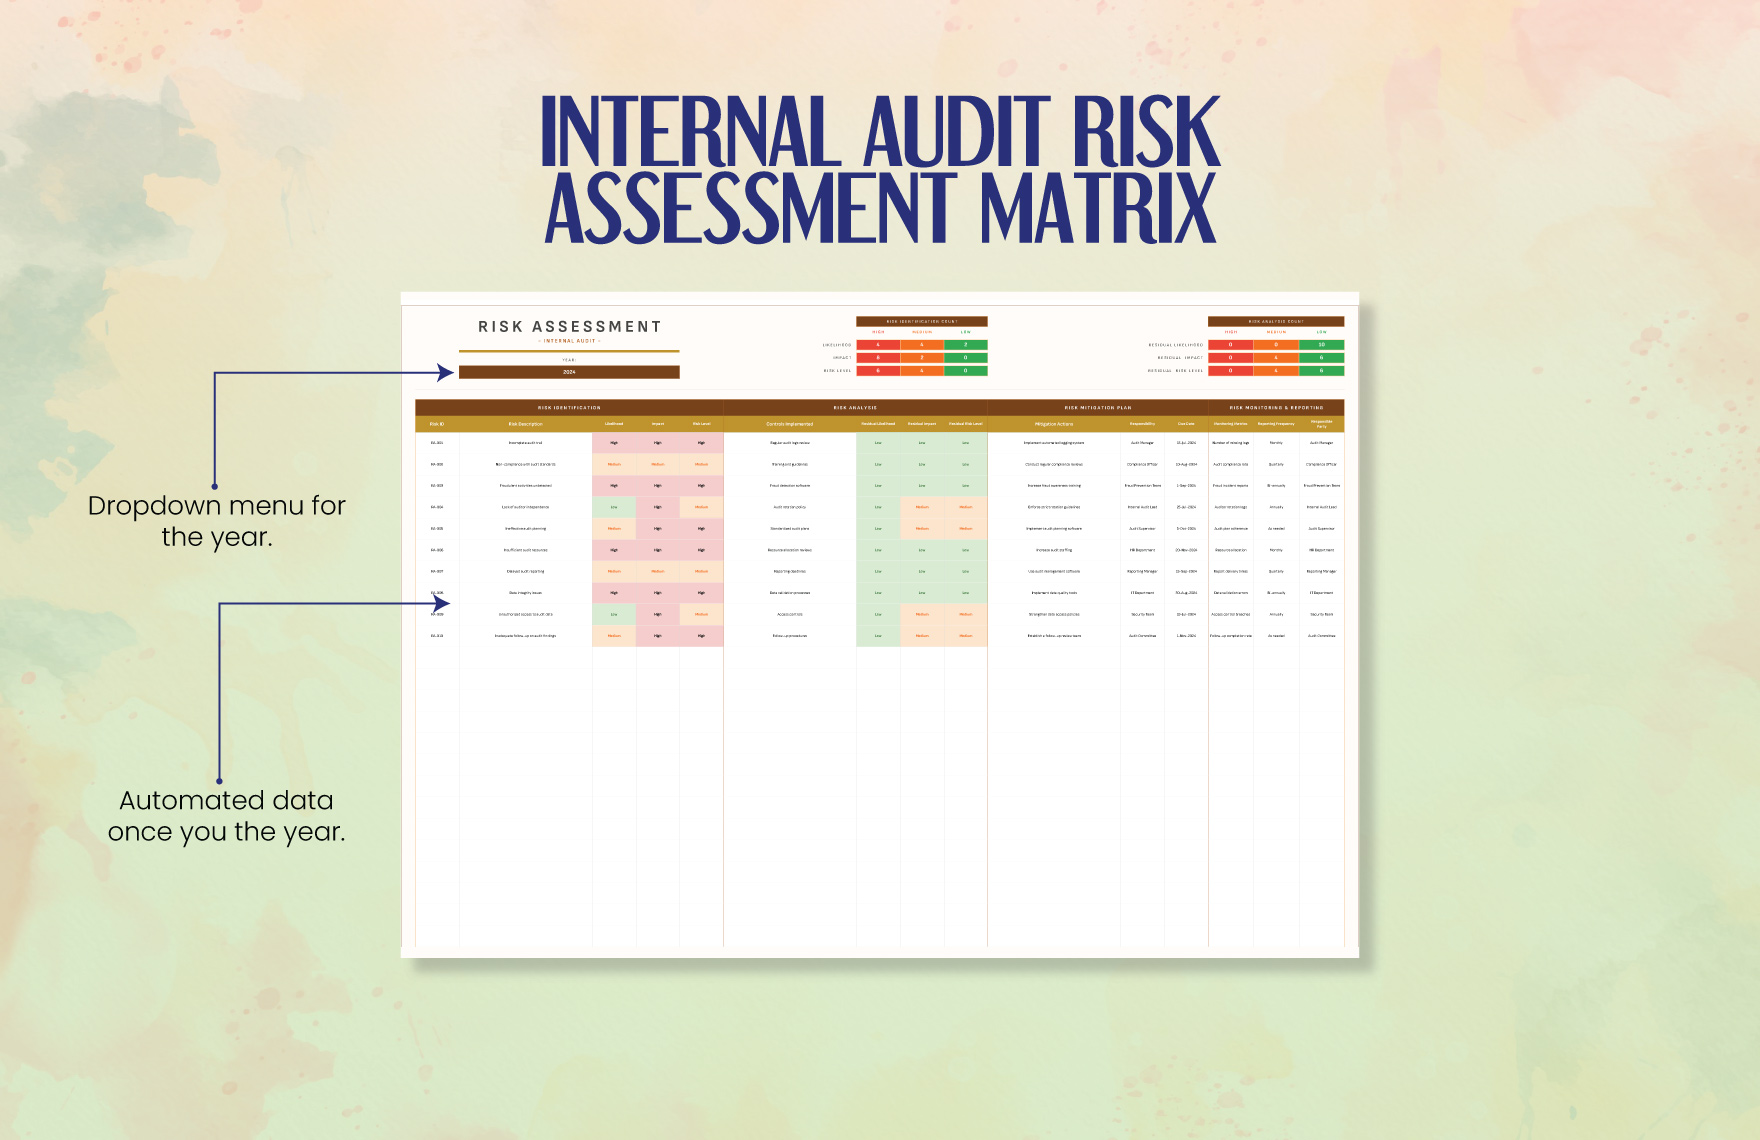
I use a visual matrix for the final output — risk score on the x-axis and audit recommendation on the y-axis. It makes it immediately obvious which areas fall into the "high risk, full audit" quadrant versus the "low risk, monitoring only" zone. Stakeholders respond better to visual evidence than to rows of numbers. One CFO I worked with actually said she could "see the plan" in the matrix and agreed to the resource allocation within five minutes. The same data in a table would have taken twenty minutes of discussion.
Common Pitfalls to Avoid
Rating inflation. When everyone marks everything "medium" or "high," the exercise loses meaning. I enforce a distribution rule: no more than 20 percent of areas can receive the highest rating, and no fewer than 15 percent should receive the lowest. This forces real prioritization. Ignoring qualitative factors. A process might look low-risk on paper but have a key person dependency that nobody documents. I always include a notes column for qualitative factors that don't fit neatly into the scoring system. Management override risk, fraud indicators, and known prior issues all belong there. Static assessments. Risk changes. If you do this once a year and never touch the scores in between, your plan is already stale when it launches. I recommend a mid-year checkpoint — even a brief one — where you update any areas that have experienced significant changes since the original assessment.
Forgetting about the smaller risks. The temptation is to focus entirely on the top five areas. But some audit standards and frameworks require coverage across the board. Build in a minimum coverage requirement — maybe 60 percent of total areas get some form of audit activity, even if it's just a targeted review rather than a full engagement.
What This Template Can't Do
I want to be blunt about the limitations. A risk assessment template cannot replace actual professional skepticism. It cannot compensate for a team that doesn't understand the business it's auditing. And it cannot account for emerging risks that haven't materialized yet — cyber threats, for example, often show up in audits years after they become relevant. The template also assumes you have reliable data to feed it. If your prior audit findings database is incomplete, your control testing history is spotty, or your financial data is outdated, the output will be garbage regardless of how well-structured the template is. I've encountered this at organizations where the risk assessment took longer to validate than to complete because the underlying data wasn't trustworthy. When that happens, the workaround is to spend time on data quality first. Interview process owners. Review recent operational reports. Cross-reference with internal monitoring results. The template should reflect reality, not fill gaps with guesses. A half-hour of research before filling out a risk rating is worth hours of defending a questionable score later.

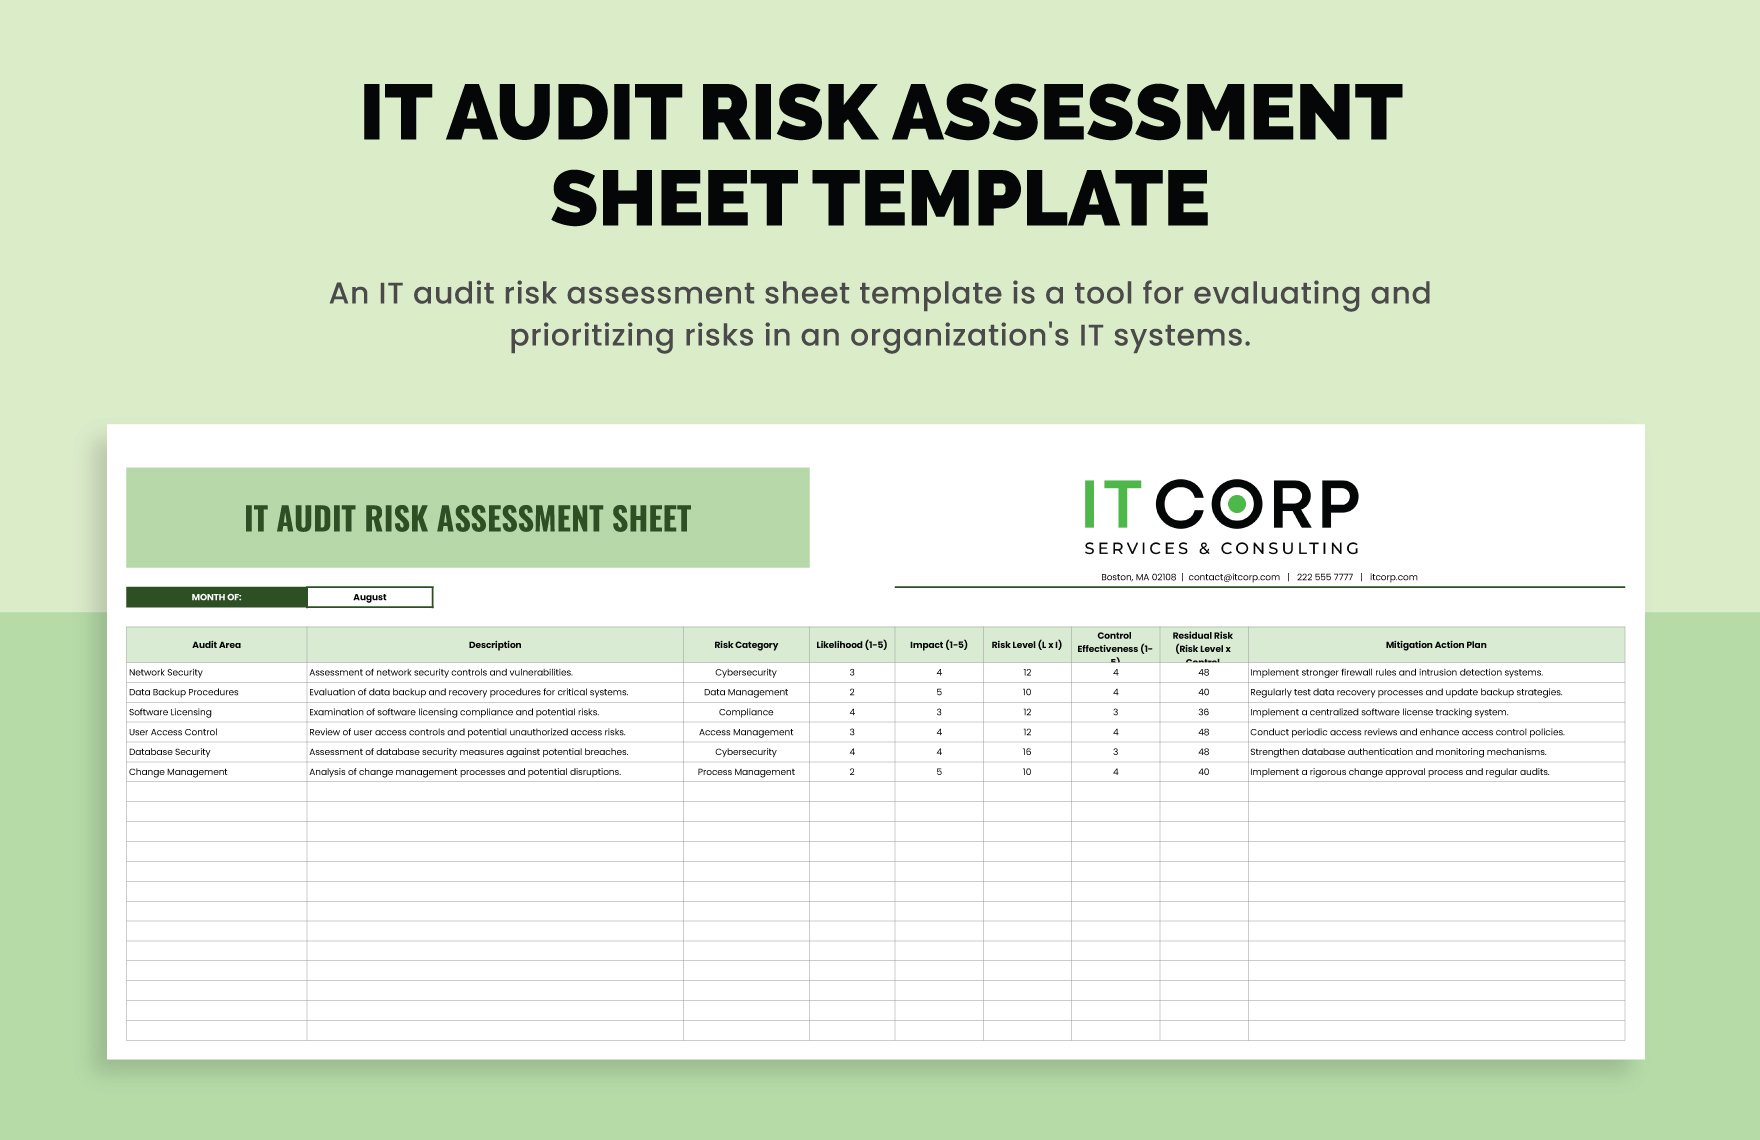
Also worth noting: this approach works well for financial and operational audits. It's less directly applicable to IT audits, where the risk dimensions shift toward things like access governance, change management, and system availability. For those, you'll want a supplemented framework that includes COBIT or NIST risk factors alongside the standard template fields.
Getting Started With Your Audit Plan Risk Assessment Template
If you're building one from scratch, start simple. Three columns for the process name, risk rating, and justification. Add dimensions one at a time as your team gets comfortable with the exercise. Don't try to implement a perfect system on day one. A working imperfect template beats a sophisticated one that sits unused because it's too complex to maintain. The version I use has evolved over several years and about forty assessment cycles. It currently runs about forty fields per process area, which means roughly twenty minutes per area for a prepared panel. That's fast enough to do a thorough annual assessment without burning through the entire planning budget. Slower is possible if you're dealing with particularly complex or unfamiliar areas, but if it takes more than an hour per area, something in your process is inefficient. Keep the output visible. Share drafts with audit committee members early. Get their input on whether the risk levels feel right before you lock the plan. Their perspective might differ from yours, and that's actually useful — it surfaces blind spots you didn't know you had.
The final product should be a single document that contains both the assessment data and the resulting audit plan. Don't let them live in separate files. When someone asks why a particular area got a certain priority, you should be able to point to the exact row and explain the reasoning without digging through multiple sources. If you can't, the template isn't doing its job.