Why Most People Blow Past CISA and Then Can't Actually Audit Anything
I spent six years as an IT auditor before moving into advisory work, and the pattern is always the same. Someone finishes a Certified Information Systems Auditor Training program, gets the certification, and then walks into their first real audit completely unprepared for what it actually looks like when you're not working from a textbook scenario. The gap between passing the exam and being competent in the field is wider than most people expect. Here's what I wish someone had told me before I sat down for my first actual engagement. The CISA exam covers five main domains, and ISACA publishes detailed job practice analysis documents for each one. Domain 1 is auditing information systems, which makes up about 17% of the exam. Domain 2 is governance and management of IT, roughly 17%. Domain 3 is acquisition, development, and implementation of systems, about 14%. Domain 4 is operations, about 29%. Domain 5 is protection of information assets, about 23%. These percentages shift slightly from one cycle to the next, so check the current ISACA outline before you buy anything. The recommended preparation time is usually 150 to 200 hours spread across eight to twelve weeks. That's a rough estimate. If you already work in IT audit, you might get through it faster because much of the language feels familiar. If you come from a development or security background, you'll need more time on the governance and audit methodology pieces. I recommend using at least two question banks. The official ISACA question bank is necessary but not sufficient on its own. Most people score around 60% on the first run through it. That's normal. The material is written to deliberately confuse you by making the most correct answer look wrong and the obviously right answer look like a trap.
What Actually Happens When You Start Auditing
Textbook audit methodology teaches you to follow a strict lifecycle: plan, test, report, follow up. Real audits rarely work that way. You walk into an environment where the documentation is incomplete or intentionally vague, the people you need to interview are either too busy or too defensive, and your deadline was set by someone who has never done an audit before. The training programs don't really prepare you for that. They prepare you for a controlled academic version of the work. My first independent engagement was a SOC 2 Type I audit for a mid-size SaaS company. I had just finished my CISA prep and felt confident. The client's CISO was friendly but the actual system documentation told a completely different story. Their incident response process was documented as a single paragraph in a shared wiki page. Their change management process existed only in the team's heads. I spent the first three days just trying to figure out what actually happened when someone pushed code to production. The official process said pull request review plus automated testing. The reality was that the lead developer merged directly into main during off-hours when nobody was watching. There was no audit trail, no rollback procedure, and no separation of duties between development and production environments. This wasn't something I'd seen in any practice question.
Counter-Intuitive Things About CISA That Beginners Miss
One thing that surprised me repeatedly during my early career is how often the correct audit approach is to do less testing, not more. The exam trains you to want comprehensive coverage. In practice, comprehensive testing without focused risk assessment wastes time and produces noise. A well-scoped audit that examines the right controls deeply will always beat a shallow walkthrough of every control in existence. Pick your five highest-risk areas and test them thoroughly. The remaining controls can be validated with targeted sampling later if time permits. Another thing nobody mentions is how much of CISA is really about professional skepticism without making yourself the enemy. You need to question everything, but you also need people to cooperate with you. The people answering your questions are the ones who will provide the evidence you need. Being aggressive about demanding proof from Day One usually backfires. It's more effective to establish credibility by asking intelligent questions that show you understand their environment, then work backward to the control gaps. This takes longer upfront but produces better evidence overall because people actually share information instead of giving you the sanitized version.
Get the Full Details

Practical Steps for Getting Through the Exam
Buy the official ISACA review manual and the corresponding question bank. Read the manual once quickly just to understand the scope. Then go through it section by section while answering every question in that section. Keep a error log. This is the part most people skip. Write down every question you got wrong and why. Categorize them by domain and by reasoning error. Are you consistently picking the wrong answer because of keywords, because of scope, or because of process? The CISA exam is heavily influenced by ISACA's preferred methodology, which sometimes conflicts with how things actually work in industry. You need to think like ISACA during the exam, not like a practitioner who has seen the messy reality. Spend more time on Domain 4 and Domain 5. These two domains together make up about half the exam. Operations and information protection are where most candidates lose points. They also tend to overlap heavily with CISSP and Security+ material, which can actually hurt you if you're too comfortable with those frameworks. CISA wants you to approach security from an audit and assurance angle, not from a technical implementation angle. A question about encryption is not asking you to choose the best cipher. It's asking you to determine whether the encryption is properly managed, who has access to the keys, and whether the policy aligns with the business risk. Take full-length practice exams under timed conditions at least four times before you sit for the real test. The exam is 150 questions in 4 hours. That's an average of 96 seconds per question. You cannot spend two minutes on a hard question and then rush through three easy ones. You need a consistent pace. My rule of thumb is: answer every question in under 90 seconds on the first pass, flag anything that takes longer, and come back to the flagged questions at the end. This usually gives you enough time for a second review of the difficult items.
Where the Certification Falls Short
Here's the honest part. The CISA certification proves you know ISACA's framework for auditing information systems. It does not prove you can walk into a company and run a credible audit on your own. The exam tests theoretical knowledge, not practical judgment. Several of my colleagues passed CISA and then needed six months to a year of supervised fieldwork before they could be trusted to lead an engagement independently. This isn't a criticism of the certification. It's just a limitation. The exam covers the what and the why, but the how takes real-world experience. Another limitation is that CISA is heavily focused on traditional IT infrastructure auditing. Cloud-native architectures, DevOps pipelines, and continuous deployment models don't fit neatly into the domain breakdown. The 2024 and 2025 exam outlines have added more cloud content, but it's still scattered across multiple domains rather than treated as a coherent subject. If you're auditing modern software delivery environments, you'll need to supplement your CISA knowledge with hands-on experience or additional training in areas like DevSecOps and infrastructure as code auditing. If the goal is purely to get past an HR screen or satisfy a regulatory requirement, CISA works fine. If the goal is to actually become competent at IT audit, treat the certification as a foundation, not a destination. Pair it with real audit work as soon as possible, ideally under someone who has been doing this for at least five years. The difference between an auditor who just knows the framework and one who can actually add value is experience, not exam prep.
A Word on Study Materials and Costs
The official ISACA materials run about $800 to $1,000 total if you include the exam fee, the review manual, and the question bank. You can cut that cost significantly by buying used manuals from previous exam cycles. The core concepts don't change that much year to year. The question bank updates happen annually, but the fundamental framework stays consistent. Third-party question banks like Focus on Pass or CISA Quest cost between $50 and $150 and are worth it if you've already gone through the official material once. Don't rely exclusively on third-party banks. They sometimes get the reasoning wrong or present scenarios that don't align with ISACA's preferred approach. Some people swear by video courses from Udemy or similar platforms. I found those useful for understanding concepts I was struggling with, but I wouldn't substitute them for the question bank. Video courses explain the material. The exam tests your ability to apply the material under pressure. Those are different skills. Practice questions build the right skill for the actual test format. Keep your study schedule realistic. Thirty to forty-five minutes a day on weekdays and two to three hours on weekends is sustainable for most working professionals. Pulling all-nighters before the exam doesn't help. The questions require clear reasoning, and fatigue destroys that. Sleep matters more than the extra hour of cramming. I've seen people who studied consistently for ten weeks perform better than people who crammed for three weeks, even though the crammers knew more facts on exam day. The consistent students had better pattern recognition for the question styles.

After You Pass
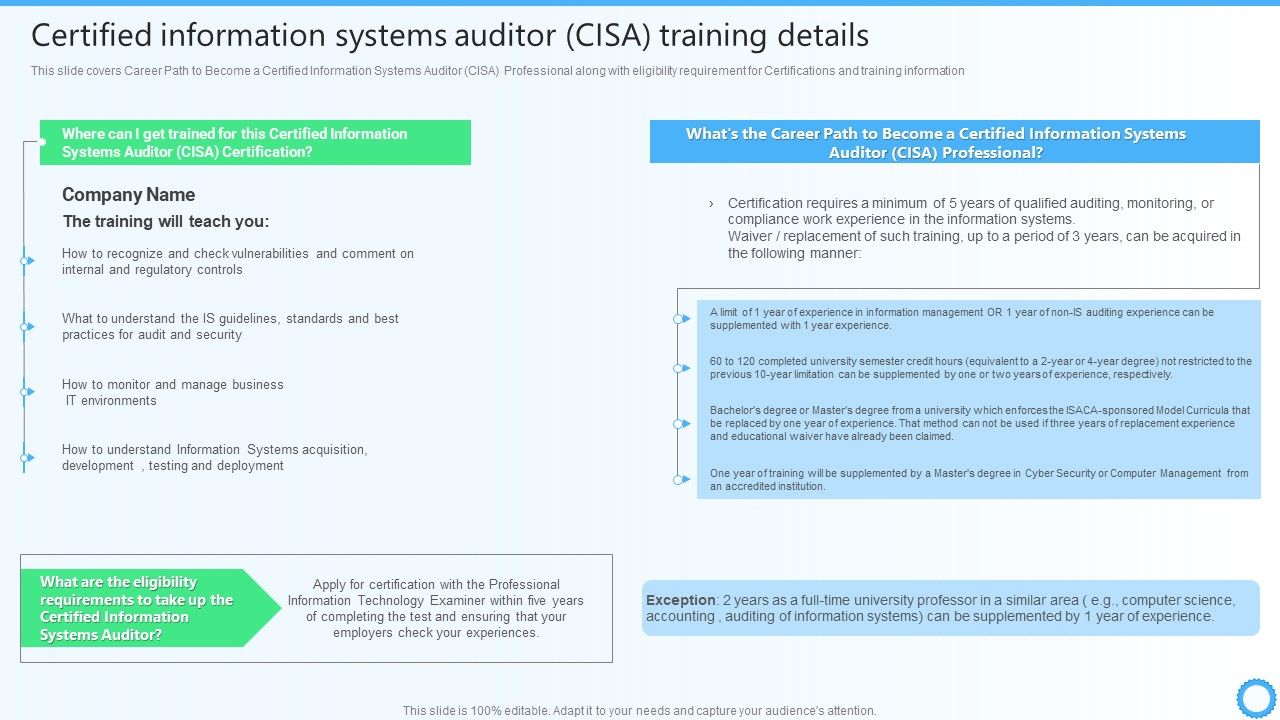
Passing the exam is only step one. You need two years of relevant work experience to actually receive the certification, or you can take the path of waiving one year of experience with certain qualifications. ISACA is fairly flexible about what counts as relevant experience as long as it involves auditing, controlling, monitoring, or overseeing IT systems. Your manager or a designated signatory needs to verify the experience. Keep detailed records of your projects, the controls you tested, and the frameworks you worked within. When you eventually submit your experience application, vague descriptions like "helped with audits" won't cut it. Be specific about what you did and which domain it relates to. Once certified, continuing professional education is required. You need 120 hours of CPE every three years, with a minimum of 20 hours per year. Conferences, webinars, internal training, and even relevant work projects can count toward this. Stay current on framework updates. ISACA releases updates to the CISA handbook and question bank every few years, and the exam content shifts accordingly. Missing that pattern recognition will cost you if you ever need to retake the exam or if you're working on engagements that reference the latest guidance.