What You Need to Know Before You Get a Quote
A cybersecurity assessment isn't a product you can put in a shopping cart. The price range is wide because the work involved varies so much between engagements. A small business with ten endpoints and a cloud-hosted website is a completely different scope than a mid-market company running on-prem servers, VLANs, and custom applications across three locations. When someone asks how much does a cyber security assessment cost, the honest answer starts with "it depends" and then moves into a lot of specific questions. I've done this work for over a decade, and the first thing I always tell people is to expect a discovery phase before any firm will give you a real number. Here's why that matters and what actually drives the price up or down.
How Much Does A Cyber Security Assessment Cost
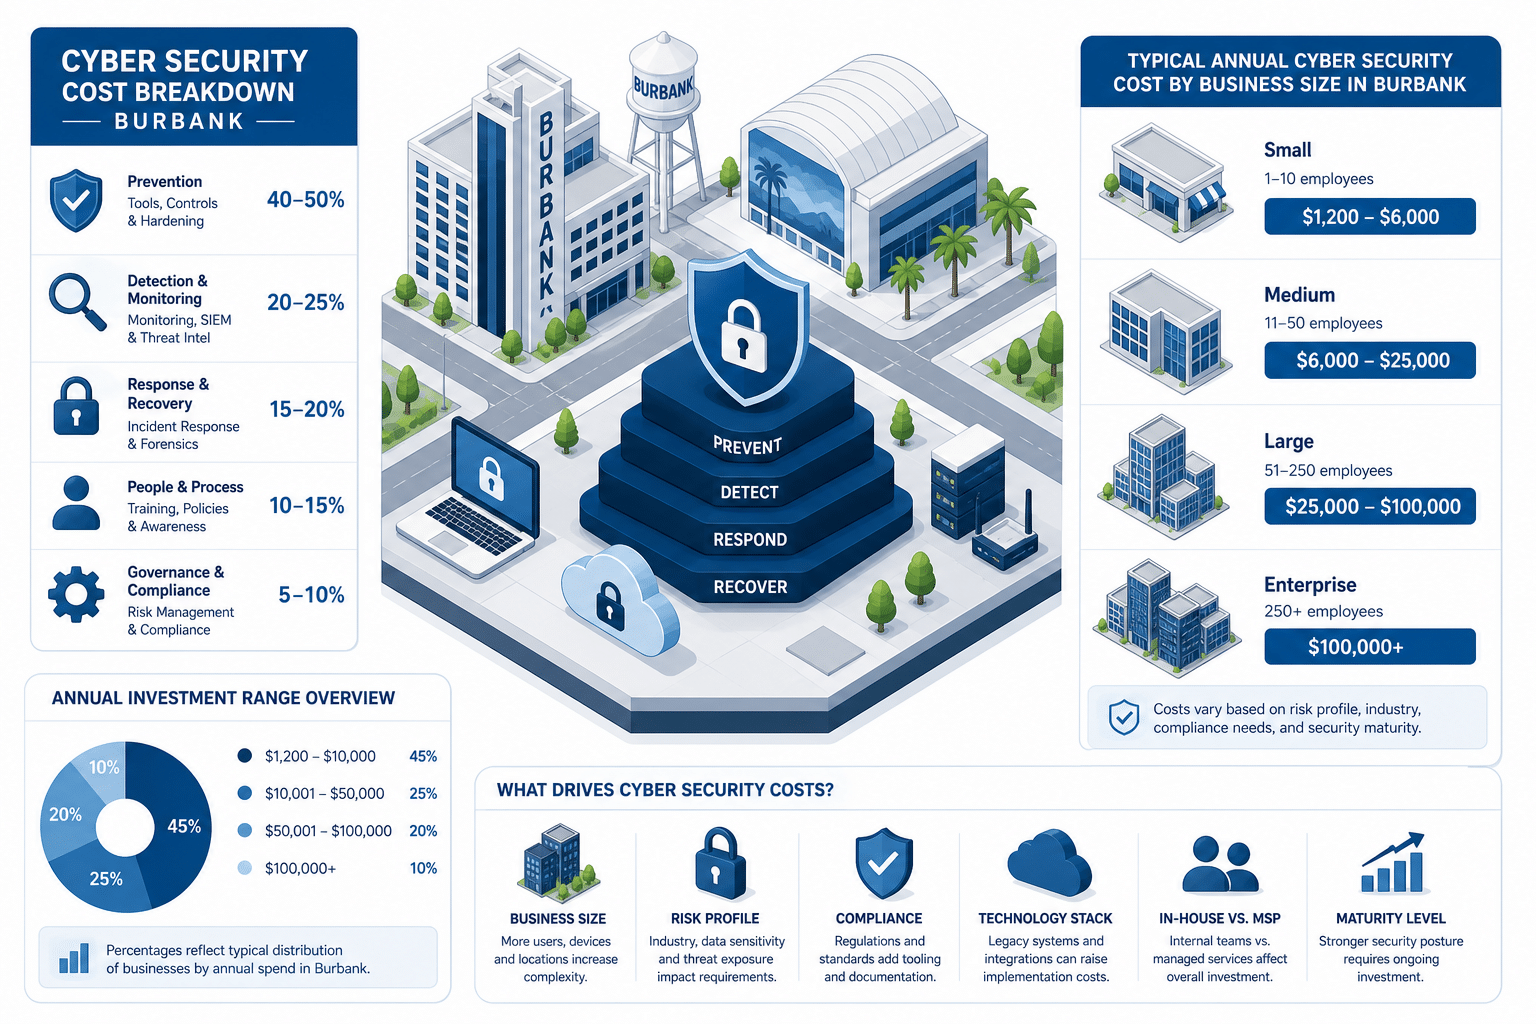
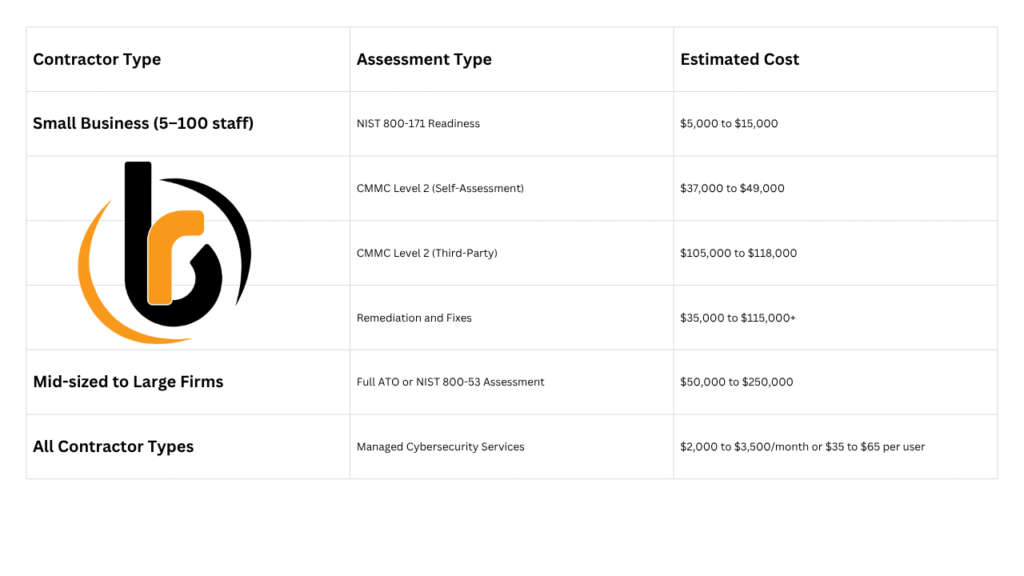
For a basic vulnerability scan and report on a small business with limited infrastructure, you're looking at somewhere between $3,000 and $8,000. That covers a unauthenticated scan of your external attack surface, a quick internal network sweep, and a written summary of findings with recommended remediation priorities. It's not comprehensive by any means, but it's a starting point for organizations that have never had anything like this done before. When you move into a full-scope assessment that includes penetration testing, that range shifts significantly. A standard penetration test for a mid-size organization with maybe fifty to a hundred systems, a few external-facing services, and internal network access testing typically runs between $15,000 and $40,000. The upper end there assumes multiple vectors, social engineering components, and a detailed red team exercise rather than a straightforward black-box test. Enterprise-level assessments with complex application security testing, regulatory compliance mapping, and extensive documentation can easily exceed $75,000 to $150,000 or more. I've seen engagements in the high six figures for organizations subject to strict regulatory requirements where the assessment needed to satisfy auditors from multiple frameworks simultaneously.
The biggest variable nobody talks about enough is the depth of the report and what happens after the testing. Some firms deliver a PDF with bullet points and move on. Others provide a remediation roadmap, follow-up validation scans, and executive-level briefing materials. The latter takes more time and obviously costs more, but it's also what actually moves the needle on security improvement.
Get the Full Details

What Actually Goes Into the Pricing
Several factors determine where your assessment lands in that range, and understanding them helps you evaluate quotes from different firms rather than just comparing bottom-line numbers. Scope definition is everything. How many IP ranges, how many external URLs, how many internal network segments, and which applications need testing. A client of mine once had a quote that seemed reasonable at first glance until we broke down the scope. They wanted testing on their customer portal API, their internal HR system, their VPN concentrator, and their cloud infrastructure all in one engagement. That turned a two-week assessment into something closer to a month of work, and the price reflected that. Testing methodology matters. OWASP-based application testing follows different procedures than a network infrastructure assessment. A combined engagement requires testers with different specializations or a team that can switch between contexts, which increases labor costs. Manual testing always costs more than automated scanning, and that's where the real value usually lives, but it's important to know what you're paying for.
Timeline compression adds cost. If you need a full assessment completed in three weeks instead of six, expect to pay a premium. Most firms have limited availability for assessment work, and squeezing it into a tight window often means pulling from other projects or assigning senior staff who command higher rates.
Where People Get Surprised
One common misconception is that a lower quote is automatically better value. I recently reviewed a proposal from a firm that came in at nearly half the price of two other competitors for what appeared to be the same scope. The catch was that the cheaper engagement excluded manual penetration testing and relied entirely on automated vulnerability scanning with a human reviewing the output. For a basic health check, that might be adequate. For an organization that needs to demonstrate due diligence to regulators or insurers, it falls short quite quickly. Another surprise comes from out-of-scope items that get discovered during the assessment. A penetration tester might find a misconfigured server that wasn't in the original scope but is clearly part of your infrastructure. Proper engagement agreements address this through change order processes, but if your contract doesn't account for that possibility, you can end up with scope creep discussions mid-assessment or a final report that deliberately omits findings outside the agreed boundaries. I learned this the hard way on a project a few years back. The client's network diagram showed twelve systems in scope, but during the internal assessment phase, the tester found an entire subnet with fifteen additional servers that the IT team had forgotten to include. Those servers were running outdated versions of critical software with known vulnerabilities. The engagement contract didn't have a clear process for adding scope, so we spent two days in meetings trying to figure out whether those systems should be tested or just noted in a separate findings document. In the end, we added them through a formal change order, but it delayed the final report by a week and cost the client an additional $4,000 in testing fees that nobody mentioned upfront. Now I always make sure our initial scoping calls dig into every system, even the ones the client thinks are irrelevant.
How to Evaluate a Quote Properly
Don't just compare total prices. Look at what's included and, more importantly, what's excluded. A quote that seems expensive might actually be better value if it includes remediation validation, executive briefing support, and a thirty-day post-assessment email window for follow-up questions. A cheap quote might exclude all of that and leave you spending more later trying to fill the gaps. Ask about the team composition. Who actually performs the testing, and what are their certifications? CISSP, OSCP, and similar credentials indicate a baseline of professional development, but they don't guarantee quality. What matters more is whether the people doing the work have hands-on experience with environments similar to yours. A tester who has only worked with Windows environments will miss nuances in a Linux-heavy infrastructure, and vice versa. The reporting quality is where most cheap assessments fail. A well-written report translates technical findings into business risk. It tells you what matters, what doesn't, and what to fix first. A sloppy report dumps a hundred findings into a spreadsheet with minimal context and leaves your team to figure out priorities on their own. I've seen security teams waste weeks chasing low-severity findings from poorly scoped reports while critical vulnerabilities went unaddressed because the risk context was missing.
Hidden Costs to Plan For
Beyond the assessment fee itself, there are a few costs that aren't always obvious up front. Remediation of findings is the biggest one, and it can easily equal or exceed the cost of the assessment depending on what's discovered. A single unpatched vulnerability might cost a couple hundred dollars to fix, but a compromised authentication system or a misconfigured firewall rule could require architecture changes that run into the tens of thousands. Reassessment costs are another consideration. Most firms include one round of validation testing within thirty days of the initial assessment at no additional charge, but if you need to bring them back after a larger remediation cycle, that's usually a separate engagement at a reduced rate. Factor that into your budget planning rather than treating it as an unexpected expense. Regulatory compliance mapping, if you need it for SOC 2, HIPAA, PCI DSS, or other frameworks, may come as an add-on service. Some firms include basic framework alignment in their pricing, but detailed compliance reporting that an auditor can review typically costs extra. Clarify this during the quoting process so there are no surprises.
When a Cheaper Option Makes Sense
There are situations where investing less in the initial assessment is reasonable. A startup with a simple web application and no sensitive data processing doesn't need a $40,000 penetration test to get started. A lightweight vulnerability assessment paired with good configuration management and a regular patching schedule might be all that's needed at that stage. Annual assessments for smaller organizations don't always need to match the depth of an initial assessment. If you've already identified your critical systems and established remediation processes, a follow-up assessment can focus on verifying that those processes are working and checking for new exposure points. That narrower focus justifies a lower cost. But don't confuse cost reduction with neglect. The cheapest possible assessment is often the most expensive mistake you can make, because it gives you a false sense of security while actual vulnerabilities remain unaddressed. I've reviewed assessments from discount providers where the testing was so superficial that a basic port scan was passed off as a complete security evaluation. That's not an assessment. That's a scan report with a cover page.

Get the scope right. Understand what you're paying for and what you're not. And remember that the real cost of a cybersecurity assessment isn't the invoice from the testing firm, it's what you do with the findings afterward. An expensive assessment with ignored recommendations costs your organization more than a moderately priced one with actionable results and a clear path forward.