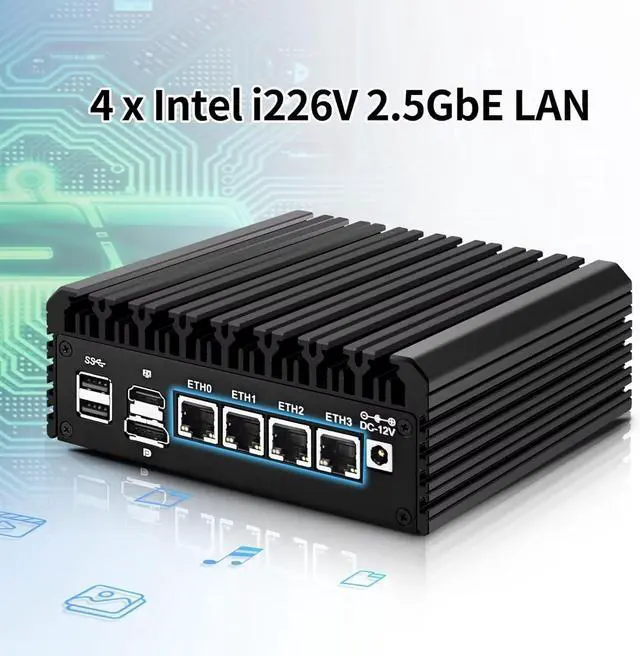
Setting Up a Pico Pc N6005 Mini Firewall Router
I picked up an N6005 mini PC about a year ago to replace a aging MikroTik RB4011 that was barely keeping up with my fiber line. The Intel N6005 is a quad-core Jasper Lake chip that pulls maybe 10-15 watts under load. It's more than enough for a home or small office firewall, but you need to know what you're doing before you just slap pfSense on it and expect everything to work smoothly. The first thing people mess up is the network card assignment. This chip has integrated Intel I210 NICs. pfSense handles them fine, but if you've got a motherboard with additional Realtek or Intel ports from an expansion card, getting them recognized in the right order can take 20-30 minutes of trial and error. I spent an evening on mine because the third port kept being assigned as lan3 instead of wan2. The fix was just going into System > Advanced > Network Interfaces and manually renaming the interfaces based on their MAC addresses. It's not intuitive but it works. For the OS, I'd go with OPNsense over pfSense at this point. Same hardware support, but the UI is faster and the developer team is more active. Install it on a proper SSD, not an SD card or eMMC if you can avoid it. The N6005 boards usually have one M.2 slot. Put your OS drive there and make sure it's a decent quality NAND drive. Cheap drives will cause issues with state table logging after a few months of heavy NAT traffic.
Here's something most guides don't mention: the N6005's integrated graphics (Intel UHD) can cause boot hangs on some OPNsense versions if you don't disable the console output correctly. During install, when you get the bootloader prompt, add hint.vtrrb.0.disabled="1" to your kernel boot parameters. Without this, you might see the system appear frozen at the login screen even though it's actually running fine. You can SSH in to verify. Takes about 5 minutes to confirm and saves a lot of head-scratching. Networking setup in practice: I run mine with 200 Mbps symmetrical fiber. Throughput clocks in around 180-190 Mbps with stateful firewall rules active, which is acceptable but not spectacular. The bottleneck isn't the CPU - it's the single gigabit I210 controller. If you need higher throughput, you'll want to add a second NIC. A $15 Intel I350-T4 used on eBay will give you another two gigabit ports and pushes your potential throughput up to around 500-600 Mbps with the N6005 still having plenty of headroom. That card shows up as bge in FreeBSD-based distros and works plug-and-play with OPNsense. Firewall configuration basics are straightforward. Set your WAN interface to your ISP connection and enable synthetic interface tags if you're doing VLAN tagging from your modem. Most people run their modem in bridge mode, which is the right call. I recommend immediately setting up an Outbound NAT mode to "Automatic" rather than manual unless you have a specific reason not to. The automatic mode handles the typical residential CGNAT scenario without requiring you to understand RFC 1918 overlap rules.
One thing that caught me off guard: the N6005's power supply quality matters more than you'd think. The bare-minimum 65W USB-C adapters that come with some of these boards don't provide clean power under sustained network load. I noticed my firewall would occasionally drop connections during heavy download periods when using the stock adapter. Swapping to a quality 90W USB-C PD adapter eliminated those drops entirely. It's a $20 fix that I wish I'd known about before troubleshooting what I thought was a driver issue for about three days. For VPN throughput, don't expect to push more than 100-120 Mbps through WireGuard on this chip. AES-NI isn't present on the N6005, so encryption falls to software. If VPN speed matters to you, this is where the platform shows its limits. OpenVPN would be even slower, closer to 40-60 Mbps. For a home user running a WireGuard tunnel to a VPS or just remote access, it's fine. For anything beyond that, you'd want something with an X5 or higher Apple Silicon-class instruction set support, or an AMD-based mini PC instead. DHCP and DNS caching work well on this hardware. I have about 30 devices on the network and dnsmasq handles it without breaking a sweat. The real advantage here is the low power draw - my total system draws about 12-18 watts idle and maybe 25-30 watts under heavy firewall load. That's roughly $15-20 per year in electricity at average US rates, compared to maybe $80-100 for a traditional mini router with an older Celeron or Atom processor.
Get the Full Details

If you end up needing more than 1 Gbps WAN throughput, more than 4 NIC ports, or heavy VPN traffic, look at an N5105 or N6000-based board instead. They give you similar form factors but with noticeably better networking performance. The N6005 is a sweet spot for light-to-medium use, not a universal replacement for anything with more demanding requirements. Build it properly, give it a good power supply, and it'll run for years without issues.