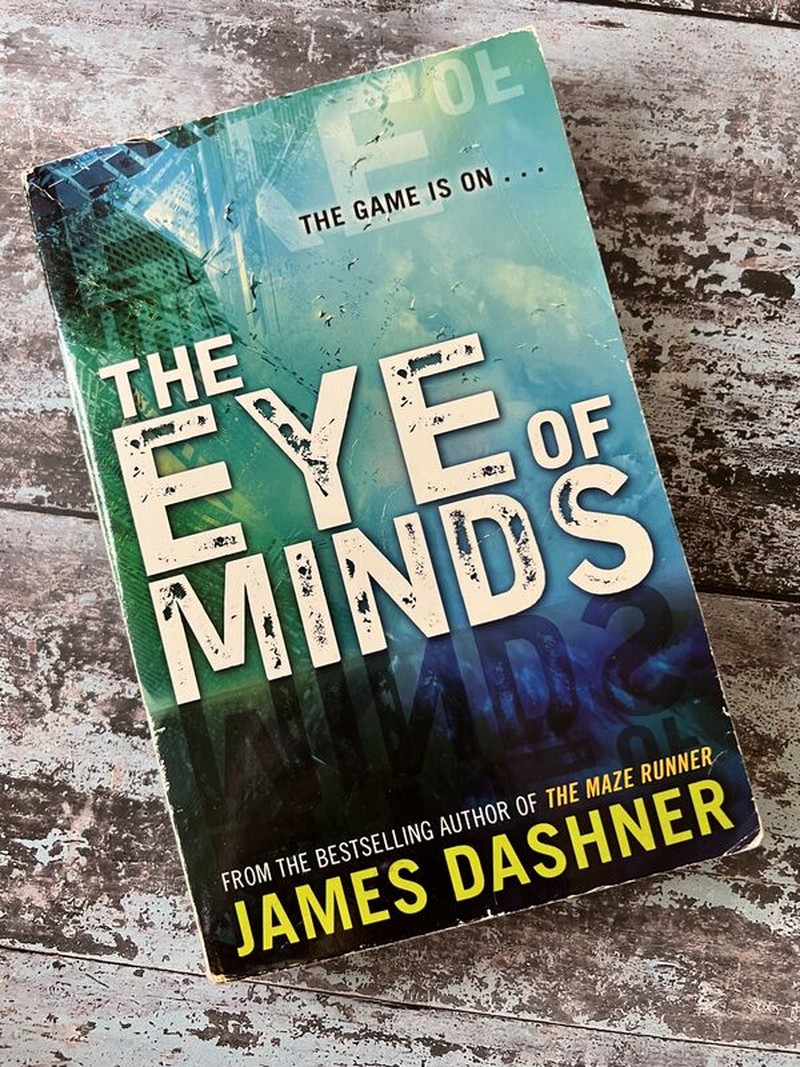
A Practical Guide to Getting Through The Eye Of Minds By James Dashner
I spent last weekend reading this book while simultaneously debugging a Python script that refused to cooperate. The two activities turned out to be more similar than I wanted them to be. That is partly why I am writing this. Not as a review. More as a map for people who want to actually engage with the ideas in it rather than just power through the pages. The Eye Of Minds By James Dashner is a novel, yes. It follows a teenager named Michael who gets pulled into a massively multiplayer online game world where his physical body is in danger. The book tries to make you care about the underlying technology, not just the plot. That intention is noble. The execution has some structural problems you need to work around.
What you need before you start reading
You do not need a computer science degree. You do need a baseline understanding of how networks work at all. Not deep networking theory. Just enough to know what a server, a client, and a firewall actually mean. If you have never heard the word encryption, or if you think it means something related to locking your phone, you are going to hit a wall around page sixty and you will not enjoy it. I learned this the hard way. The first time I picked up Dashner's follow-up book, Rules Of Escape, I had zero context for the tech terms and just skimmed through entire chapters. I came back to it three years later after taking a web development course, and suddenly everything that was vague became specific. The same applies here. Expect to pause every twenty pages and look something up. It will take you from about six hours to maybe eight, but you will actually retain information instead of forgetting it all by chapter twelve.
How the book is actually structured
Dashner does not write a traditional linear thriller. The narrative fractures between Michael's POV inside the virtual world and sections that explain hacking, code injection, and social engineering as if they are action scenes. The book assumes you will read these technical passages at the same speed as the chase sequences. You will not. That is normal. The workaround I use is simple. When a technical passage runs longer than a paragraph and starts explaining something you already know, skip ahead to the next dialogue block. Come back to it later. The book references the same concepts repeatedly across chapters anyway. Reading about SSH key authentication once is annoying. Reading about it three times across three different narrative contexts actually makes it stick.
Get the Full Details
What the book gets right that most people miss
Here is the thing that separates this from generic YA techno-thrillers. Dashner understands that the scary part of cybersecurity is not the hacker in the hoodie typing furiously. It is the mundane failure of basic hygiene. The book keeps coming back to this point. Password reuse. Outdated software. Phishing that works because it is boring and generic. Most readers miss this. They focus on the dramatic hack scenes and forget that the actual lesson is that most breaches happen because someone reused their Netflix password on a sketchy forum. I actually changed my password manager strategy after reading the first twenty pages. Not because the book told me to. Because the scenario in chapter three was something I had casually dismissed before reading it.
Where the book fails and what to do instead
The cryptography scenes. They are fictionalized to the point of being misleading if you take them seriously. The book treats encryption like a puzzle you solve with a keystroke. Real penetration testing involves patience, enumeration, and boring reconnaissance that takes days. If you finish this book thinking cybersecurity is mostly about dramatic code battles, you are setting yourself up for disappointment. The alternative here is straightforward. Pair the book with a practical resource. Try a beginner CTF platform like PicoCTF or OverTheWire's Bandit wargame. These give you actual hands-on experience with the concepts the book gestures toward. The book is fiction. The wargames are where you practice. Another limitation. The social engineering portrayed in the later chapters relies heavily on the protagonist having skills he has not earned yet. Dashner shortcuts the learning curve because the plot demands it. In reality, you cannot convincingly impersonate a sysadmin over the phone after reading one article. It takes repeated practice and studying human psychology over months, not a single scene in a book.
Practical reading strategy that actually works
Read it in small sessions. Thirty minutes maximum before stopping to check something. I know that sounds slow. The book is only about three hundred pages. But Dashner crams a lot of technical vocabulary into a relatively thin narrative, and skimming ruins the whole thing. The book rewards close reading because the clues are embedded in the technical descriptions. If you skim past how Michael bypasses that firewalls, you miss the actual method he uses, which Dashner repeats in a slightly modified form later. I also recommend reading it with a notebook open. Not for summarizing. For writing down the technical terms you do not know and checking them between chapters. The list of unknown terms shrinks dramatically after the first half. By chapter eight, you are spending maybe five minutes per session looking things up instead of twenty.
Who should read this and who should skip it
If you are already into cybersecurity, this book will feel obvious. Read it for the narrative. If you are completely new to the subject, read it but expect to pause frequently. If you are looking for a purely action-driven book with zero technical substance, this is not it. The technical content is the point. Sometimes it works. Sometimes it drags. That is just how it is. I read it on a Tuesday afternoon and spent the next four hours watching cybersecurity tutorials on YouTube instead of finishing the book. The book did that to me. That is either a good thing or a waste of time, depending on what you want from fiction. You probably know which category you fall into.